How SOC Analysts Save 28 Minutes Per Alert Review
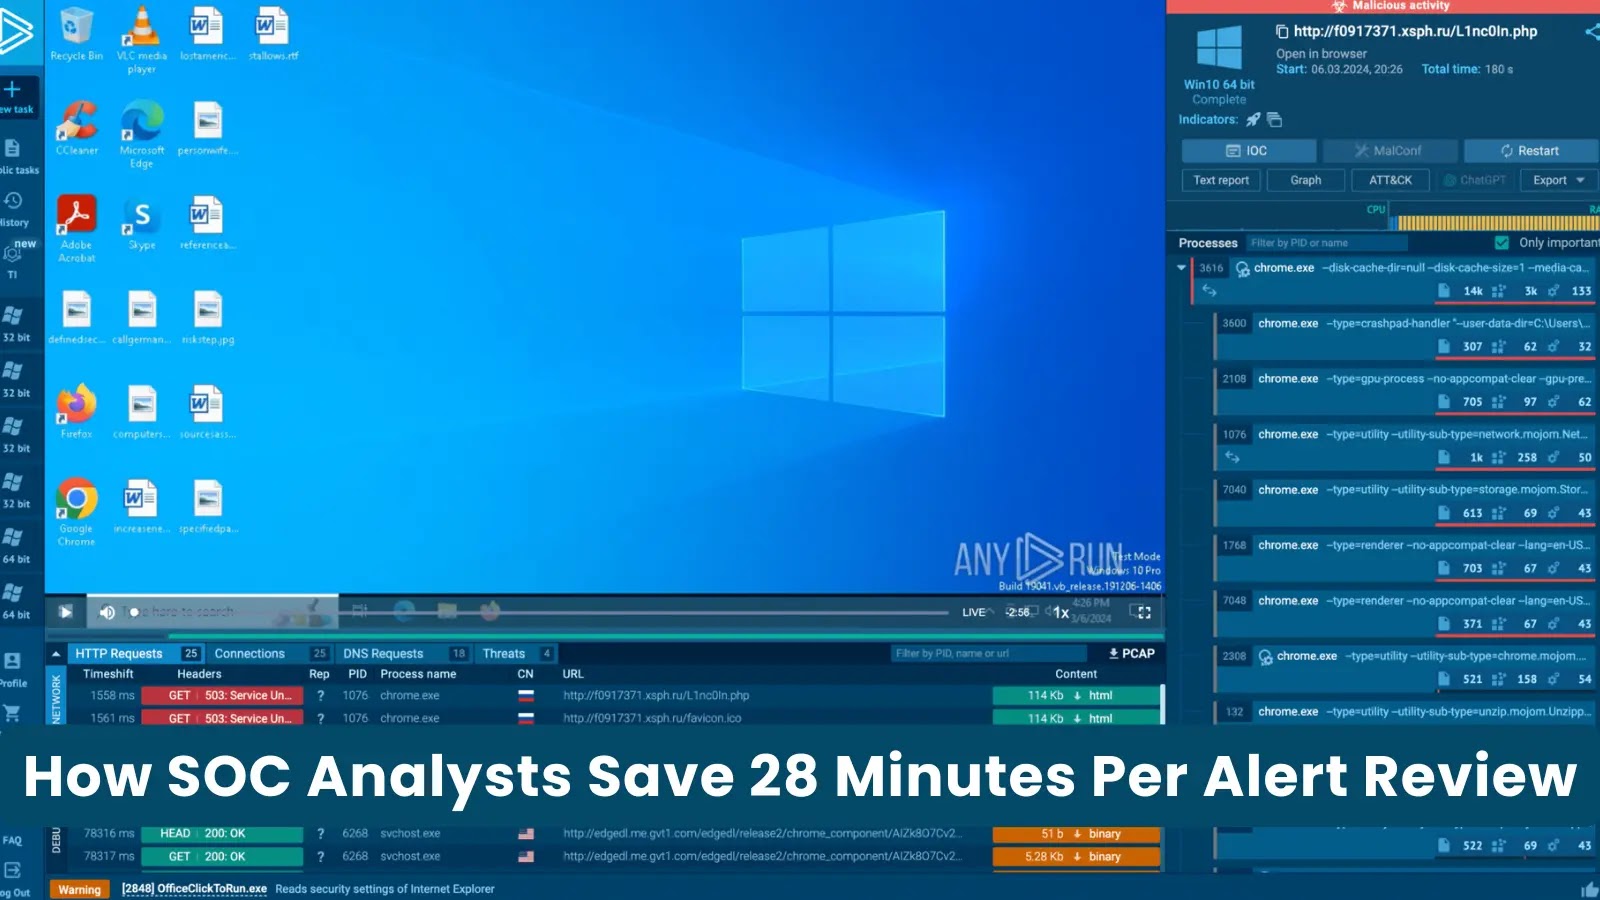
SOC analysts alert review How much time do you spend reviewing alerts that turn out to be harmless? In many teams, a single alert takes…
SOC analysts alert review How much time do you spend reviewing alerts that turn out to be harmless? In many teams, a single alert takes…
SolarWinds Serv-U Vulnerabilities An urgent security update has been released for the Serv-U file server software to fix multiple critical vulnerabilities that could allow attackers…
Threat actors are always looking for new ways to abuse trusted platforms, and Microsoft Entra ID is increasingly becoming a target through a technique known…
Microsoft Extends DLP Support Copilot Purview Data Loss Prevention (DLP) controls are being expanded to block Microsoft 365 Copilot from processing sensitivity-labeled files across all…
CISA Confirms Exploit FileZen Vulnerability U.S. authorities have confirmed that threat actors are actively exploiting a critical vulnerability in FileZen by Soliton Systems K.K.. Due…
Microsoft Stop Support Windows Server 2016 and Windows 10 2016 Organizations are being reminded that three Windows releases first introduced in 2016 are nearing end-of-support.…
Microsoft Released Updates Windows 11 25H2 and 24H2 An optional non-security update, KB5077241, has been released for Windows 11 versions 25H2 and 24H2, improving overall…
A coordinated attack campaign is actively targeting software developers through malicious repositories disguised as legitimate Next.js projects and technical assessment materials. The attackers rely on…
Vulnerabilities in CPSD CryptoPro Secure Disk for BitLocker Multiple vulnerabilities have been discovered in CryptoPro Secure Disk (CPSD) for BitLocker, a widely used encryption solution.…
A critical vulnerability in Apache ActiveMQ has been actively exploited by threat actors, leading to a full LockBit ransomware deployment across an enterprise network. Attackers…
GitHub Copilot Exploited A critical AI-driven vulnerability in GitHub Codespaces, dubbed RoguePilot, that enabled attackers to silently hijack a repository by embedding malicious instructions inside…
The U.S. Department of the Treasury’s Office of Foreign Assets Control (OFAC) on February 24, 2026, designated Russian national Sergey Sergeyevich Zelenyuk and his St.…