Nissan Discloses Data Breach Linked to Compromised Red Hat Infrastructure
Nissan Motor Co., Ltd. has disclosed a significant data breach affecting approximately 21,000 customers of Nissan Fukuoka Sales Co., Ltd. following unauthorized access to a…
Nissan Motor Co., Ltd. has disclosed a significant data breach affecting approximately 21,000 customers of Nissan Fukuoka Sales Co., Ltd. following unauthorized access to a…
A 29-year-old Bangladeshi man has been indicted on federal charges for operating online marketplaces that sold fraudulent identity document templates to customers worldwide, U.S. authorities…
Microsoft Teams users worldwide experienced significant service disruptions on December 20, 2025, as the collaboration platform encountered widespread issues affecting messaging functionality and other critical…
The Shadowserver Foundation has identified over 25,000 internet-facing Fortinet devices globally with FortiCloud Single Sign-On (SSO) functionality enabled, raising concerns about potential exposure to critical…
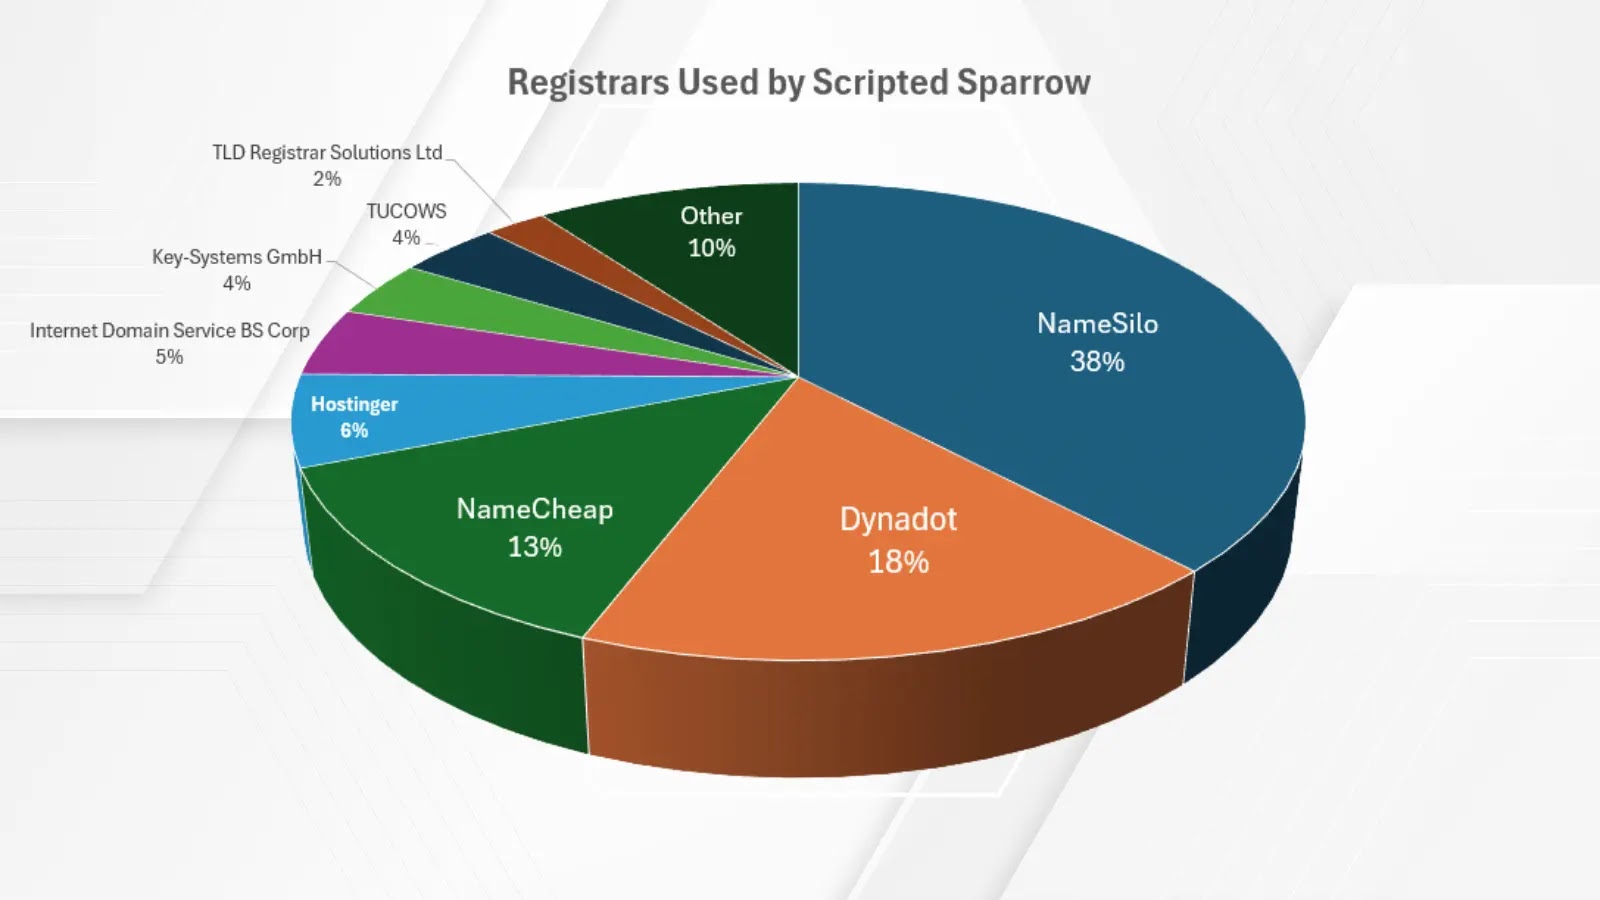
Scripted Sparrow, a prolific Business Email Compromise (BEC) collective with members spanning three continents, has raised significant concerns among cybersecurity researchers due to the sophisticated…
Elastic has released critical security updates to address a dangerous cross-site scripting (XSS) vulnerability affecting multiple versions of Kibana. The vulnerability, tracked as CVE-2025-68385, allows…
Iranian state-sponsored threat actors, previously thought to have gone dormant, have resurfaced with sophisticated new malware campaigns targeting critical infrastructure organizations globally. A new research…
The Apache Software Foundation has released a critical security update for its widely used Log4j logging library. A newly discovered vulnerability, tracked as CVE-2025-68161, allows attackers…
A critical remote code execution vulnerability in Gladinet Triofox is now under active exploitation by threat actors, and security researchers have demonstrated that weaponizing the…
The Cloud Atlas threat group, active since 2014, continues to pose a significant risk to organizations in Eastern Europe and Central Asia through sophisticated attacks…
In mid-September 2025, the ransomware landscape witnessed a significant development when DragonForce announced an alliance with Qilin and LockBit on a Russian underground forum. The…
Russian state-sponsored threat group BlueDelta has conducted a sustained credential-harvesting campaign targeting users of UKR.NET, one of Ukraine’s most popular webmail and news services, between…