Critical MCP Server Flaw Exposes Over 3,000 Servers and Thousands of API Keys
A critical vulnerability in Smithery.ai, a popular Model Context Protocol (MCP) server hosting service, exposed over 3,000 AI servers and thousands of API keys to…
A critical vulnerability in Smithery.ai, a popular Model Context Protocol (MCP) server hosting service, exposed over 3,000 AI servers and thousands of API keys to…
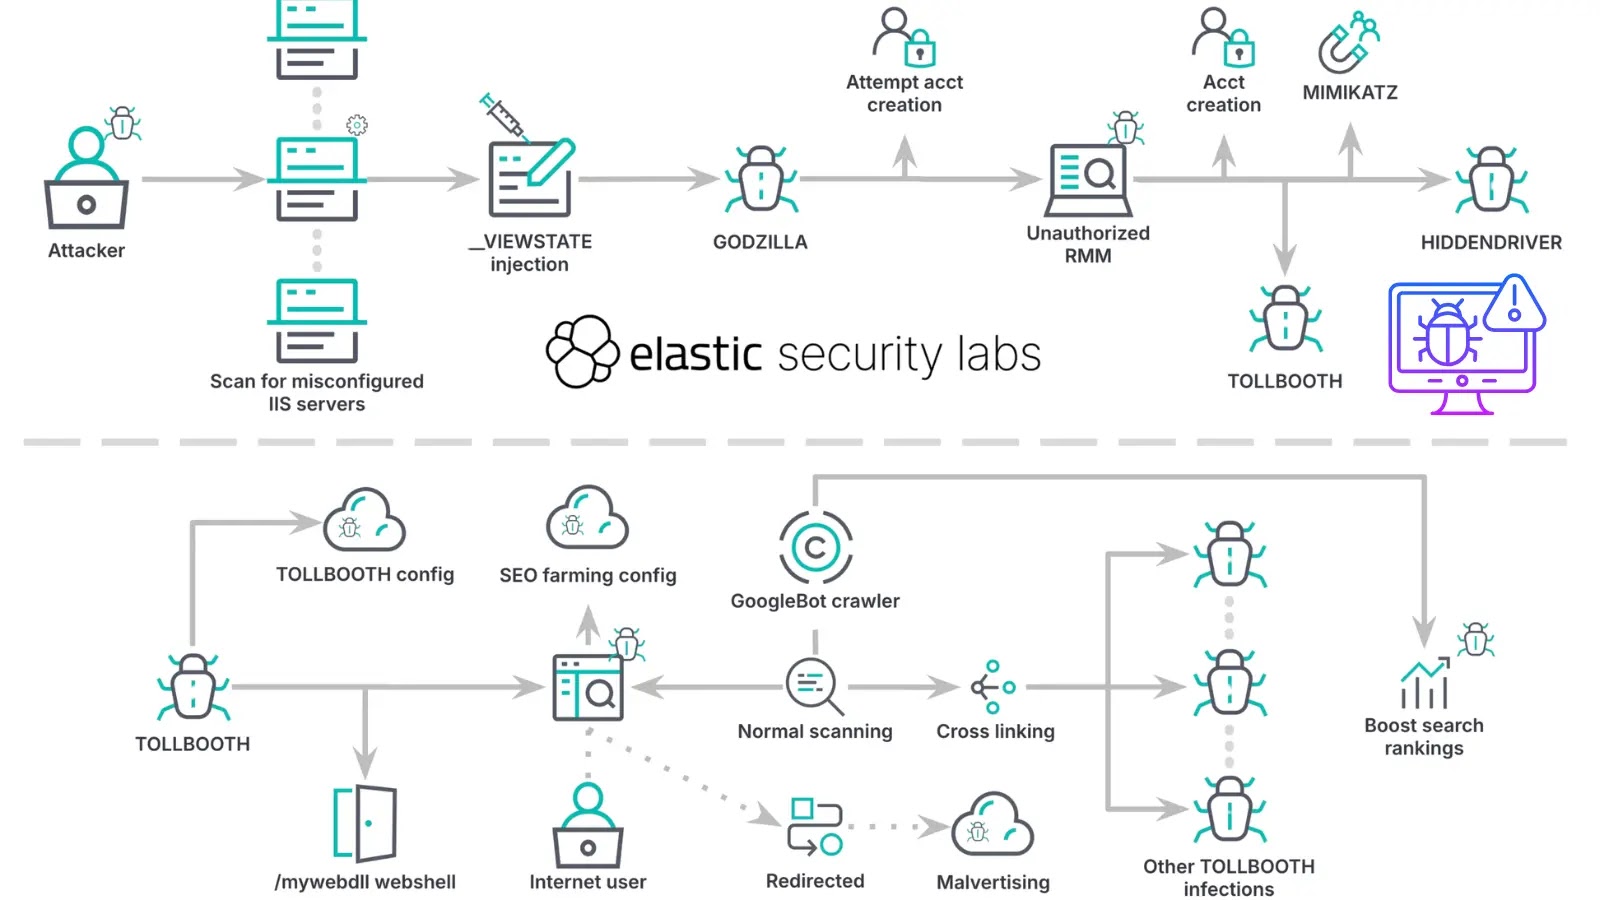
In September 2025, Texas A&M University System (TAMUS) Cybersecurity, a managed detection and response provider, in collaboration with Elastic Security Labs, uncovered a sophisticated post-exploitation…
Threat actors are increasingly targeting Azure Blob Storage, Microsoft’s flagship object storage solution, to infiltrate organizational repositories and disrupt critical workloads. With its capacity to…
Cybercriminals continue to evolve their email phishing arsenals, reviving legacy tactics while layering on advanced evasions to slip past automated filters and human scrutiny. In…
CyberProof researchers detected a significant surge in Remcos (Remote Control & Surveillance Software) campaigns throughout September and October 2025, exploiting sophisticated fileless techniques to evade…
SharkStealer, a Golang-based information stealer, has been observed leveraging the Binance Smart Chain (BSC) Testnet as a covert dead-drop mechanism for command-and-control (C2) communications. By…
Cybercriminals are increasingly exploiting a legitimate Microsoft 365 feature designed for enterprise convenience, turning Exchange Online’s Direct Send into a dangerous vector for phishing campaigns…
In a newly uncovered campaign, the threat group known as Bitter—also tracked as APT-Q-37—has leveraged both malicious Office macros and a previously undocumented WinRAR path…
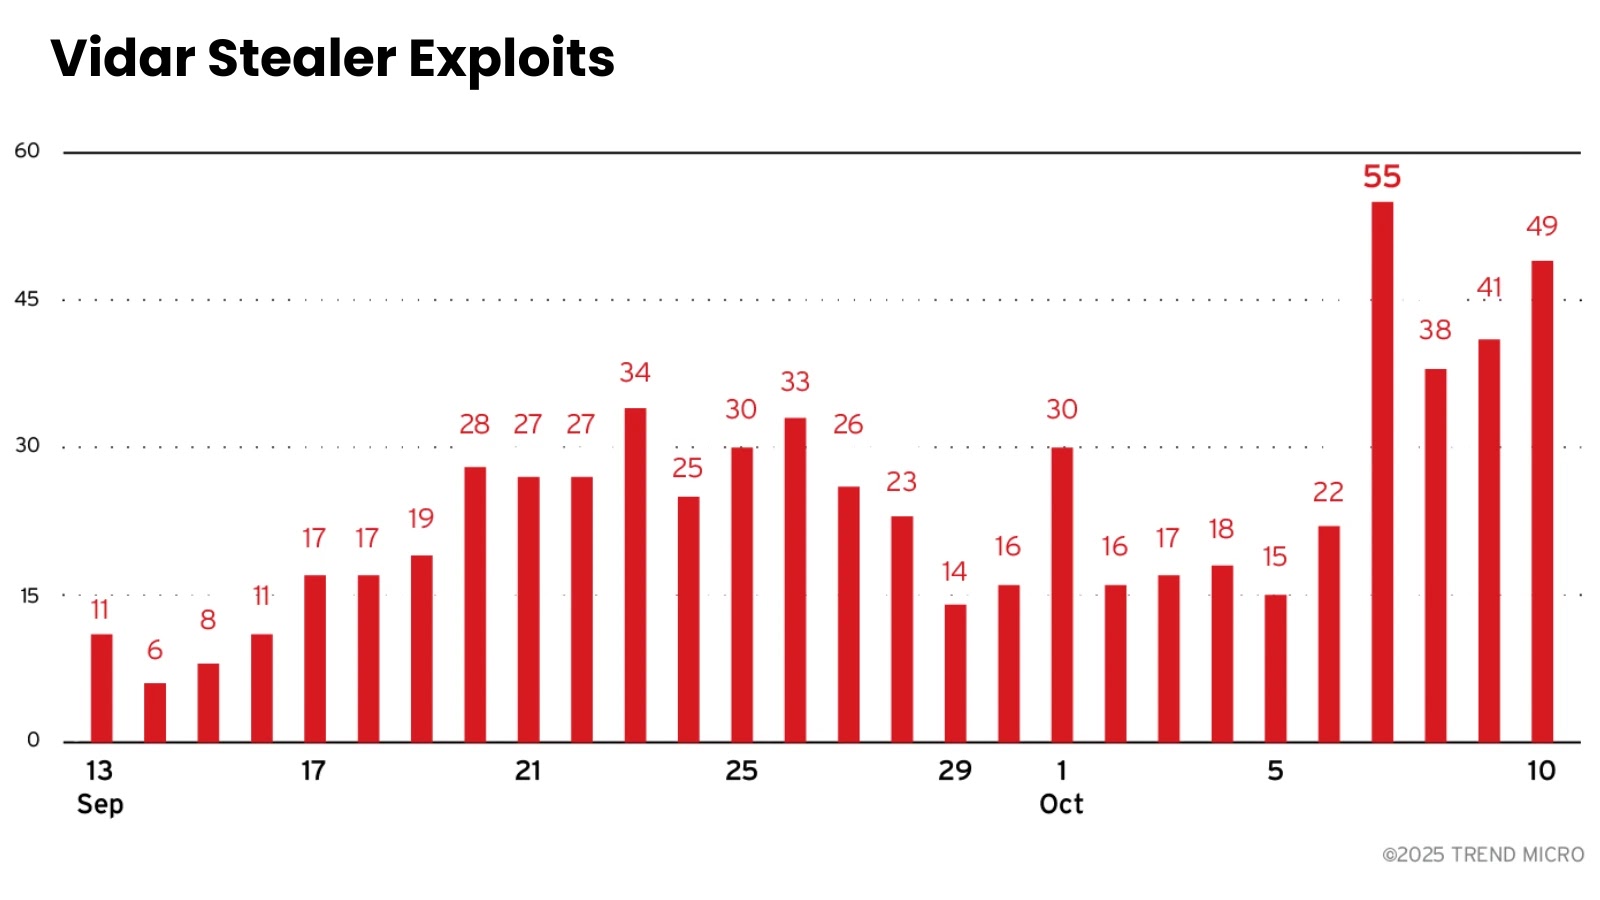
On October 6, 2025, the cybercriminal developer known as “Loadbaks” announced the release of Vidar Stealer v2.0 on underground forums, introducing a sophisticated information-stealing malware…
A sophisticated, Rust-based malware dubbed ChaosBot has been exposed utilizing the Discord platform for its Command and Control (C2) operations. This isn’t your average botnet;…
The cybercrime ecosystem surrounding stealer malware has reached unprecedented scale, with threat actors now processing millions of stolen credentials daily through sophisticated distribution networks. Security…
Salt Typhoon represents one of the most persistent and sophisticated cyber threats targeting global critical infrastructure today. Believed to be linked to state-sponsored actors from…