Microsoft Tapped China Engineers for SharePoint Support
A new investigation has revealed that Microsoft relied on China-based engineers to provide technical support and bug fixes for SharePoint, the same collaboration software that…
A new investigation has revealed that Microsoft relied on China-based engineers to provide technical support and bug fixes for SharePoint, the same collaboration software that…
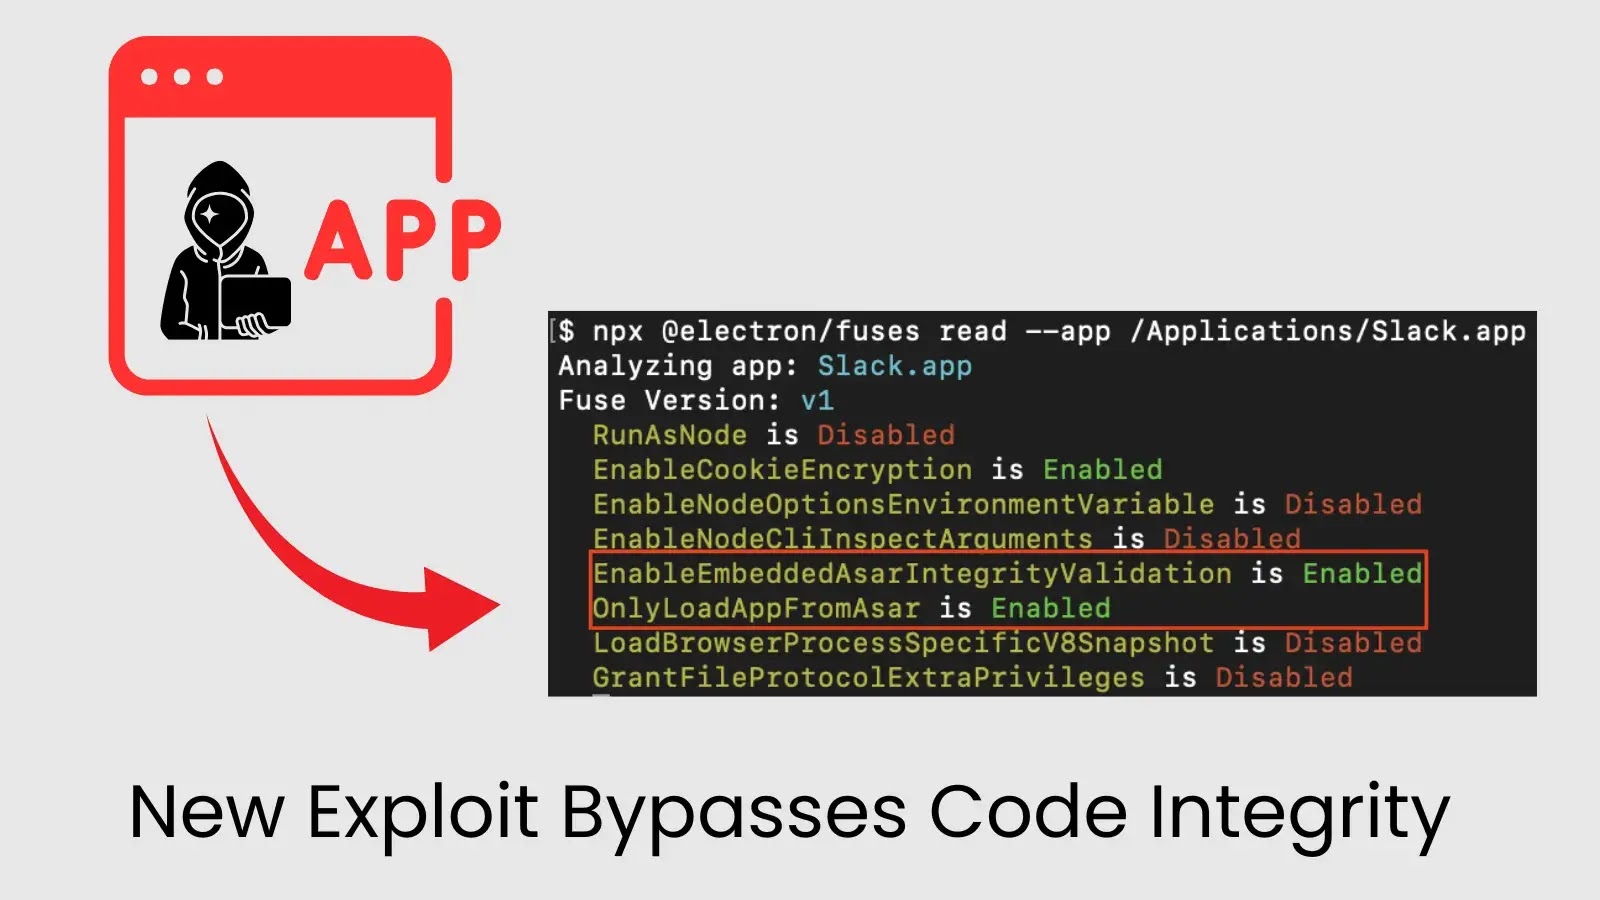
A new security exploit has been discovered that lets attackers slip malicious code into widely used desktop applications including Signal, 1Password, Slack, and Google Chrome…
A critical security flaw in SAP S/4HANA, tracked as CVE-2025-42957, is being actively exploited by attackers, according to research from SecurityBridge. The vulnerability, which carries…
A marked escalation in the abuse of ConnectWise ScreenConnect installers since March 2025, with U.S.-based businesses bearing the brunt of these incursions. Adversaries are now…
SafePay, an emerging ransomware group, has rapidly ascended from obscurity to notoriety in 2025. In June alone, the group claimed responsibility for attacks on 73…
A sophisticated threat actor, TAG-150, active since at least March 2025. Characterized by rapid malware development, technical sophistication, and a sprawling multi-tiered infrastructure, TAG-150 has…
The Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent warning regarding critical vulnerabilities in popular TP-Link router models that are currently being actively…
A sophisticated malware campaign targeting Colombian institutions through an unexpected vector: weaponized SWF and SVG files that successfully evade traditional antivirus detection. The discovery emerged…
A sophisticated cryptojacking campaign that hijacks Windows’ native Character Map utility (“charmap.exe”) to evade Windows Defender and covertly mine cryptocurrency on compromised machines. First detected…
A sophisticated North Korean cyber operation has been exposed, revealing how state-sponsored hackers systematically monitor cybersecurity intelligence platforms to detect when their malicious infrastructure is…
A novel serverless command-and-control (C2) technique that abuses Google Calendar APIs to obscure malicious traffic inside trusted cloud services. Dubbed MeetC2, this lightweight, cross-platform proof-of-concept…
A critical security vulnerability has been discovered in Microsoft Windows systems that allows attackers to escalate their privileges and potentially gain complete control over affected…