BlackHat AI Tool WormGPT Enhanced with Grok and Mixtral
The rapid evolution of large language models (LLMs) has not only transformed legitimate industries but has also found its way into the hands of cybercriminals.…
The rapid evolution of large language models (LLMs) has not only transformed legitimate industries but has also found its way into the hands of cybercriminals.…
Qilin ransomware has emerged as a formidable force, rapidly ascending to prominence amid the collapse of once-dominant groups like RansomHub and LockBit in 2025. Active…
The Qualys Threat Research Unit (TRU) has uncovered two interconnected local privilege escalation (LPE) vulnerabilities—CVE-2025-6018 and CVE-2025-6019—that together enable attackers to gain full root access…
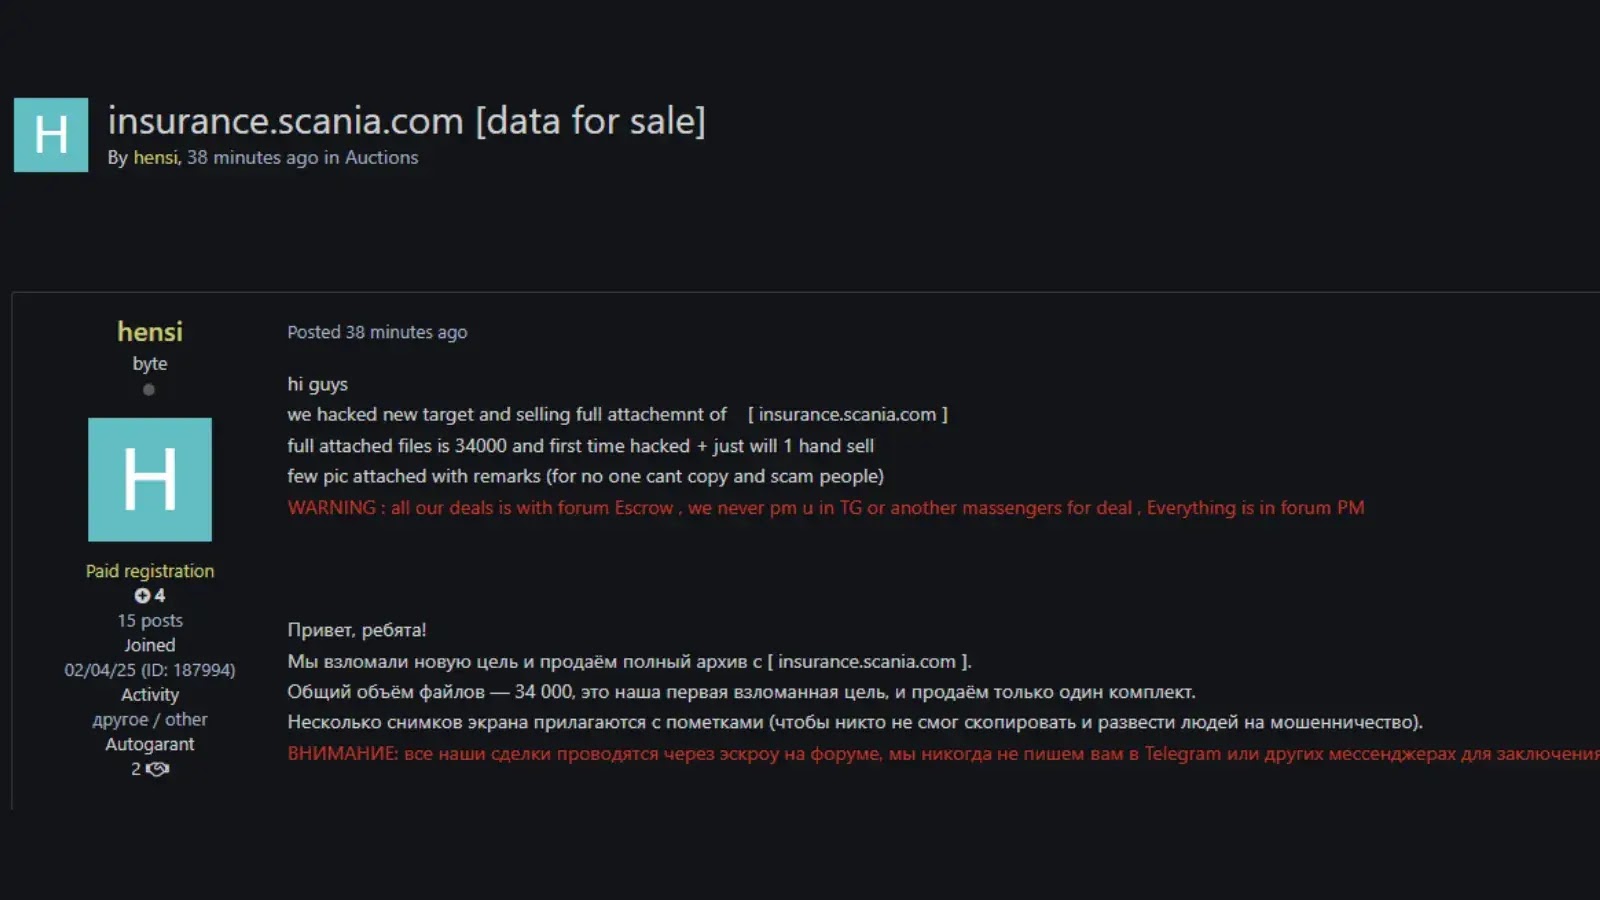
A significant data breach has rocked Sweden’s Scania Financial Services, as a threat actor operating under the alias “hensi” claims to have infiltrated the subdomain…
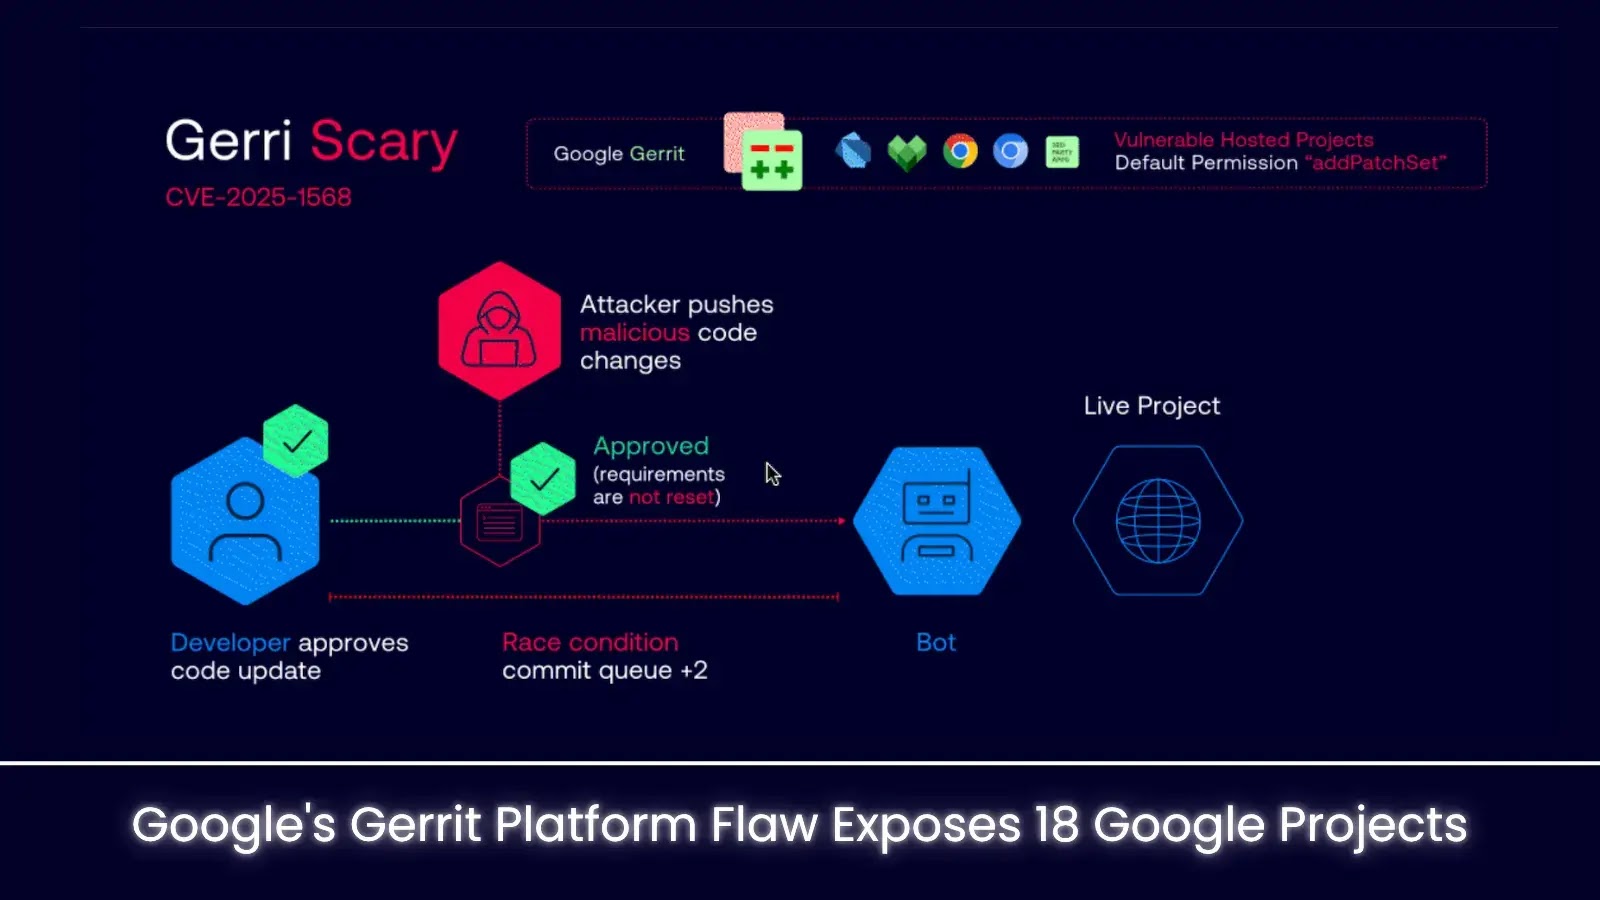
A critical vulnerability, dubbed “GerriScary,” has been discovered in Google’s Gerrit code-collaboration platform, putting at least 18 major Google projects—including ChromiumOS, Chromium, Dart, and Bazel—at…
The Cybersecurity and Infrastructure Security Agency (CISA) issued an urgent alert regarding active exploitation of a critical Linux kernel vulnerability, tracked as CVE-2023-0386, which has…
Two critical vulnerabilities have been discovered in Citrix NetScaler ADC (formerly Citrix ADC) and NetScaler Gateway (formerly Citrix Gateway), potentially exposing sensitive data to hackers…
Veeam, a leading provider of data protection and backup solutions, disclosed three critical vulnerabilities affecting its widely deployed backup software. These flaws—assigned CVE-2025-23121, CVE-2025-24286, and…
The XDSpy threat actor has been identified as exploiting a Windows LNK zero-day vulnerability, dubbed ZDI-CAN-25373, to target governmental entities in Eastern Europe and Russia.…
A recently uncovered malware campaign has revealed a highly sophisticated, multi-stage infection process utilizing heavily obfuscated Visual Basic Script (VBS) files to deploy remote access…
An important development discovered in March 2025 by Orange Cyberdefense’s Managed Threat Detection teams in Belgium was that a European client was the subject of…
The two new variants of the KimJongRAT stealer have emerged, showcasing the persistent and evolving nature of this malicious tool first identified in 2013. Detailed…