DragonForce Ransomware Reportedly Compromised Over 120 Victims in the Past Year
DragonForce, a ransomware group first identified in fall 2023, has claimed over 120 victims in the past year, marking its rapid ascent as a formidable…
DragonForce, a ransomware group first identified in fall 2023, has claimed over 120 victims in the past year, marking its rapid ascent as a formidable…
A newly identified wave of cyberattacks by the notorious Scattered Spider hacking group has zeroed in on help-desk administrators at major technology companies, leveraging advanced…
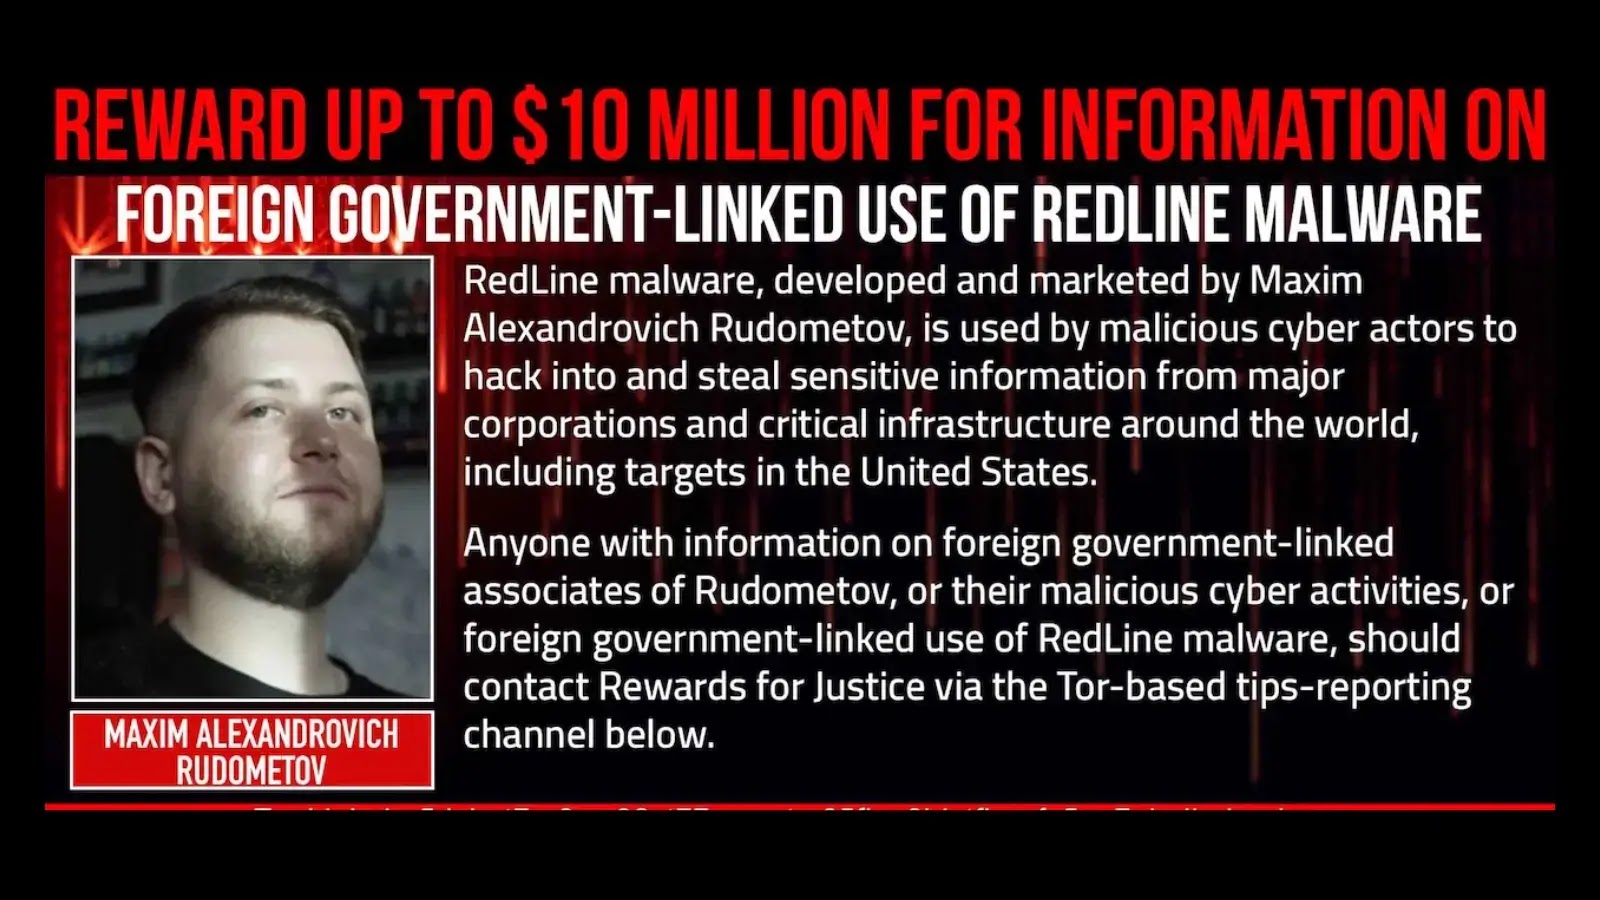
The US State Department has announced a reward of up to $10 million for information leading to the identification or location of Maxim Alexandrovich Rudometov,…
HUMAN’s Satori Threat Intelligence and Research team, in collaboration with Google, Trend Micro, and Shadowserver, has uncovered and partially disrupted a massive cyber fraud operation…
In May 2025, AWS disclosed a critical remote code execution (RCE) vulnerability, CVE-2025-4318, in the @aws-amplify/codegen-ui package—a core dependency for AWS Amplify Studio’s UI code…
Government agencies worldwide are facing an unprecedented wave of cyberattacks, with adversaries employing advanced tactics to breach critical infrastructure and steal sensitive data. Recent case…
Hewlett-Packard Enterprise (HPE) has released a critical security bulletin addressing multiple high-impact vulnerabilities in its Insight Remote Support (IRS) software, versions prior to 7.15.0.646. These…
A critical memory corruption vulnerability, tracked as CVE-2025-5688, has been disclosed in FreeRTOS-Plus-TCP, Amazon’s open-source TCP/IP stack widely used in embedded and IoT devices. The…
A critical security flaw has been uncovered in numerous popular Chrome extensions, affecting millions of users worldwide by exposing sensitive credentials such as API keys,…
Cisco Talos has uncovered a sophisticated and destructive cyberattack targeting a critical infrastructure entity in Ukraine, deploying a previously unknown wiper malware dubbed “PathWiper.” This…
The widespread text-sharing website Paste.ee has been used as a weapon by bad actors to spread powerful malware strains like XWorm and AsyncRAT, which is…
A critical memory leak vulnerability in Apache Tomcat’s HTTP/2 implementation (CVE-2025-31650) has been weaponized, enabling unauthenticated denial-of-service attacks through malformed priority headers. The flaw affects…