Chinese Hackers Breached Deep Into US Telecom to Spy on Calls and Texts
In a breach that lawmakers are calling the most serious in U.S. history, Chinese hackers infiltrated the nation’s telecommunications systems, gaining the ability to listen…
In a breach that lawmakers are calling the most serious in U.S. history, Chinese hackers infiltrated the nation’s telecommunications systems, gaining the ability to listen…
A design flaw in the logging mechanism of Fortinet’s VPN servers has been uncovered, allowing attackers to conduct brute-force attacks without detection. This vulnerability, disclosed…
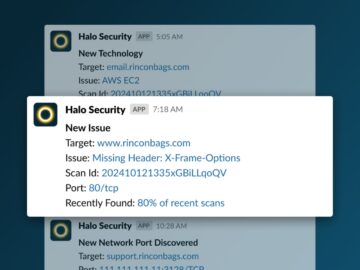
Halo Security, a leader in external attack surface management and penetration testing, has announced the launch of its new Slack® app, empowering cybersecurity teams to…
FrostyGoop, a newly discovered OT-centric malware that exploited Modbus TCP to disrupt critical infrastructure in Ukraine, capable of both internal and external attacks, targets industrial…
Federal authorities have unsealed charges against five individuals accused of orchestrating sophisticated phishing schemes that targeted employees of companies across the United States. The alleged…
Helldown, a new ransomware group, actively exploits vulnerabilities to breach networks, as since August 2024, they have compromised 28 victims, leaking their data on a…
A race condition vulnerability in Apple’s WorkflowKit has been identified, allowing malicious applications to intercept and manipulate shortcuts on macOS systems. This vulnerability, cataloged as…
The Wireshark Foundation has officially announced the release of Wireshark 4.4.2, the latest version of the world’s most popular network protocol analyzer. Wireshark is wide…
SquareX, the leading browser security company, will make its Australian debut at Melbourne CyberCon 2024, hosted by AISA (Australian Information Security Association), from 26th to…
North Korean IT workers, operating under the cluster CL-STA-0237, have been implicated in recent phishing attacks leveraging malware-infected video conference apps. The group, likely based…
Water Barghest, a sophisticated botnet, exploits vulnerabilities in IoT devices to enlist them in a residential proxy marketplace by leveraging automated scripts to identify vulnerable…
APT31, using the Rekoobe backdoor, has been observed targeting TradingView, a popular financial platform, as researchers discovered malicious domains mimicking TradingView, suggesting a potential interest…