Node.js Malware Takes Over Victim’s Computer
Through strategies like polymorphic code, which continuously alters its appearance to prevent detection, as well as employing encryption and obfuscation to disguise its actions, malware…
Through strategies like polymorphic code, which continuously alters its appearance to prevent detection, as well as employing encryption and obfuscation to disguise its actions, malware…
Apple previously reported three zero-day vulnerabilities exploited in the wild by threat actors, which Apple fixed as part of an Emergency patch update. However, a…
Healthcare has been one of the primary industries targeted by threat actors as part of every malware or ransomware campaign. Many Advanced Persistent Threat (APT)…
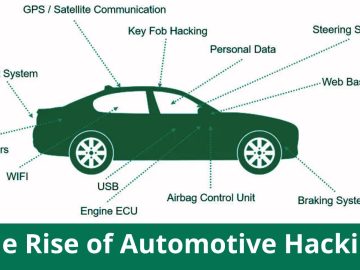
Though we can’t see it, the world brims with more technology than ever. These days, devices with internet connectivity live within the ever-growing Internet of…
Cybersecurity analysts at NSFOCUS Security Labs recently uncovered an unknown phishing-based attack process during threat-hunting. Apart from this, during their further investigation, they identified two…
Google Chrome has been recently discovered to be a Use-after-free vulnerability that threat actors can exploit to attack users. This vulnerability exists in the Google…
The Progress MOVEit software’s vulnerability resulted in a cybersecurity breach that affected BORN (the Better Outcomes Registry & Network), which gathers data on pregnancies, births, the…
The threat actors have been spotted increasingly depending on Remote Management and Monitoring (RMM) tools, which resulted in a relatively botched Hive ransomware distribution. The original payload…
This article explores the conversion of Microsoft Outlook’s OST file to PST format and highlights the necessity of this conversion for tasks. Learn the manual…
EvilBamboo, formerly known as “Evil Eye,” has been found to target Tibetan, Uyghur, and Taiwanese organizations and individuals. This threat actor was mentioned as conducting…
In a recent disclosure, BIND 9, a widely-used DNS (Domain Name System) server software, has been found vulnerable to two critical security flaws, labeled CVE-2023-4236…
OilRig (APT34) is an Iranian cyberespionage group active since 2014, targeting Middle Eastern governments and various industries like:- Chemical Energy Finance Telecom OilRig launched DNSpionage…