Researchers Uncover Series of Ransomware Attacks
Ransomware groups often recycle tools, techniques, and procedures. Even some of them also provide playbooks for affiliates as well. Numerous use Cobalt Strike for remote…
Ransomware groups often recycle tools, techniques, and procedures. Even some of them also provide playbooks for affiliates as well. Numerous use Cobalt Strike for remote…
The well-known bulletproof hosting platform, Lolek Hosted, has been shut down by law enforcement officials from the United States and Poland to limit fraudsters’ access…
Infostealer malware is becoming extremely popular among cybercriminals, especially in the malware-as-a-service (MaaS) based sector. These kinds of malware remain undetected as much as possible…
In the last three years, hackers unknowingly seeking data or malware deployment have found a seemingly vulnerable virtual machine that is hosted in the U.S.,…
The TargetCompany ransomware (aka Mallox, Fargo, and Tohnichi) is actively targeting the organizations that are using or running vulnerable SQL servers. Apart from this, recently,…
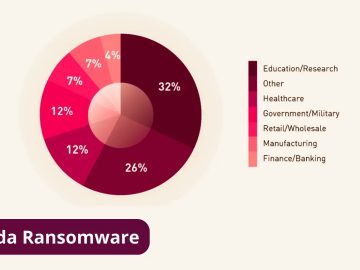
A new ransomware group known as ‘Rhysida’ has been operating since May 2023, posing a huge danger to the healthcare industry. Rhysida ransomware gang has been…
CODESYS, a widely-used integrated environment for controller programming, holds a strong presence in Operational Technology across diverse industries, such as:- Factory automation Energy Mobile Building…
RedHotel (TAG-22), a Chinese-state-sponsored threat group, is well-known for its persistence, prominence, operational intensity, and global reach. RedHotel is reported to have acted upon over…
Researchers have discovered a Google Bard Ads campaign that is being used by cybercriminals on Facebook to impersonate well-known generative AI brands such as ChatGPT…
Gather Data Sampling (GDS) impacts select Intel CPUs, enabling attackers to deduce outdated data through malicious use of gather instructions. While all these entries link…
Microsoft fixed 74 security issues in its August Patch Tuesday release, including two that were being actively exploited and twenty-three that allowed remote code execution.…
An unidentified threat actor has deployed the Yashma ransomware variant since June 4, 2023, actively targeting English-speaking countries like:- While this new variant of Yashma…