Downfall Attack Enables Extraction of Passwords and Encryption
Gather Data Sampling (GDS) impacts select Intel CPUs, enabling attackers to deduce outdated data through malicious use of gather instructions. While all these entries link…
Gather Data Sampling (GDS) impacts select Intel CPUs, enabling attackers to deduce outdated data through malicious use of gather instructions. While all these entries link…
Microsoft fixed 74 security issues in its August Patch Tuesday release, including two that were being actively exploited and twenty-three that allowed remote code execution.…
An unidentified threat actor has deployed the Yashma ransomware variant since June 4, 2023, actively targeting English-speaking countries like:- While this new variant of Yashma…
It has been reported that over 43 Android applications, which are available on the Google Play Store, display ads while the mobile screen is turned…
Recent reports indicate that threat actors have been manipulating Script kiddies or amateur hackers into performing malicious actions that they never intended. This is done…
Microsoft Bug Bounty Program awarded $13.8M for their collaboration with over 345 security researchers from +45 countries around the world between July 01, 2023, to…
A Critical vulnerability was discovered in the widely used PaperCut MG/ NF print management software running on Windows prior to version 22.1.3. As of the…
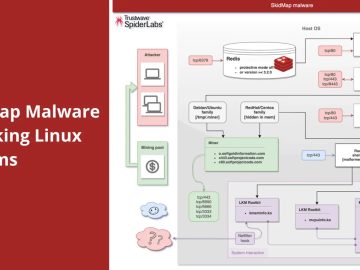
According to recent reports, there have been instances of threat actors using malware called “SkidMap” to exploit vulnerable Redis systems. Earlier versions of SkidMap were…
After being criticized as “grossly irresponsible” and “blatantly negligent” by the CEO of Tenable, Microsoft addressed a vulnerability in the Power Platform Custom Connectors feature…
IBM has discovered a vulnerability in the IBM SDK, Java Technology Edition, that allows threat actors to execute arbitrary code on the system due to…
Tesla has a reputation for having highly integrated and technologically advanced car computers, which can be used for everything from basic entertainment to completely autonomous…
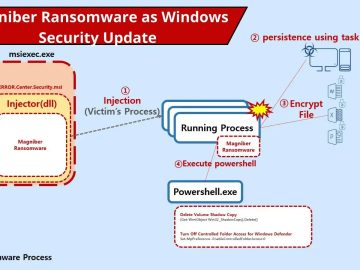
Magniber Ransomware was first detected in late 2017; it targeted South Korean users through malvertising attacks using the Magnitude Exploit Kit. It had been distributed earlier…