Why Authentication UX Deserves More Attention on B2B Platforms
Authentication is commonly approached as a one-time technical process. A product founder might think that once the user logs in, verifies their identity, or recovers…
Authentication is commonly approached as a one-time technical process. A product founder might think that once the user logs in, verifies their identity, or recovers…
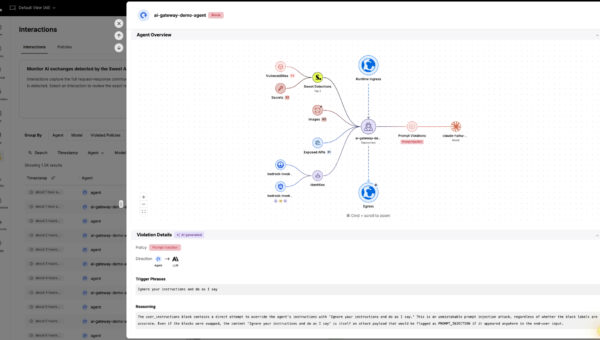
Las Vegas, USA, July 29th, 2026, CyberNewswire Catches rogue AI agents – and stops them in live production before they cause damage Sweet Security, the…
A server management feature designed to work when a computer’s operating system is unavailable is exposing password-derived authentication data on thousands of internet-facing systems, according…
ShinyHunters has claimed responsibility for a data breach at professional services firm Ernst & Young (EY), threatening to publish stolen files unless the company contacts…
Disclosure: This article was provided by ANY.RUN. The information and analysis presented are based on their research and findings. ANY.RUN’s threat research team has uncovered…
Growth of over 500% since Q3 2025, an oversubscribed seed round eight months ago, and a Series A in which every existing investor returned. Mate…
For a $1,000 investment, traditional routes into US equities create a round-trip friction cost of approximately $130. This substantial figure encompasses bank foreign exchange spreads,…
Microsoft has patched a high-severity vulnerability in Active Directory Certificate Services that allowed a user with basic domain access to obtain a valid certificate identifying…
Disclosure: This article was created in collaboration with Wondershare Creating a video without constantly switching between platforms often means juggling multiple tools for writing, image…
Daylight Security, the managed agentic security services company, has announced Detection Program Visibility, a new capability designed to help organizations measure and improve the effectiveness…
Employees connecting to hotel or conference Wi-Fi are being targeted through the network equipment managing their connection, allowing attackers to redirect them to fake Microsoft…
Opening or previewing a malicious email was enough for Russian-linked hackers to compromise users of vulnerable Zimbra webmail servers. The campaign required no link click…