Chinese Scammers Exploit Cloned Websites in Vast Gambling Network
The large-scale scam campaign has been ongoing for at least two years, and the cloned websites are still operational. Online gambling is a booming industry,…
The large-scale scam campaign has been ongoing for at least two years, and the cloned websites are still operational. Online gambling is a booming industry,…
While domain squatting opens the door to brand hijacking, it also exposes unsuspecting users and businesses to critical cybersecurity threats including phishing and malware attacks.…
Database security is difficult because of the large volume of attacks, zero-day exploits, human errors, and the need for continual management of security tools. On…
An X (Twitter) account, operated by hackers using the handle @MonkeyInject, alleges that the breach was facilitated by a former employee of Plume. The smart…
As of 2023, there are over 1.7 million websites using Drupal, underscoring the significance of acquiring Drupal tips and tricks. The migration process can be…
The IPStorm botnet targeted Windows, Linux, Mac, and Android devices and claimed victims in Asia, Europe, North America, and South America. A Russian-Moldovan national has…
The recently discovered IronWind malware is distributed via email attachments, cleverly disguised as official correspondence related to the “Economic Cooperation Program with the Countries of…
Omegle’s founder Brooks Leif K-Brooks, cited the rampant misuse of the platform by pedophiles and other criminals as a major factor in the decision to…
As of now, based on the information regarding the sale of the Abrax666 AI Chatbot, cybersecurity researchers are of the opinion that the chatbot is…
BulletProftLink, a prolific phishing-as-a-service (PhaaS) and initial access broker (IAB) operation was operating since 2015. In a significant blow to the cybercrime community, Malaysian police…
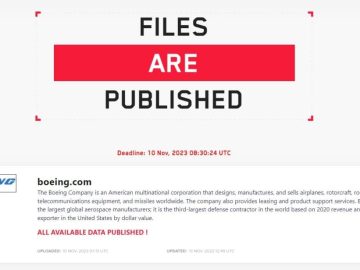
The notorious Lockbit ransomware group has leaked a trove of data belonging to the leading global aerospace company Boeing, apparently following failed ransom negotiations. The…
The OracleIV botnet malware employs various tactics, with a primary focus on executing DDoS attacks through UDP and SSL-based floods. Cybersecurity researchers at Cado Security…