Qrator Labs Mitigated Record L7 DDoS Attack from 5.76M-Device Botnet
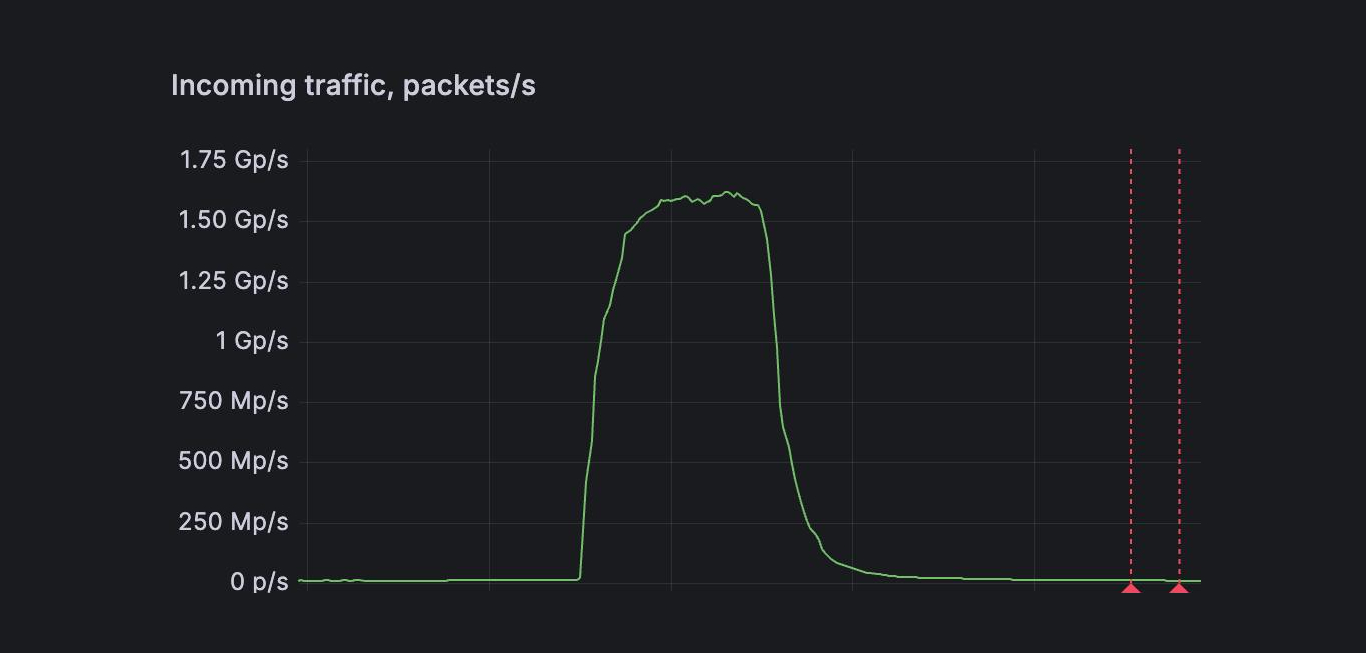
In early September, Qrator Labs detected and mitigated one of the most significant L7 DDoS attacks seen this year, carried out by what is now…
In early September, Qrator Labs detected and mitigated one of the most significant L7 DDoS attacks seen this year, carried out by what is now…
Okta Threat Intelligence exposes VoidProxy, a new PhaaS platform. Learn how this advanced service uses the Adversary-in-the-Middle technique to bypass MFA and how to protect…
New SEO poisoning campaign exposed! FortiGuard Labs reveals how attackers trick users with fake websites to deliver Hiddengh0st and Winos malware. A new cyberattack campaign…
Scattered Lapsus$ Hunters, linked to the Jaguar Land Rover cyberattack, claims to shut down as experts suggest the group is fracturing under pressure. For days,…
A new report from Cofense reveals that cybercriminals are blending phishing and malware, including Muck Stealer, Info Stealer, ConnectWise RAT, and SimpleHelp RAT in dual-threat…
US Senator Ron Wyden urges the FTC to investigate Microsoft after its software contributed to a major ransomware attack on Ascension Hospital, exposing 5.6 million…
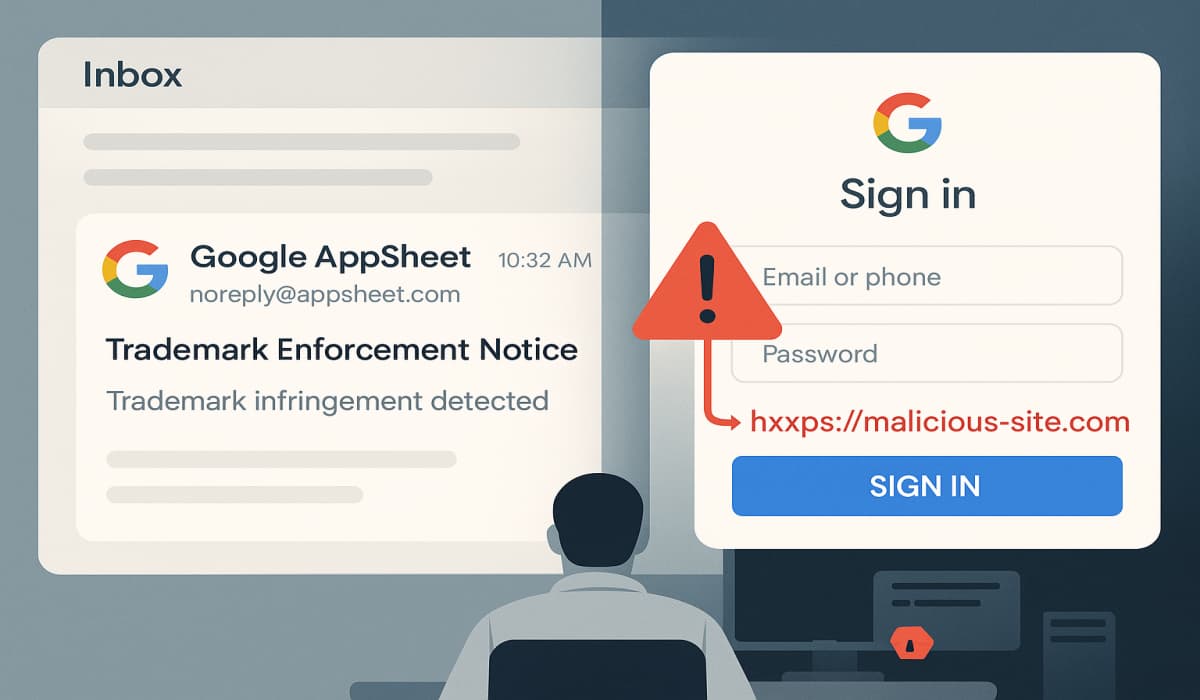
A phishing scam is exploiting Google’s trusted AppSheet platform to bypass email filters. Learn how hackers are using legitimate tools to trick Google Workspace users.…
LNER cyber attack exposes passenger contact details and journey data. No financial information or passwords were taken, but customers are urged to be cautious. UK-based…
A previously dormant macOS threat, ChillyHell, is reviving. Read how this malware can bypass security checks, remain hidden, and install itself permanently to control your…
London, United Kingdom, September 11th, 2025, CyberNewsWire FastNetMon today announced that it detected a record-scale distributed denial-of-service (DDoS) attack targeting the website of a leading DDoS scrubbing…
Bitdefender uncovers EggStreme, a fileless malware by a China-based APT targeting the Philippine military and APAC organisations. Cybersecurity researchers at Bitdefender have identified a new…
LevelBlue Labs has published new research on a recent attack that used a fileless loader to deliver AsyncRAT, a well-known Remote Access Trojan used for…