Top LLM vulnerabilities and how to mitigate the associated risk
As large language models (LLMs) become more prevalent, a comprehensive understanding of the LLM threat landscape remains elusive. But this uncertainty doesn’t mean progress should…
As large language models (LLMs) become more prevalent, a comprehensive understanding of the LLM threat landscape remains elusive. But this uncertainty doesn’t mean progress should…
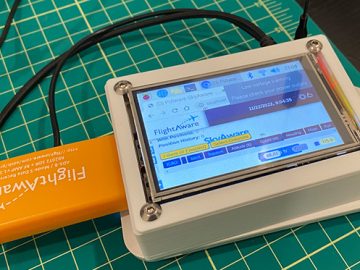
Fly Catcher is an open-source device that can detect aircraft spoofing by monitoring for malicious ADS-B signals in the 1090MHz frequency. Angelina Tsuboi, the developer…
A team of computer scientists led by the University of Massachusetts Amherst recently announced a new method for automatically generating whole proofs that can be…
For January 2024 Patch Tuesday, Microsoft has released fixes for 49 CVE-numbered vulnerabilities, two of which are critical: CVE-2024-20674 and CVE-2024-20700. None of the vulnerabilities…
Researchers have discovered over two dozen vulnerabilities in “smart” cordless nutrunners (i.e., pneumatic torque wrenches) manufactured by Bosch Rexroth that could be exploited to make…
A blind SQL injection vulnerability (CVE-2023-51448) in Cacti, a widely-used network monitoring, performance and fault management framework, could lead to information disclosure and potentially remote…
Why is it that when a company becomes aware of a potential data security incident, the team working on it (and others who are made…
In this Help Net Security interview, Phil Vachon, Head of Infrastructure in the Office of the CTO at Bloomberg, discusses the varying definitions of zero…
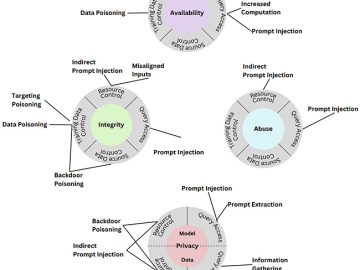
Adversaries can intentionally mislead or “poison” AI systems, causing them to malfunction, and developers have yet to find an infallible defense against this. In their…
Andrew Ginter is a widely-read author on industrial security and a trusted advisor for industrial enterprises. He holds a BSc. in Applied Mathematics and an…
In this Help Net Security interview, Jayson E. Street, Chief Adversarial Officer at Secure Yeti, discusses intriguing aspects of social engineering and unconventional methods for…
AuthLogParser is an open-source tool tailored for digital forensics and incident response, specifically crafted to analyze Linux authentication logs (auth.log). The tool examines the auth.log…