Diligent Board Reporting for IT Risk equips CISOs with third party risk scores
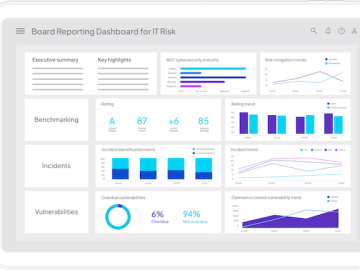
Diligent launched Board Reporting for IT Risk to provide CISOs and IT risk professionals with a holistic view of their organization’s risk posture. “As cyber…
Diligent launched Board Reporting for IT Risk to provide CISOs and IT risk professionals with a holistic view of their organization’s risk posture. “As cyber…
Tenable announced new Tenable Cloud Security features that deliver automated operating system (OS) vulnerability detection across container images, registries and pipelines. Building on existing exposure…
Code42 has added custom Insider Risk Indicators (IRIs) to its Incydr data protection solution. This addition enables security teams to customize their Insider Risk alerts…
The Biden-Harris Administration has announced a cybersecurity certification and labeling program to help Americans more easily choose smart devices that are safer and less vulnerable…
In this Help Net Security interview, Arthur Hu, SVP, Global CIO and Services & Solutions Group CTO at Lenovo, discusses how AI/ML is optimizing tech…
In January, law enforcement officials disrupted the operations of the Hive cybercriminal group, which profited off a ransomware-as-a-service (RaaS) business model. Hive is widely believed…
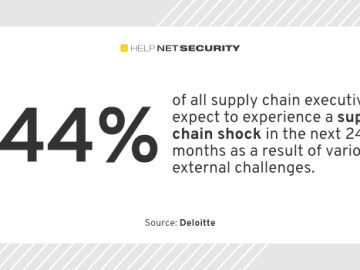
Supply chain executives significantly overestimate stakeholder trust in their supply chain capabilities and intentions, according to Deloitte. Of more than 1,000 executives from large global…
Improve your cloud security with these 9 proven strategies. Uptycs, alongside renowned expert Lee Atchison, share their list of comprehensive tactics to mitigate risks facing…
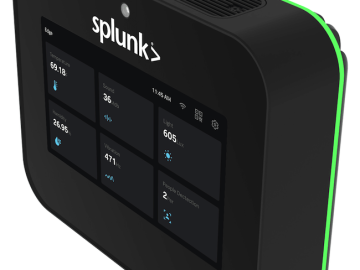
Splunk announced Splunk Edge Hub, a new solution that simplifies the ingestion and analysis of data generated by sensors, IoT devices and industrial equipment. Splunk…
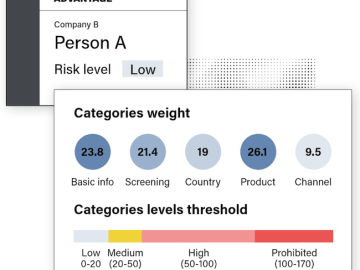
One of the biggest challenges faced by regulated and non-regulated companies is assessing whether or not another business is safe to work with. Existing approaches…
In an era where cyber threats continue to evolve, healthcare organizations are increasingly targeted by malicious actors employing multiple attack vectors, according to Trustwave. In…
Red Siege has developed and made available many open-source tools to help with your penetration testing work. The company plans to continue to support the…