vim + llm = 🔥 · rez0
If you don’t use vi/vim, you might not find this post that practical, but it also might convince you to try it! Leveraging vim’s Visual…
If you don’t use vi/vim, you might not find this post that practical, but it also might convince you to try it! Leveraging vim’s Visual…
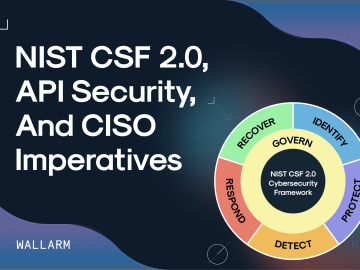
Last week, our good friend Raj Umadas, Director of Security at ActBlue, teamed up with our very own Tim Erlin, Head of Product, to talk…
We are delighted to roll out two significant updates that will redefine how you manage your program credentials and integrate your applications through webhooks. Let’s…
I should read a lot more biographies. I’m never disappointed when I do, and I always extract so much wisdom from them. I’ve been thinking…
Welcome to the 9th post in our weekly series on the new 2023 OWASP API Security Top-10 list, with a particular focus on security practitioners.…
Unsupervised Learning Unsupervised Learning is a Security, AI, and Meaning-focused company, newsletter & podcast that looks at how best to thrive as humans in a…
Greetings, digital guardians. Today, we’ll be diving into the wonderful world of External Attack Surface Management (EASM) platforms. As the sun rises on another day…
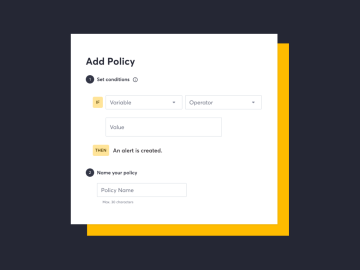
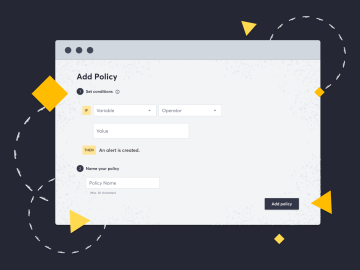
AppSec teams often struggle to either validate or scale their security policies, like enforcing security headers or removing risky technologies. This job is easier said…
We’re excited to announce that Detectify has been included in the 2023 Gartner Competitive Landscape for External Attack Surface Management report. This report is an…
AppSec teams often struggle to either validate or scale their security policies, like enforcing security headers or removing risky technologies. This job is easier said…
Resolving vulnerabilities quickly depends on several factors, not least how effectively security and product development teams collaborate. Modern security teams rely on several tools to…
The attack surface is where you can understand what you have exposed and whether you should take action on it. Previously, users couldn’t see which…