Hunting for Suspicious Windows Libraries for Execution and Defense Evasion
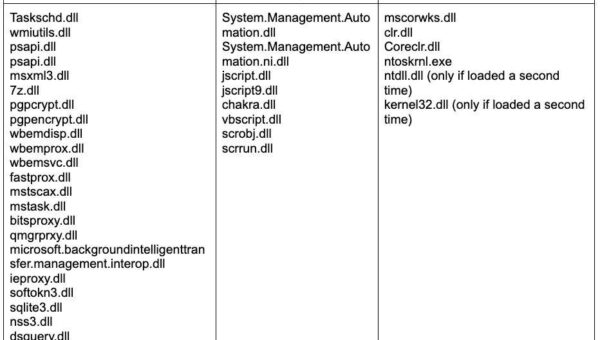
Dynamic-link library (DLL) image loads is one of the noisiest types of event in Windows, which may discourage defenders from using it for detection engineering…
Dynamic-link library (DLL) image loads is one of the noisiest types of event in Windows, which may discourage defenders from using it for detection engineering…
It is becoming more common that adversary attacks consist of more than a standalone executable or script. Advanced attacker techniques, like “living off the land”…
Preamble Credential Access consists of techniques for stealing credentials like cookies, API keys, and passwords. It is one of the top critical tactics that is…
Blog Each month, the Elastic Security Labs team dissects a different trend or correlation from the Elastic Global Threat Report. This post provides an overview…
Preamble ICEDID is a malware family discoveredin 2017 by IBM X-force researchers and is associated with the theft of login credentials, banking information, and other…
Preamble Imagine you are an Endpoint artifact developer. After you put in the work to ensure protection against conventional shellcode injections or ransomware innovations, how…
Searching for a way to help protect your network from potential domain generation algorithm (DGA) attacks? Look no further — a DGA detection package is…
Introduction Bring Your Own Vulnerable Driver (BYOVD) is an increasingly popular attacker technique wherein a threat actor brings a known-vulnerable signed driver alongside their malware,…
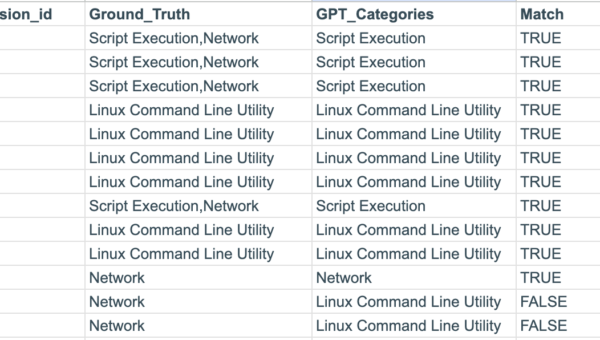
Using LLMs to summarize user sessions With the introduction of the AI Assistant into the Security Solution in 8.8, the Security Machine Learning team at…
Using LLMs and ESRE to find similar user sessions In our previous article, we explored using the GPT-4 Large Language Model (LLM) to condense complex…
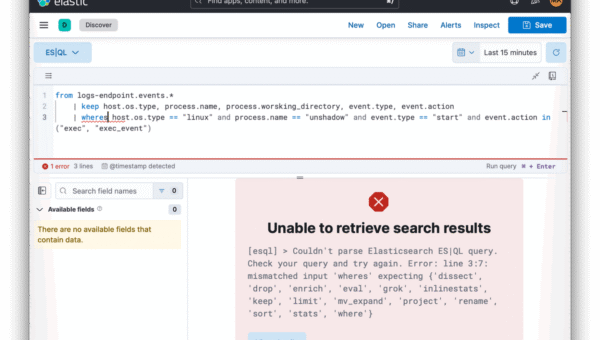
One of the amazing, recently premiered 8.11.0 features, is the Elasticsearch Query Language (ES|QL). As highlighted in an earlier post by Costin Leau, it’s a…