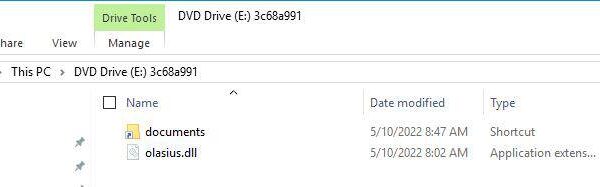
ICEDIDs network infrastructure is alive and well
Key takeaways li]:list-disc”> Initial access Command and control Persistence Core functionality Network infrastructure As mentioned in the Preamble, ICEDID has been around for many years…
Key takeaways li]:list-disc”> Initial access Command and control Persistence Core functionality Network infrastructure As mentioned in the Preamble, ICEDID has been around for many years…
To defend your environment from the SIGRed vulnerability, we recommend implementing the detection logic included below into your environment using technology such as Endpoint security,…
li]:list-disc”> A series of payloads have been shared by the GreyNoise team, including payloads containing both encoded and decoded variants for analysts looking to explore…
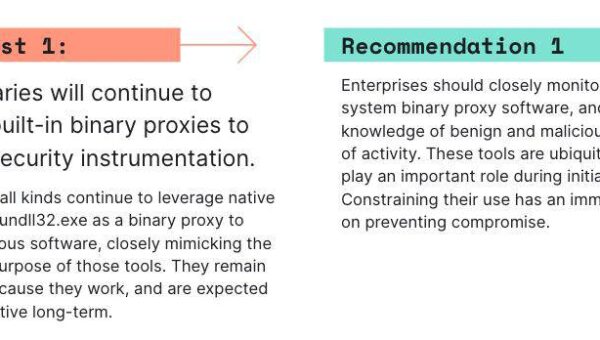
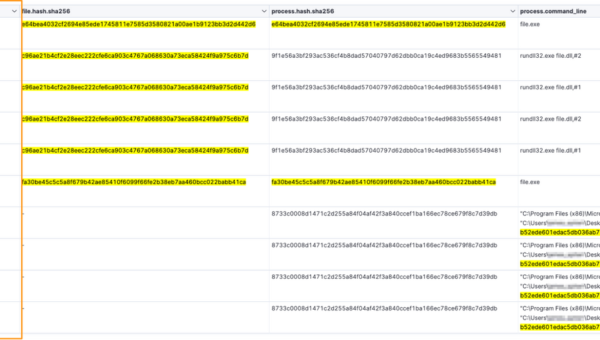
Attackers are increasingly turning to trusted software your business already depends on instead of custom malware or exploits. In one recent Huntress Security Operations Center…
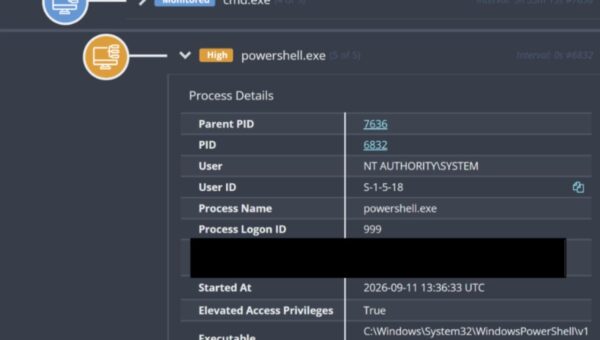
Background Huntress researchers recently came across a unique incident where, after gaining initial access via exploiting a known Samsung MagicINFO vulnerability and installing a rogue…
Picture your Microsoft 365 environment being hardened around the clock, controls rolling out on a set schedule based on expert best practices, without you having…
On March 29, 2022 a vulnerability in the Spring framework was disclosed to the public by VMware. This vulnerability had several prerequisites affecting impact:
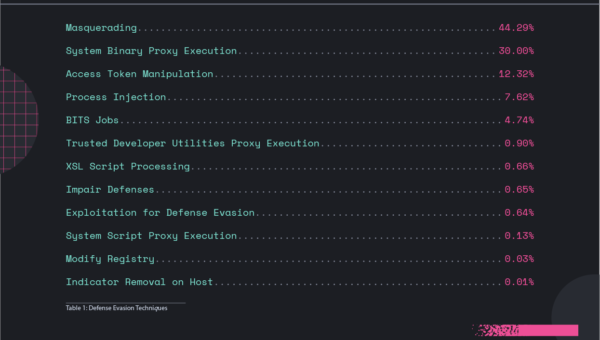
Reports Elastic Security Labs has compiled the 2022 Global Threat Report to share trends and tactics adversaries and attack groups use, as observed by our…
To understand how Elastic is currently assessing internal risk of this vulnerability in our products please see the advisoryhere. This document was updated on December…
Today, we released our first-ever Global Threat Report at Elastic. Now, customers, partners, and the security community at large will be able to identify many…
Key Takeaways li]:list-disc”> 0-day exploit – vulnerability previously unknown to defenders and does not have a public patch Activity Group – individuals, groups, or organizations…
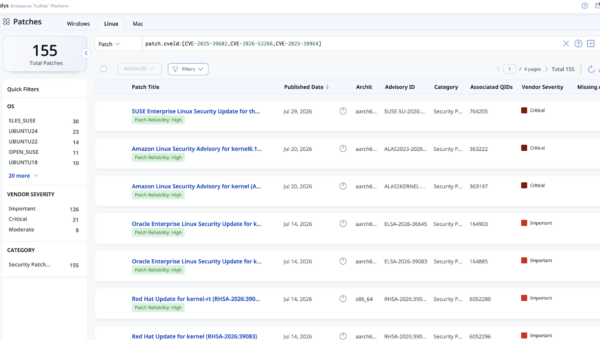
Executive Summary CISA added three actively exploited Linux kernel vulnerabilities: CVE-2025-39682, CVE-2026-53266, and CVE-2025-39964 to its KEV Catalog on September 18, 2026, triggering a 3-day…