Before the Breach: Why Test Environments Are a Major Cloud Risk
Key Takeaways Most security failures do not begin where they are discovered. By the time risk becomes visible in production, the decisions that created it…
Key Takeaways Most security failures do not begin where they are discovered. By the time risk becomes visible in production, the decisions that created it…
We all have thoughts that keep us up at night. Will the ticking noise the car made end up being an expensive repair? When will…
Huntress has been hunting malicious actors across 60,000+ user accounts for almost 2,000 small businesses enrolled in our Managed Detection and Response (MDR) for Microsoft…
Today marks one year since Huntress announced the acquisition of Curricula, which is now Huntress Security Awareness Training. This acquisition was especially exciting for all…
Most of the time when you hear about business email compromise (BEC), you hear a single user account was compromised, leading to large amounts of…
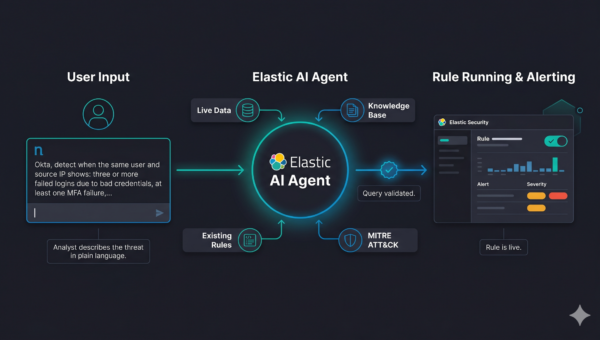
Elastic Security now includes AI-powered detection rule creation, built into the rule creation workflow. Analysts describe a threat behavior in plain English and receive a…
Elastic Security v9.4 introduces Entity Analytics Watchlists, a new capability in the Entity Analytics suite that lets security teams create named, weighted lists of users,…
Threat hunting has always been a human art; a practitioner staring at logs, forming a hypothesis, and patiently chasing it down. What if the hardest…
There’s an uncomfortable truth in security analytics that nobody talks about at conferences: The quality of your detections, alerts, and investigations is only as good…
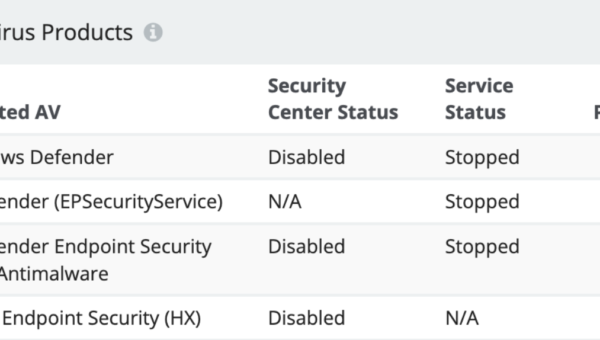
Choosing the right antivirus (AV) tool can be a real headache. With so many options available, how do you know which one is the right…
The idea of “persistence” in a cloud environment is not a well-studied topic. At most, you hear instances of the attacker creating backup logins to…
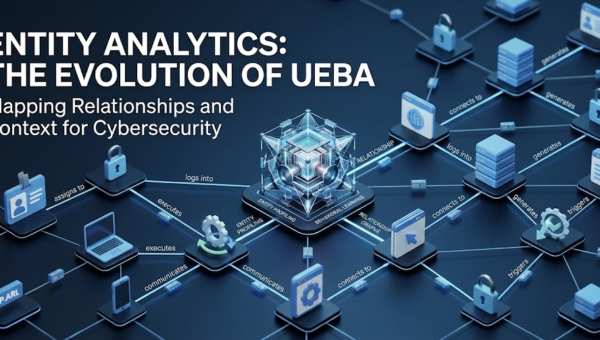
Entity Analytics is a core security analytics capability that extends Elastic Security from event-centric to entity-centric investigation. By focusing on critical entities, such as users,…