Not sleeping anymore: SOMNIRECORD’s wake-up call
Introduction While monitoring the REF2924 activity group, Elastic Security Labs researchers identified a new malware family written in C++ that we refer to as SOMNIRECORD.…
Introduction While monitoring the REF2924 activity group, Elastic Security Labs researchers identified a new malware family written in C++ that we refer to as SOMNIRECORD.…
Preamble In recent months, there has been a noticeable shift in the nature of the incidents being tracked under REF2924. Initially, the attacker employed custom,…
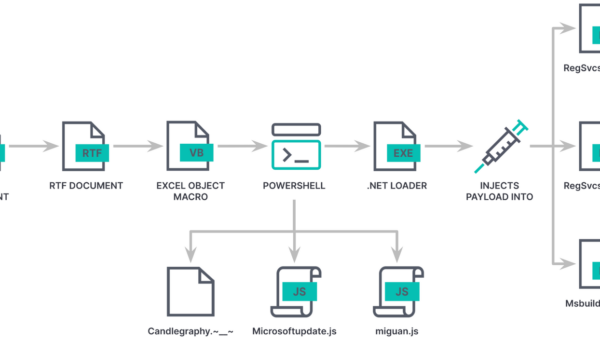
Key Takeaways li]:list-disc”> C:WindowsMicrosoft.NETFrameworkv4.0.30319RegSvcs.exe C:WindowsMicrosoft.NETFrameworkv2.0.50727RegSvcs.exe C:WindowsMicrosoft.NETFrameworkv3.5Msbuild.exe These binaries are signed and trusted by the system and can evade detection by security software that relies on…
Last November, Elastic published our inaugural global threat report: a summary of threat trends, forecasts, and recommendations based on analyzing millions of telemetry events shared…
Key takeaways li]:list-disc”> akamaicontainer[.]com akamaitechcloudservices[.]com azuredeploystore[.]com azureonlinecloud[.]com azureonlinestorage[.]com dunamistrd[.]com glcloudservice[.]com journalide[.]org msedgepackageinfo[.]com msstorageazure[.]com msstorageboxes[.]com officeaddons[.]com officestoragebox[.]com pbxcloudeservices[.]com pbxphonenetwork[.]com pbxsources[.]com qwepoi123098[.]com sbmsa[.]wiki sourceslabs[.]com visualstudiofactory[.]com zacharryblogs[.]com Potentially…
Reports Check out the newest report from Elastic Security Labs, which explores how you can protect your organization from LLM threats. Today Elastic Security Labs…
Intro Elastic Security for endpoint, with its roots in Endgame, has long led the industry for in-memory threat detection. We pioneered and patented many detection…
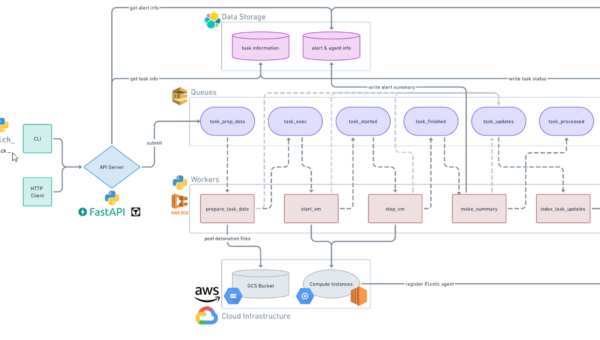
Preamble In our first post in our Detonate series, we introduced the Detonate system and what we use it for at Elastic. We also discussed…
Key takeaways li]:list-disc”> How Elastic Security Labs identified reconnaissance from the adversary group The adversary’s steps to evade detection using xcc , installing the sh.py…
Run security operations for more than one team, region, or customer, and you inherit a familiar tradeoff. One giant deployment gives you a single view…
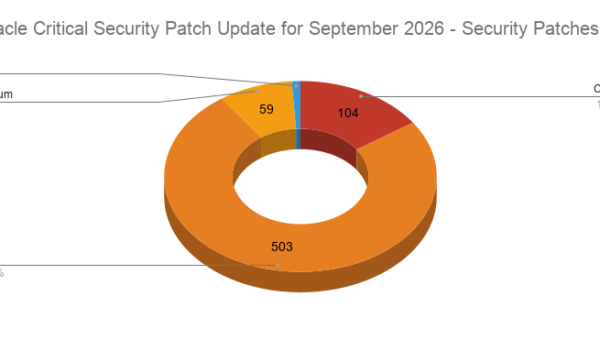
Oracle addresses 672 CVEs in its September 2026 Critical Security Patch Update with 673 patches, including 104 critical updates. Key Takeaways The September 2026 Critical…
Key Takeaways Periodic audits provide a point-in-time assessment, but they cannot demonstrate whether controls remain effective between audit cycles. Qualys platform data shows 10.5 billion…