Meanwhile, the agency is finalizing an incident-reporting regulation and setting up a new industry coordination structure.
Meanwhile, the agency is finalizing an incident-reporting regulation and setting up a new industry coordination structure.
The vulnerability has a maximum severity score of 10, indicating serious potential impact and relative ease to exploit by an attacker. Source link
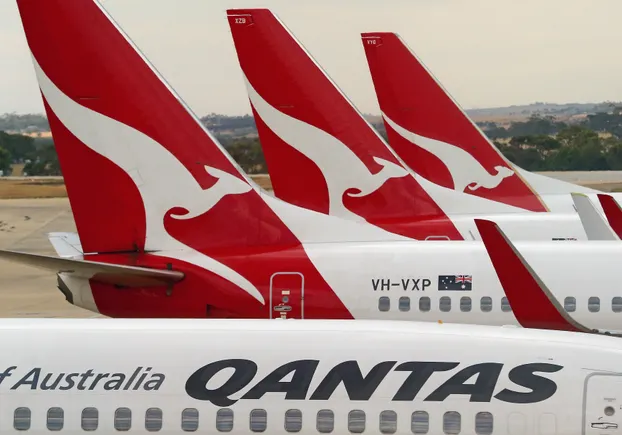
Australian carrier Qantas said hackers who breached one of its call centers stole a significant quantity of customer data. The airline said on its website…
Hackers could subvert frontier models with attacks that their developers overlook, Cisco said. Source link
Xerox has issued a security upgrade for critical and high-severity vulnerabilities in its FreeFlow Core product that researchers said could have allowed an attacker to…
Chief information security officers are increasingly concerned about the risk of a cyberattack, and a growing number say they have experienced a material loss of…
RTX Corp., the parent firm of Collins Aerospace, confirmed that ransomware was used in the hack of its airline passenger processing software, in a filing…