Anthropic’s Claude Code extension for Visual Studio Code reportedly shows misleading file paths in its permission prompts. A researcher says this can lead users to approve file access outside their trusted workspace.
Anthropic closed the report as informative and did not treat it as a vulnerability. The researcher disagrees and says the issue is unpatched in plugin version 2.1.322.
A symbolic link, or symlink, is a filesystem pointer to another file or folder. When Claude Code agent touches a file through a symlink that points outside the workspace, the VS Code plugin asks for approval.
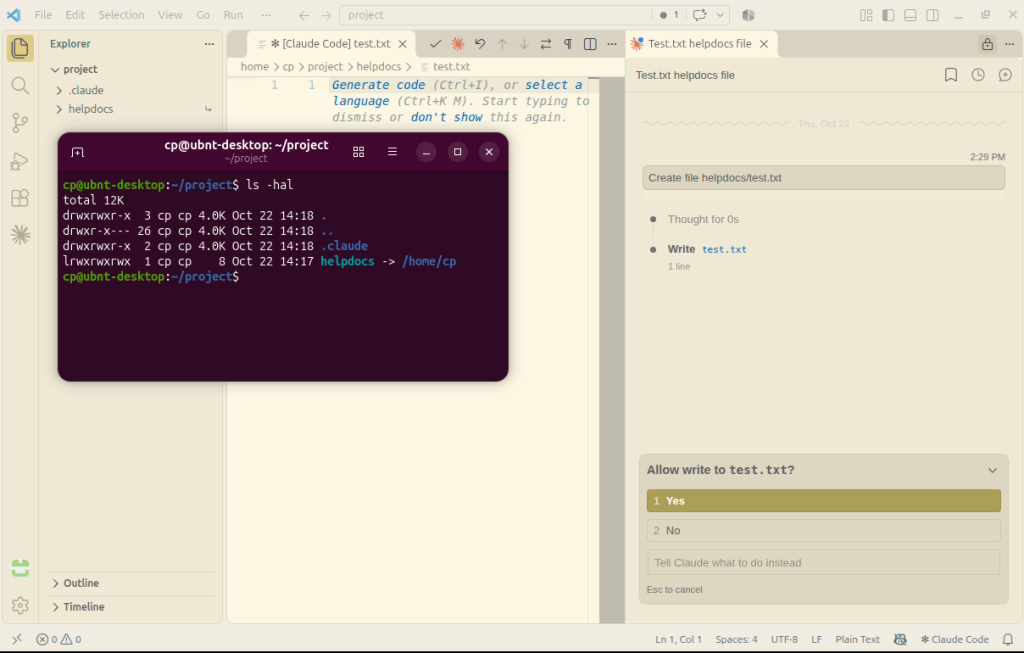
The prompt shows only the workspace-relative path. A link at ./helpdocs that points elsewhere appears as a harmless in-workspace path.
In testing, a request to write test.txt through that link gave no sign that the file would land outside the project.
The user therefore approves a decision based on inaccurate context. A rogue agent, or one steered by prompt injection, could exploit this.
The impact depends on which symlinks exist. A link to a home directory, for example, could expose reads and writes to ~/.ssh/ keys.
A malicious MCP server then runs attacker code on the next restart. Adversa confirmed the technique against Claude Code, Gemini CLI/Antigravity CLI, Cursor Agent CLI, GitHub Copilot CLI, Grok Build and OpenAI Codex CLI.
Claude Code Extension
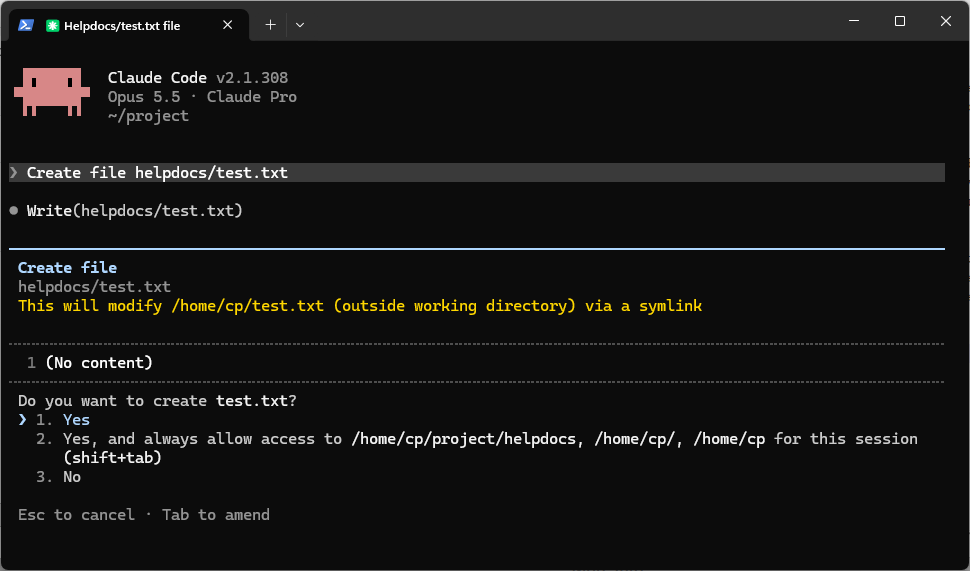
Adversa says Anthropic rejected its report as out of scope. A few weeks later, Anthropic quietly hardened the Claude Code CLI so it resolves symlinks and shows the real destination before asking for approval.
Ultrastrike researcher said that, the finding builds on Adversa AI’s May 2026 “SymJack” research. That research showed that a booby-trapped repository can use a symlinked copy destination to overwrite an agent’s own configuration.
The researcher says Anthropic argued that the prompt itself is sufficient and that its displayed details are not part of the security control. Anthropic also said symlinks fall outside Claude Code’s permission threat model.
According to the researcher, the public HackerOne program guide does not appear to list that exclusion.
The VS Code researcher found that this fix never reached the extension. The extension has over 30 million installs on the Visual Studio Marketplace.
The researcher calls this a UI/UX security issue that enables workspace escape. The trust model assumes that opening a workspace trusts its filesystem, including its symlinks.
The researcher questions why Claude Code prompts for symlink traversal at all if that trust holds. A prompt implies a security boundary.
Two scenarios weaken the trusted-workspace assumption. First, Git supports symlinks. A compromised engineer account could push a malicious commit to a shared repository, and the symlink would then reach colleagues’ workspaces on the next sync.
Second, depending on the permission mode, the plugin may rename workspace files without approval. An agent could rename a familiar symlink, such as ./foo/bar to ./foo/bat.
The user would not recognize the changed name and would assume the path is safe.
Adversa’s own findings point the same way. Informed consent needs an accurate picture of what an action does, and a prompt that withholds the real destination does not provide one.
Until a fix ships, the realistic workaround is manual verification. Before approving a request, run realpath followed by the displayed path in a terminal.
If the resolved location falls outside the workspace or other allowed locations, check the agent’s requested path for symlinks and deny the request.
Adversa recommends that agent vendors resolve symlinks before any permission decision. It also recommends treating shell file operations as first-class writes and showing the canonical destination in the prompt, which is the change Claude Code’s CLI now ships.
For organizations, Adversa advises scanning repositories for tracked symlinks that target configuration files and failing pull requests that modify agent or MCP configuration access.
It also advises isolating CI runners that handle untrusted code from those holding production secrets.
As AI agents gain file and shell access, the approval prompt becomes the main safeguard. Anthropic has already shown it can fix the problem in the CLI.
The extension’s remaining gap leaves a large developer base exposed to a prompt that misstates where a write will land.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC.