
Client-side path traversal vulnerability class explained – $6,580 GitLab bug bounty

Source link
Related Articles
All Mix →
Celebrating 10 Years of Partnership: Snap and HackerOne Reach $1M in Bounties
Q: Tell us about your role at Snap and why cybersecurity is vital to your business. Jim Higgins: I’m Snap’s Chief Information Security Officer (CISO).…
Content Security Policy (CSP) explained including common bypasses
Table of Contents Example policy self inline eval Callback CDN – anyone can upload files CDN – abusing existing libraries Injection in the actual policy…
Newly added security tests, July 6, 2017: OpenVPN CRLF injection
To bring you the most up-to-date security service and help you stay on top of threats, we update Detectify on a regular basis. Here are…
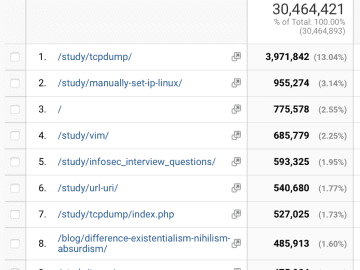
AI is the End of Tutorial Webpages
AI’s are far better at finding the answer you’re looking for and giving it to you directly Created/Updated: April 6, 2023 Since 1999, most of…

Your Grab public bug bounty program is arriving now
Any hackers out there ever hunt for bugs on your mobile phone while riding in a car? Well, now our thousands of hackers in Southeast…

Live Recon Stream #2
Live Recon Stream #2 Source link