
Common Open Redirection Bug Bounty Mistakes

Source link
Related Articles
All Mix →
[tl;dr sec] #290 – Securing MCP, AppSec Archetypes, CISO’s Guide to Protecting Crown Jewels
Table of Contents Tools to scan MCP servers and an MCP WAF, 4 AppSec archetypes, how to strategically protect your org with limited resources AppSec…
The Future Of Hacking #shorts
The Future Of Hacking #shorts Source link
My Thoughts on Depression | Daniel Miessler
A new BBC piece is highlighting an alternate approach to depression. Rather than assume that it’s something that should immediately be countered with drugs, how…
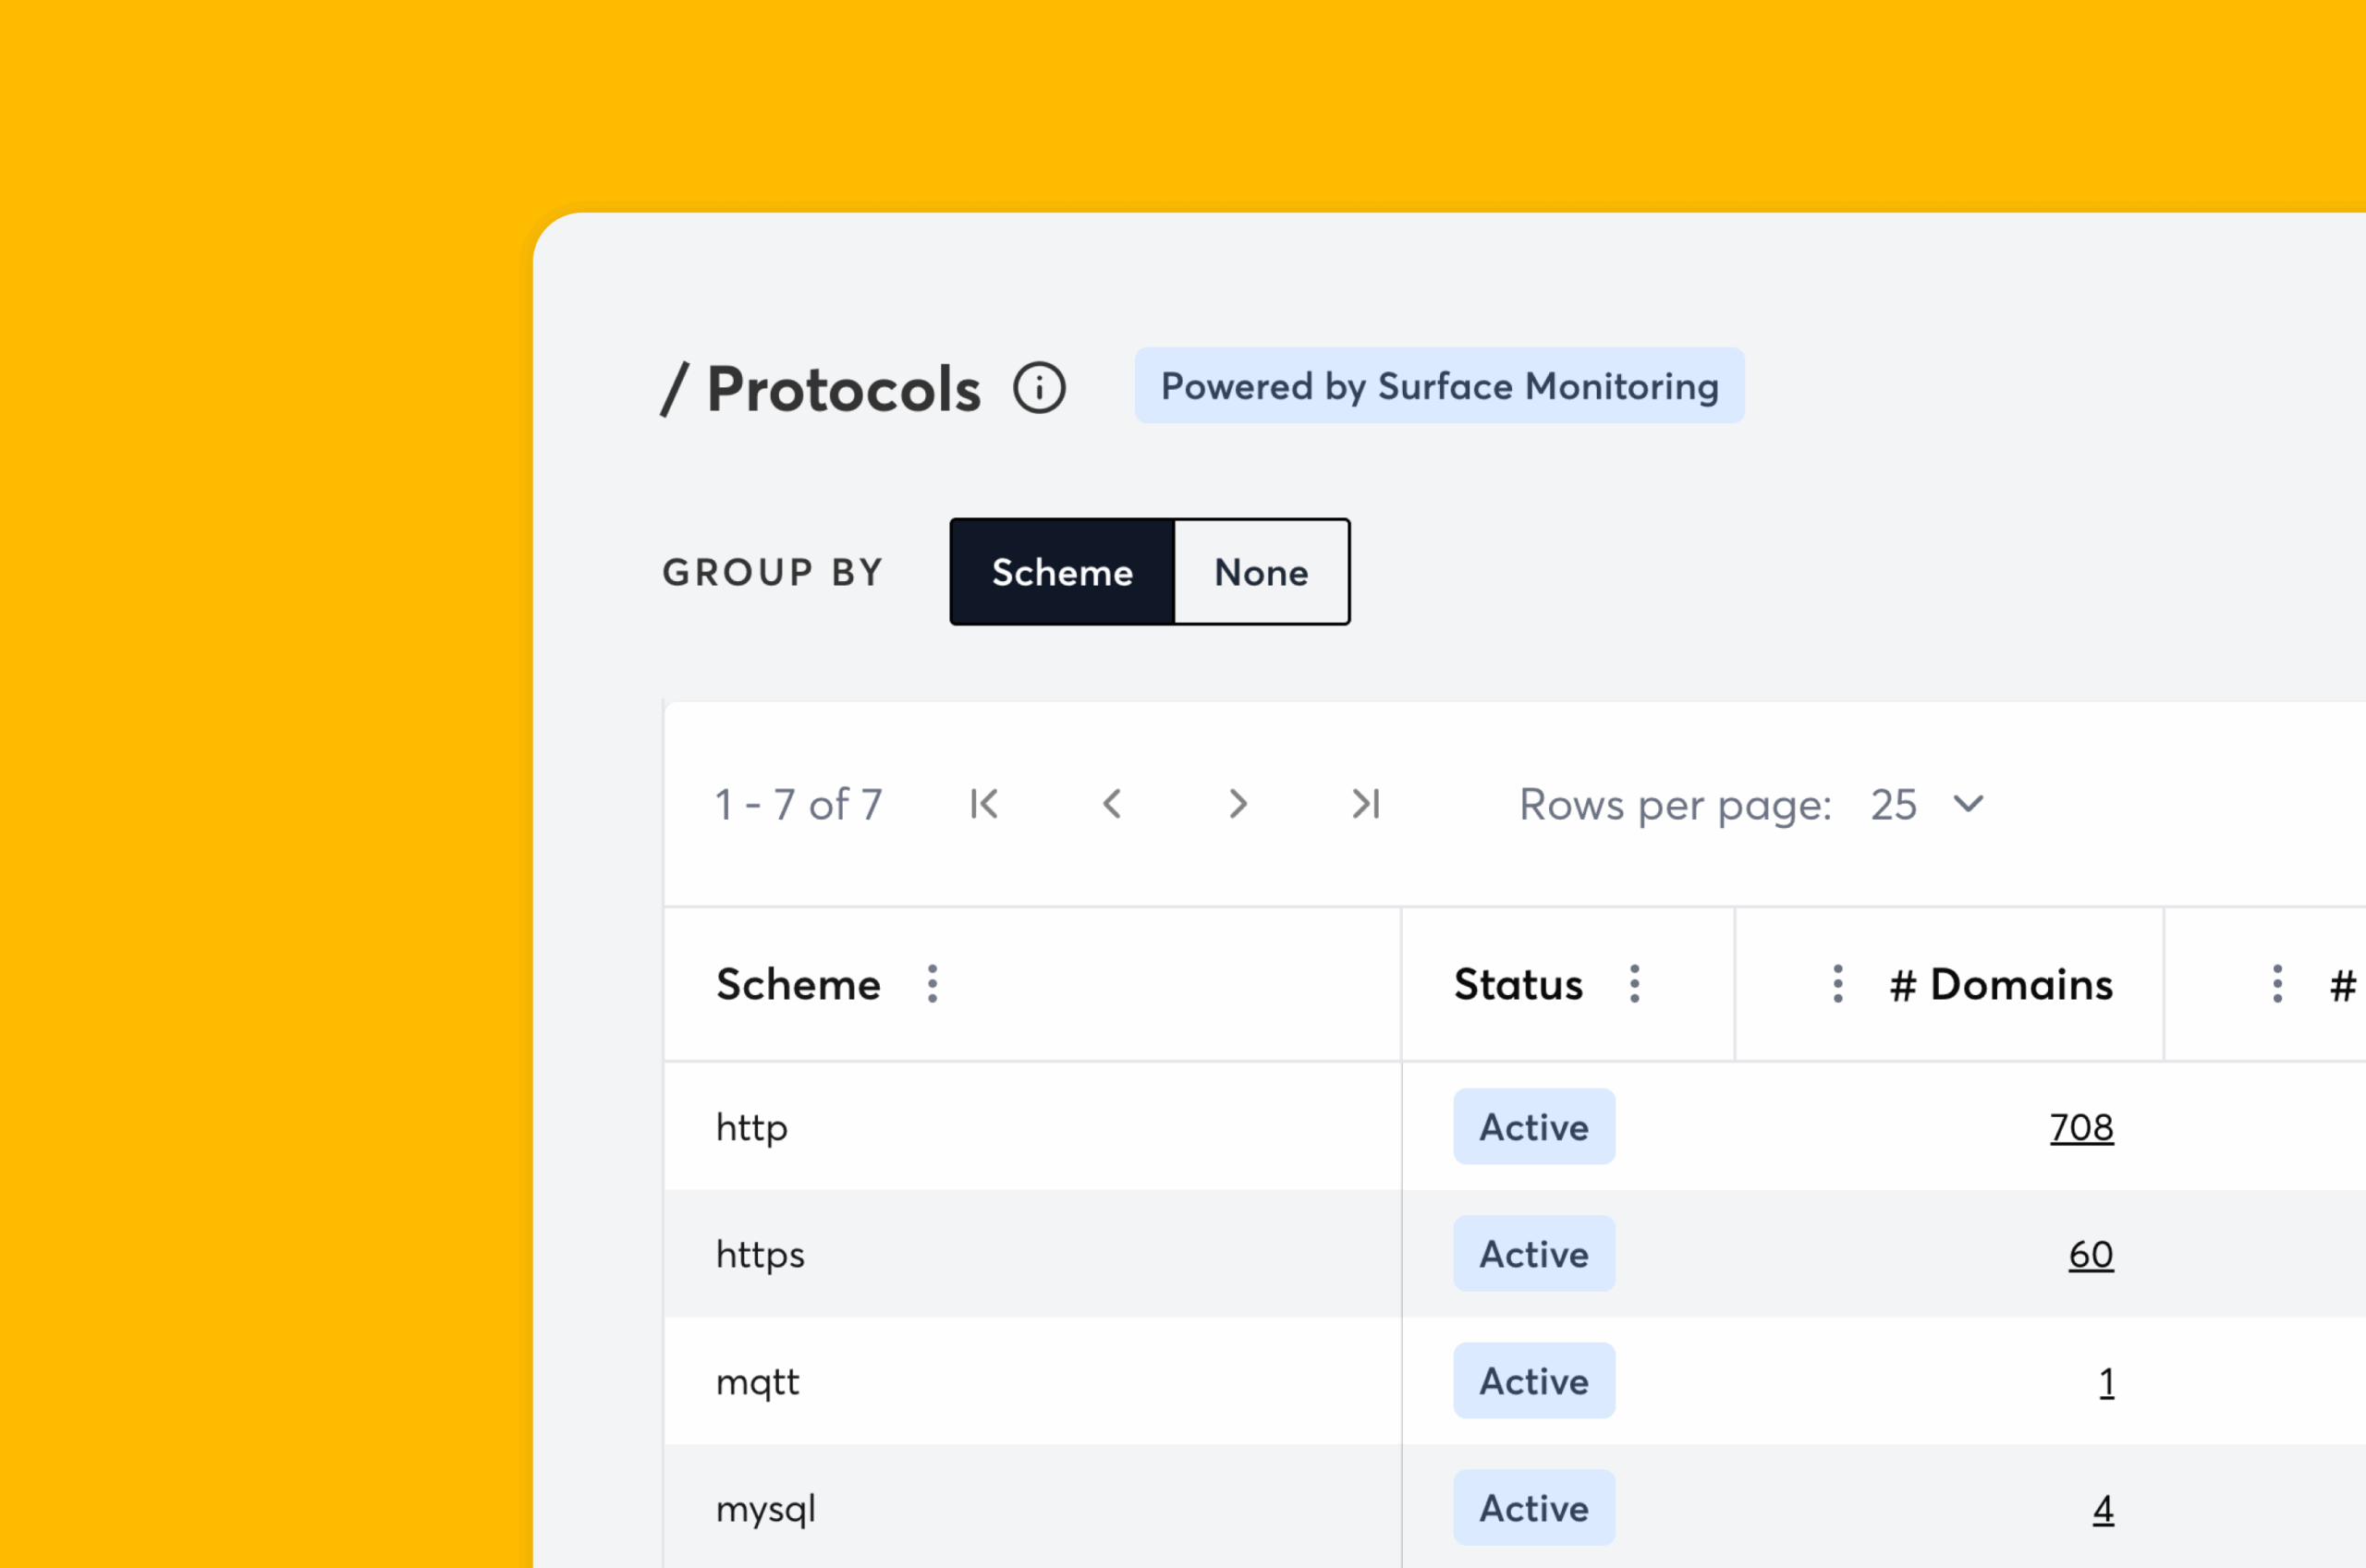
Introducing Protocol Discovery to stop guessing what’s behind your open ports
Table of Contents Engineering a better Discovery engine Deep visibility into niche & legacy protocols What’s new in your dashboard? Get started Most tools will…
Six years of the GitHub Security Bug Bounty program
This guest blog post was authored by Brian Anglin, Application Security Engineer at GitHub and originally published on the GitHub company blog. Last month GitHub…
Harnessing the Working Genius for Team Success
Table of Contents The Six Types of Working Genius How HackerOne Introduced the Working Genius Working Genius in Real Life Employees at HackerOne utilize…