An ongoing malware campaign uses SEO-optimized GitHub repositories to impersonate well-known software firms to push a previously undocumented information stealer called Rapuncel.
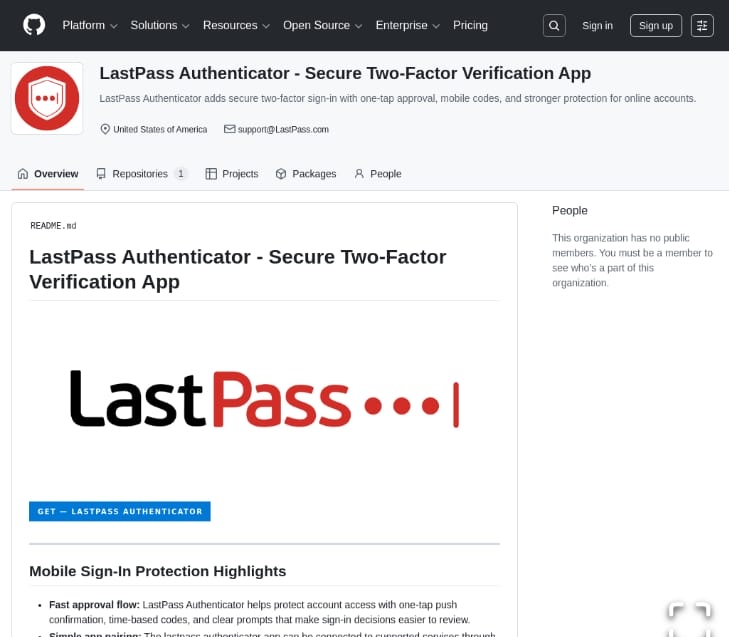
LastPass and Delphos Labs uncovered the campaign, which they report impersonates the password manager brand and at least 39 other companies.
Alongside the Rapuncel infostealer, the repositories deliver a Microsoft-signed kernel driver that can disable 145 antivirus and endpoint detection and response (EDR) products.
The attack chain begins when victims search for LastPass Authenticator or other popular software and follow links to fake GitHub repos.
There, clicking download buttons triggers a series of redirections before reaching payload-delivery servers, where victims receive ZIP archives with their size inflated to up to 148MB to evade security scans.
The installer inside the archives is a copy of the legitimate Microsoft Visual Studio CoreCLR Debugger, ‘vsdbg.exe,’ renamed and configured to sideload a malicious DLL (vsdbg.dll). The installer deploys the Rapuncel infostealer as well as the Alinubx.sys kernel driver, which is used to kill antivirus software.
Source: LastPass
The kernel driver is disguised as an NVIDIA component named ‘nvfsflt64.sys’ and registers as the NvFsFilter service.
According to the researchers, the driver acts as an EDR killer that contains a hardcoded list of 145 antivirus and EDR processes that it aims to terminate.
“The driver calls ObOpenObjectByPointer with AccessMode=KernelMode, which bypasses the normal user-mode SeAccessCheck path at handle-open time,” explains LastPass.
“It asks the kernel to open the process as kernel code, then kills it. That is why it can defeat Protected Process Light (PPL); the protection many security products rely on to survive an administrator.”
Currently, the driver is not in Microsoft’s vulnerable drivers blocklist, and the one used in the campaign is signed through Microsoft’s Windows Hardware Compatibility Publisher chain.
The researchers noted that Alinubx.sys contains additional capabilities for file and registry hiding, DLL injection, driver and process interception, traffic manipulation, and port redirection, but do not appear to be activated in this campaign.
The Rapuncel infostealer
Once security software is terminated on the device, the Rapuncel infostealer begins stealing data from the infected device.
The malware collects the following information:
- Credentials stored in 25 web browsers
- Data from 30 cryptocurrency wallets
- Discord, Steam, and Telegram session credentials
- Windows Credential Manager contents
- Documents with names containing “password,” “seed,” “wallet,” or “recovery”
- Screenshots from every connected monitor
- Detailed system information
To bypass Google’s app-bound encryption protection present on Chrome, Edge, and related browsers, Rapuncel injects a helper DLL into the app and invokes its own Elevation Service.
The stolen information is compressed and uploaded to an external endpoint at ‘2.26.126[.]50‘ using an HTTP-formatted request sent over raw TCP.
Rapuncel persists across reboots via a Windows service, so any security tools that reactivate are killed again before the infostealer launches.
LastPass and Delphos Labs assessed with moderate confidence that Rapuncel is a variant of BoryptGrab, while they also found that its loader was built with the Cruciferra PUROSANGUE crypter.
Users are recommended to only download software from official websites, avoid dubious GitHub repositories, and skip or block promoted results on Google Search.

Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Save your seat