
Fundamentals of Bug Bounty Recon

Source link
Related Articles
All Mix →
Broken Access Control – Lab #12 Multi-step process with no access control on one step | Long Version
Broken Access Control – Lab #12 Multi-step process with no access control on one step | Long Version Source link

[www.32red.com] Reverse proxy misconfiguration leads to 1-click account takeover
Kindred Group disclosed a bug submitted by sw33tlie: https://hackerone.com/reports/1632973 – Bounty: $5250 Source link
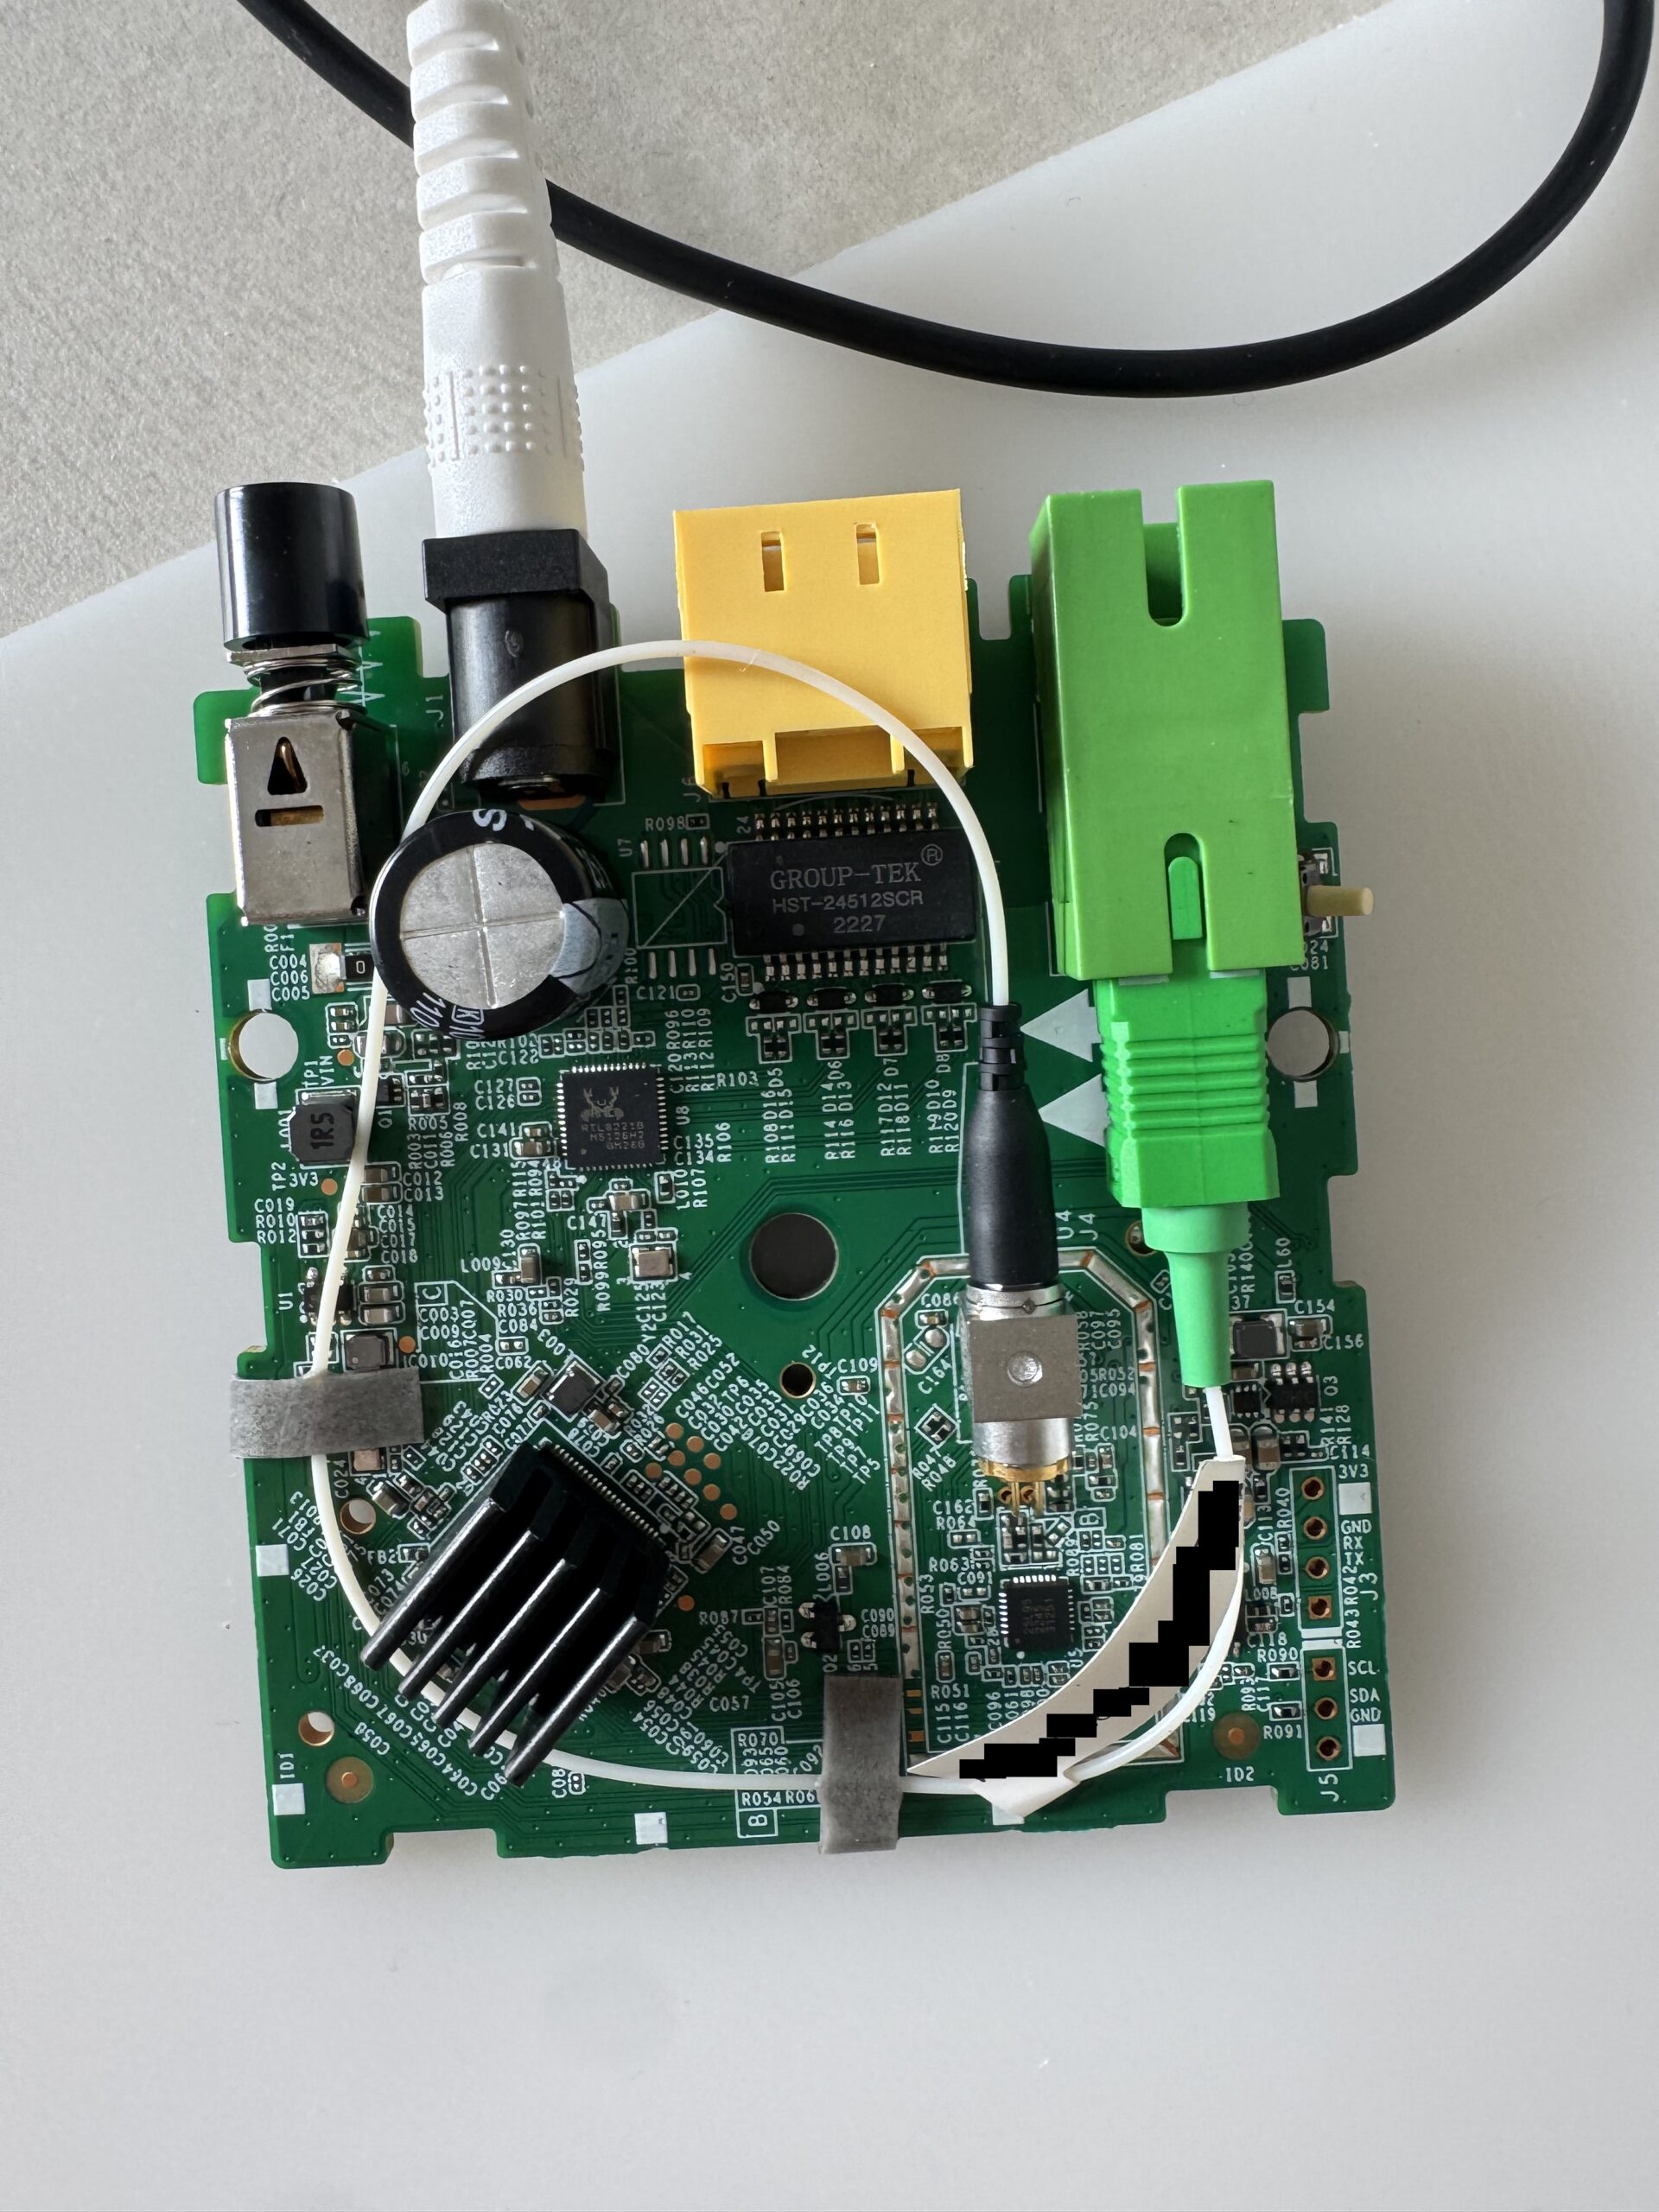
Getting a Shell on the LAU-G150-C Optical Network Terminal
Optical Network Terminals (ONTs) are devices that convert fiber optic signals to Ethernet signals that can be handled by typical routers. As the connection between…

Finding XSS in a million websites (cPanel CVE-2023-29489) – Assetnote
cPanel is a web hosting control panel software that is deployed widely across the internet. To be exact, there are about ~1.4 million installations of…
XXE-scape through the front door: circumventing the firewall with HTTP request smuggling
Table of Contents The Hole in the Wall The Great Escape Lessons learned Timeline In this write-up, I want to share a cool way in…

parameter pollution bug at twitter | by mert tasci
mert tasci · Follow 1 min read · Mar 11, 2023 — 1 Listen Share twitter sent an e-mail to you when someone followed you…