Antidetect browsers tools that create separate browser profiles with altered digital fingerprints could help scammers operate thousands of apparently unrelated social media accounts.
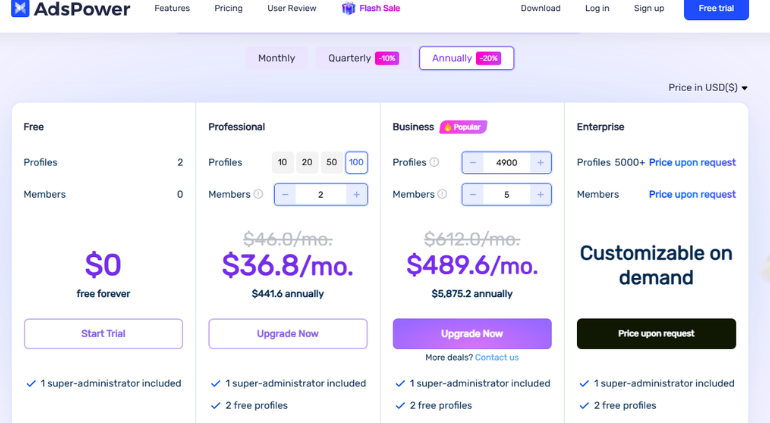
The research focuses on Kameleo, AdsPower and MultiLogin, commercially available platforms with legitimate uses in marketing, e-commerce and privacy protection.
Researchers say they also found the tools referenced in criminal forums and marketplaces in connection with account takeovers, payment fraud, fake loan applications and bulk creation of accounts for advertising fraud.
A browser fingerprint is the collection of technical signals a website can use to distinguish one device or browser from another. These can include screen resolution, time zone, fonts, user-agent details, and Canvas or WebGL output.
Antidetect browsers let users configure separate profiles so those signals appear different across accounts. When combined with proxy services, the profiles can also appear to connect from different network locations.
This creates a challenge for platforms that identify coordinated abuse by correlating account, device and behavior signals.
The tools do not make accounts inherently invisible, but they can make some commonly used identity signals less reliable.
Artificial intelligence could make these operations easier to run. AdsPower advertises an MCP server that connects AI systems to its Local API and supports browser-automation tasks.
Check Point says that stolen session cookies can also be loaded into browser profiles, potentially allowing criminals to access an already authenticated account without triggering a conventional login event.
Check Point Research said that, the risk is growing as these products combine identity masking with automation and AI integrations, lowering the effort needed to scale account fraud and coordinated influence campaigns.
Gemini-Compatible AI Browsers
MCP, or Model Context Protocol, is a standard for connecting AI models to external tools and services. Check Point warns that AI-generated content combined with automation could help operators distribute material across multiple profiles with less manual work.
In a Browser-in-the-Middle attack, the phishing server instructs the antidetect browser to create a new profile for the victim, assigned a residential proxy in their country and a clean device fingerprint.
Account editor supports platforms spanning social media, e-commerce, financial services, and professional networks including Facebook, Amazon, LinkedIn, X, PayPal, and Google.
The headline’s reference to Gemini-compatible browsers should be understood as a compatibility concern, not as evidence that Google’s Gemini product is itself malicious or that the researchers demonstrated a specific Gemini-driven campaign.
AdsPower’s documentation describes MCP support for Claude Desktop, Cursor and other compatible tools; it does not name Gemini in the material reviewed.
AdsPower’s own site also advertises integrations with AI agents and automation scripts.
The researchers describe a broader criminal ecosystem around these tools. Their report cites underground advertisements for credential-harvesting services that export stolen session data to antidetect browsers, as well as malware advertised as compatible with multiple browser platforms.
The potential consequences extend from phishing and account theft to fraudulent transactions and coordinated efforts to manipulate online discussion.
The threat is not limited to social networks. Check Point says attackers used antidetect profiles, residential proxies, CAPTCHA-solving and identity-verification bypass tools in a campaign targeting cryptocurrency exchanges and financial marketplaces, citing Anthropic’s September 2026 threat-intelligence report.
Accounts that pass onboarding checks and develop a history of apparently normal activity may be harder to flag before they are abused.
Check Point emphasizes that the software has legitimate applications; the risk lies in how criminals combine its features with stolen credentials, proxies and automation.
For organizations, researchers recommend looking beyond a single account’s activity and reviewing infrastructure and session signals, including large-scale proxy use, unusual session-cookie activity and signs of pre-authenticated access.
They also advise reassessing fraud controls that depend heavily on device consistency.
The central concern is a change in scale: automation can reduce the time and expertise needed to manage many online identities.
But researchers’ findings do not mean every user of an antidetect browser is acting maliciously, nor that AI alone can bypass platform defenses.
The warning is that identity-masking tools and AI-assisted workflows, when combined with criminal infrastructure, can make coordinated fraud and manipulation harder to detect.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC.