Google has enhanced Chrome’s AI-powered scam defenses with a new server-side Gemini model that detects fake antivirus alerts, fraudulent browser updates, and other deceptive websites.
Announced on October 20, 2026, these changes expand protection to all users who enable Safe Browsing’s Enhanced Protection mode.
This update builds on the earlier on-device Gemini integration introduced in 2025, which identified technical support scams on supported devices.
By moving the analysis to a more powerful server-side model, Chrome can broaden device coverage and assess a wider range of scams.
Gemini AI to Detect Fake Antivirus
Gemini analyzes page content to identify the brand, assess the page’s intent, and generate a scam likelihood score. Safe Browsing combines this evaluation with domain reputation and additional security signals to issue a final verdict. Therefore, Gemini adds contextual analysis rather than independently determining whether a website is dangerous.
Google states that Chrome limits server-side analysis to the text of pages that already show high-confidence scam indicators. The content processed for this purpose is ephemeral: it is not logged, retained, or used to train models. This approach minimizes the data shared while allowing for a deeper inspection of suspicious content.
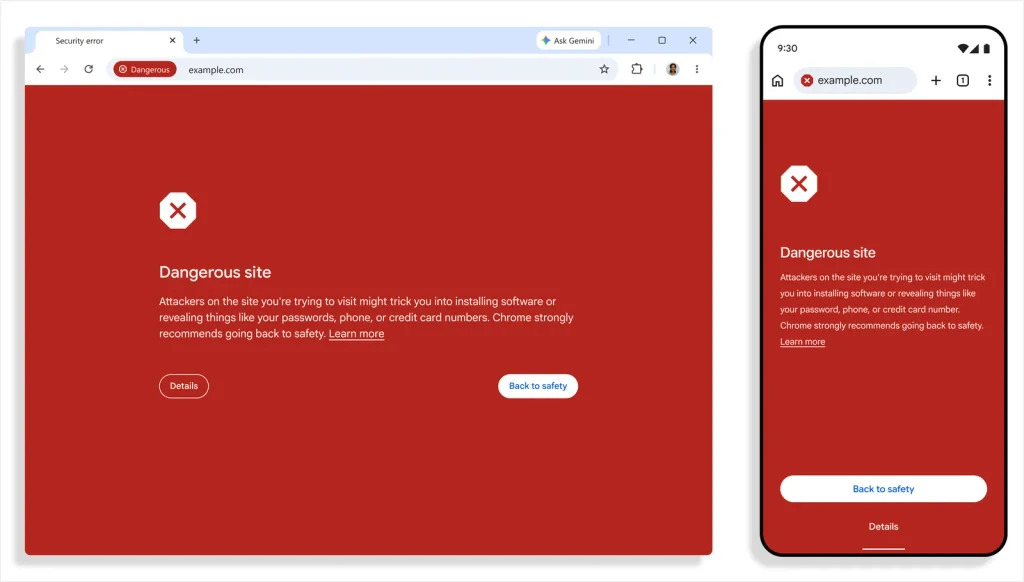
Chrome is also introducing separate warning categories for suspicious and dangerous websites under Enhanced Protection. Suspicious warnings cover lower-confidence findings that involve deceptive patterns associated with malicious sites.
The presentation of these warnings varies in wording, colors, icons, and layout, enabling Chrome to alert users about potentially harmful pages.
In contrast, Chrome reserves dangerous verdicts for known malicious pages that pose a high risk of harm. These still trigger Chrome’s familiar full-page red warning, keeping a clear distinction between possible deception and confirmed threats.
Another new defense targets ClickFix attacks, which trick users into copying and executing commands that are falsely claimed to fix a made-up problem.
These commands often use legitimate operating system utilities, such as PowerShell and cmd.exe, to download or install malware. Executing these commands in a terminal can bypass browser-based download protections.
Chrome now detects potentially malicious commands that are copied during suspected ClickFix activity. It removes personally identifiable information from the clipboard content before sending it to Safe Browsing.
If it issues a dangerous verdict, it triggers a warning; Google notes that the system prioritizes precision to reduce interference with legitimate developer workflows.
These protections require Enhanced Protection to be enabled. Google’s claim of “ten times safer” compares the average number of warnings between different protection modes, rather than directly measuring a tenfold reduction in successful compromises. This distinction is important when interpreting the company’s security claims.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC.