Hackers accessed LiteLLM’s GitHub organization and executed credential-stealing workflows eleven days before the October 21 supply chain attack that distributed malicious litellm==1.107.0 packages.
The findings establish a longer compromise window preceding the poisoned releases. Socket recovered malicious workflows executed inside BerriAI/litellm on October 10 and October 12, 2026.
Both used the maintenance-style commit message ci: bump cache config while introducing .github/workflows/cache.yml, a file designed to collect continuous integration secrets and transmit them to attacker-controlled endpoints.
Hackers Breached LiteLLM GitHub Repository
The attacker created temporary branches from legitimate commits, pushed the malicious workflow, allowed GitHub Actions to execute, and deleted the branches.
Named ci-tmp-a351cc and ci-tmp-4d8517, these branches disappeared without merging the workflow into main, limiting visibility during routine repository reviews.
The October 10 workflow contained one job targeting six configured secrets, including GH_TOKEN, a GitHub App private key, and credentials associated with LiteLLM, Linear, and Together AI.
It wrote the values into /tmp/c.env, encoded the file into /tmp/c.b64, and used curl to POST the resulting content to webhook.site. A trailing || true suppressed transmission errors.
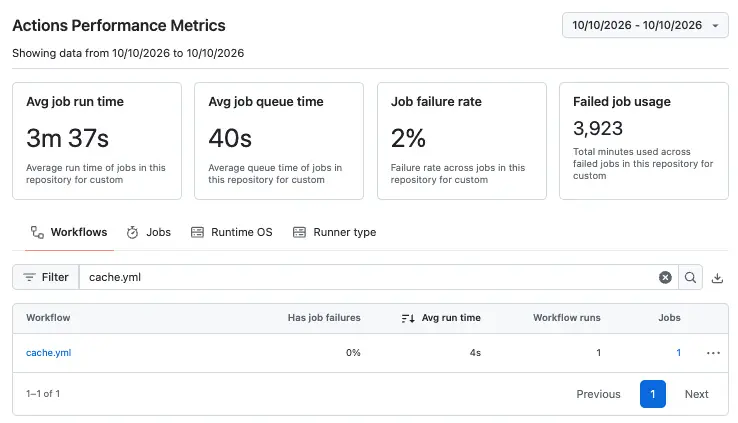
As a result, the job could report success even when exfiltration failed. GitHub Actions performance metrics recorded one successful execution lasting approximately four seconds, but those metrics alone could not establish whether the collector received the credentials.
The October 12 variant expanded collection to six jobs, five bound to configured GitHub environments. Across both workflows, attackers referenced 20 distinct secret names covering OpenAI, Anthropic, AWS Bedrock, GitGuardian, PostgreSQL, Redis, and Linear browser session material.
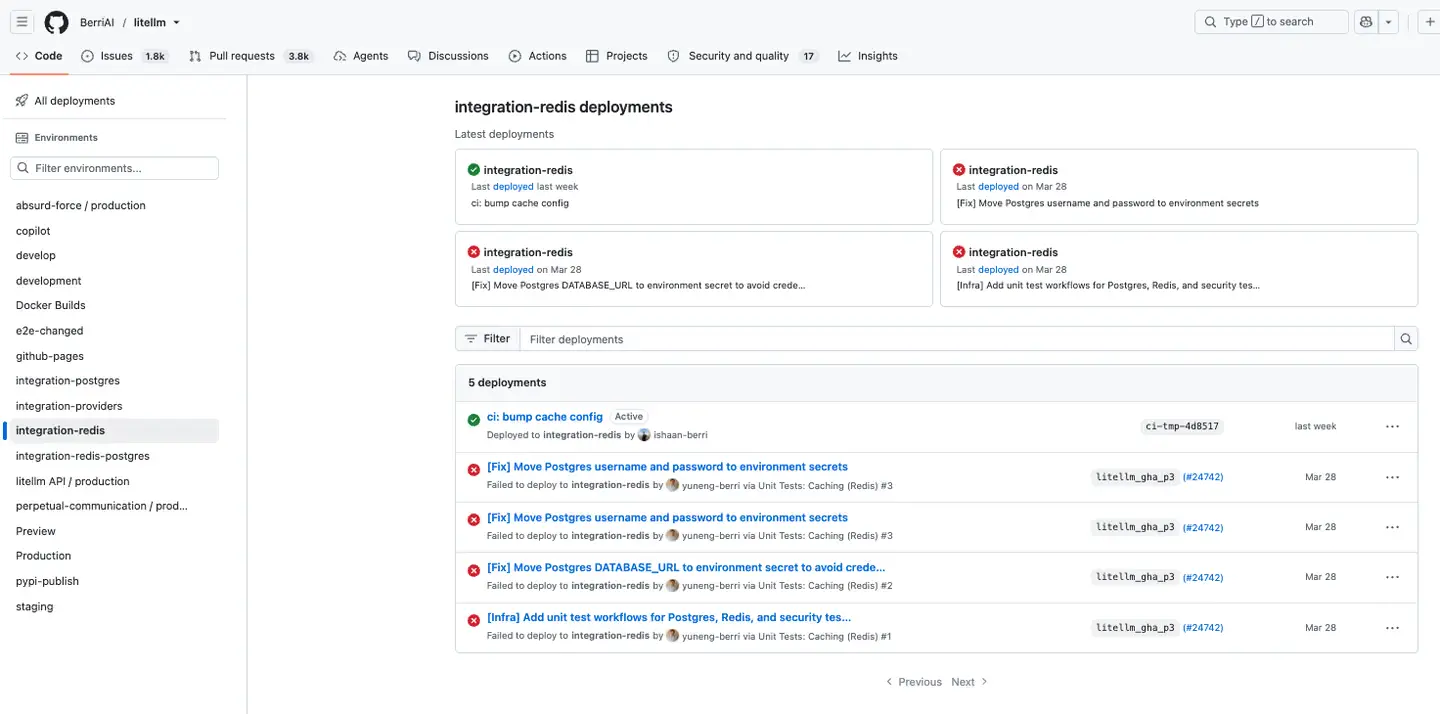
Persistent environment deployment records corroborated execution after the branches were deleted. LiteLLM’s investigation traced initial access to an Agent Platform master key accidentally committed publicly on May 27 and never revoked.
On October 10, the attacker used that key to retrieve an unrestricted GitHub CLI OAuth token belonging to an organization owner. The resulting access enabled additional credential theft. LiteLLM said audit-log token hashes connected the GH_TOKEN stolen from BerriAI/litellm to approval of the malicious production release.
Another stolen maintainer token was used to delete release workflow records. On October 21, the attacker bypassed branch protections using owner privileges and redirected the release pipeline toward the lookalike Berri-AI/litellm repository.
The pipeline subsequently signed and published seven malicious PyPI wheels and compromised container images. LiteLLM locked registries, removed all but one trusted GitHub organization member, and began revoking credentials across internal systems and vendors.
Socket cautioned that October 10 represents the earliest activity it could substantiate, not necessarily the intrusion’s beginning. Deleted branches and successful workflow statuses therefore leave important uncertainty about the compromise’s complete duration and scope.
IOCs
| Category | Indicator / Value | Associated Date / Details |
|---|---|---|
| Exfiltration endpoint | hxxps://webhook[.]site/65a42464-3cfa-4b02-a18c-17a6d7b86f37 | October 10, 2026 |
| Exfiltration endpoint | hxxps://webhook[.]site/4da03473-a3e7-4dc2-a087-9c564b4208e1 | October 12, 2026 |
| HTTP request header | X-Tag: lm1 | October 10 workflow |
| HTTP request header values | X-Tag: org, X-Tag: e2e, X-Tag: intpg, X-Tag: intprov, X-Tag: intredis, X-Tag: intrp | October 12 workflow |
| Malicious workflow file | .github/workflows/cache.yml | Workflow used for secret exfiltration |
| Git commit | b69bc36fd4e23b23ea09f4ce63a92b07258f5044 | October 10, 2026 |
| Git commit | 1a6e3c1e41f1b5c8eeaeeb2ae94bcd95390fa891 | October 12, 2026 |
| Temporary branch | ci-tmp-a351cc | Created and deleted on October 10 |
| Temporary branch | ci-tmp-4d8517 | Created and deleted on October 12 |
| Environment deployment reference | ci-tmp-4d8517 | Deployment remained marked Active |
| Runner filesystem artifact | /tmp/c.env | File containing collected secret values |
| Runner filesystem artifact | /tmp/c.b64 | Base64-encoded file prepared for exfiltration |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Join 16,000+ SOC teams using ANY.RUN to streamline threat investigations and reduce manual effort. Explore for your team