Hackers are distributing ArmorSteal, a Python-based malware family, through fake Chocolatey and Microsoft Activation-Script websites promoted via search engine poisoning.
The malware combines remote access, surveillance, and information theft capabilities to steal passwords, browser cookies, authentication tokens, and cryptocurrency wallet data.
Zscaler’s Threat Hunting team identified the campaign in September 2026 and published its findings on October 22. The operation targets users searching for installation commands, turning routine software setup into an infection pathway.
Hackers Use Fake Chocolatey and Microsoft Activation Websites
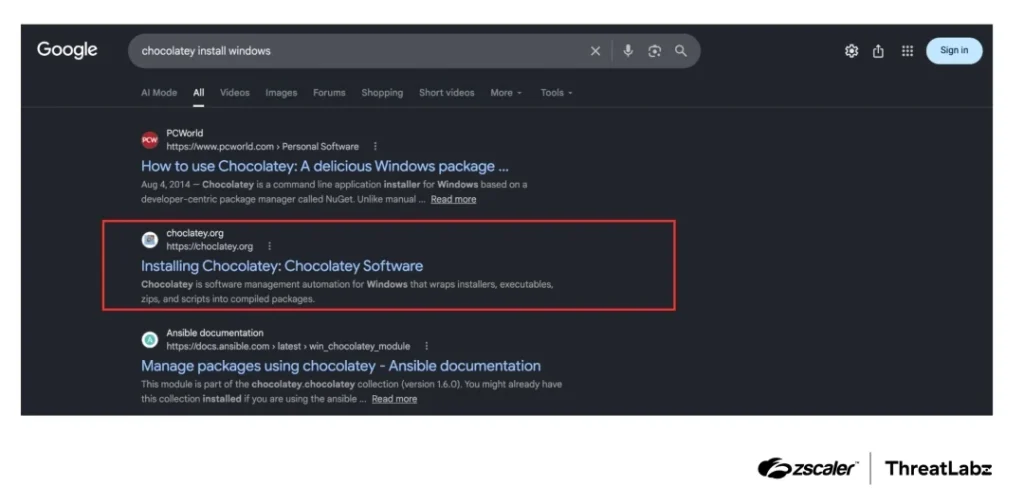
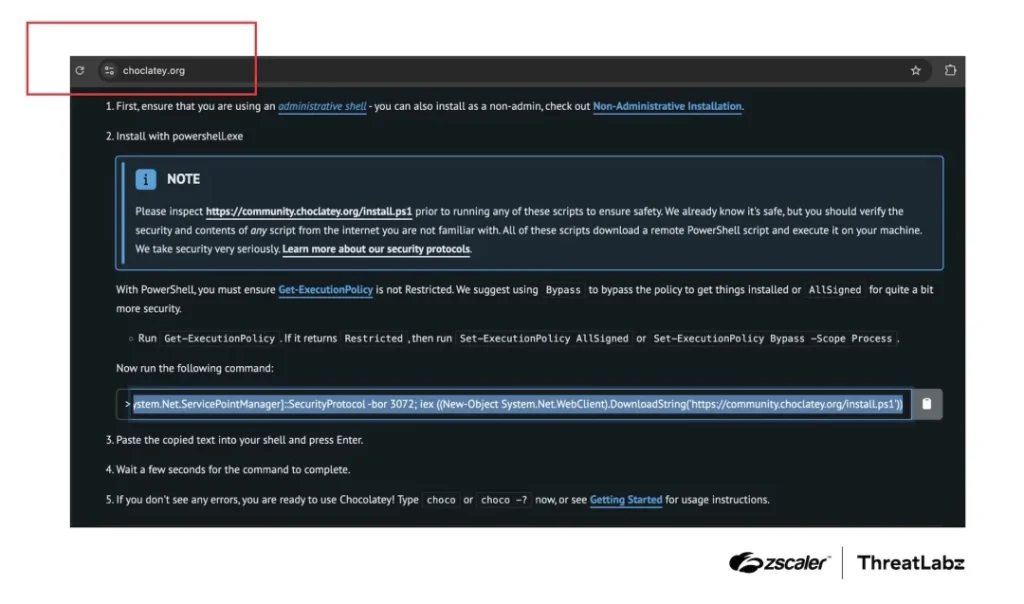
The typosquatted domain choclatey[.]org impersonated Chocolatey and displayed a malicious PowerShell installation command. Executing it deployed ArmorSteal while also running the legitimate Chocolatey installer, allowing the requested package manager to function normally and reducing visible signs of compromise.
A second domain, massgravel[.]net, impersonated the Microsoft Activation Scripts project. Shared malware components and an identical RSA-2048 task-signing key linked both distribution channels to the same operation.
Both installers request elevated privileges, hide the PowerShell console, and download an archive into C:WindowsSystemHealthUpdate. The package contains Python 3.11, Pyarmor runtime files, and malicious scripts protected with Pyarmor 9.1.7.
Persistence uses two scheduled tasks. SysCheck2 launches the remote access module at user logon with the highest available privileges. SysCheckX executes it as SYSTEM, following a 45-second delay after startup.
The remote access module, SysMon.py, profiles infected systems and derives a machine identifier from the motherboard serial number. It polls command-and-control servers every 60 seconds for victim-specific and campaign-wide Python tasks.
Before executing tasks in memory, the module verifies RSA-2048 signatures and compares version numbers against locally stored values, preventing older or previously processed instructions from running again.
ArmorSteal queries ipinfo[.]io for public IP ownership. When selected cloud providers appear in the organization field, it displays a fake memory error and exits, potentially evading cloud-hosted analysis environments.
The basrq.py surveillance module logs keystrokes and window titles, checks clipboard contents every half-second, and replaces cryptocurrency addresses. It also captures keyword-triggered screenshots and displays fake Exodus, MetaMask, and Phantom transaction notifications.
The got.py stealer targets browser passwords, autofill records, credit card metadata, SSH keys, Steam sessions, and password manager data. It validates tokens from 22 Discord client variants and collects information from 21 wallet extensions and desktop applications.
Zscaler said browser cookies are extracted through Chrome DevTools Protocol on port 9222, while additional routines search drives for BIP39 recovery phrases.
Although both lure sites went offline, operators shifted infrastructure toward pymons[.]is and datamons[.]org. Defenders should investigate the scheduled tasks, inspect the SystemHealth directory, review PowerShell downloads, monitor browser remote-debugging activity, and remove unauthorized Microsoft Defender exclusions.
IOCs
| Category | Indicator / SHA256 | Filename | Description |
|---|---|---|---|
| File | f3846ec2a6ff0a27d9ef2b9bf7908743b81d295ef29344acfb96ff83fff994f9 | install.ps1 | MAS lure installer |
| File | fb1181160e9f10ce1eb5e5dc9bc23e1498a39110ee9ea361fd150454cb01b292 | install.ps1 | Chocolatey lure installer |
| File | 3e3b62a9836697d978cbb620dc8af8f6eefdf8cb73fc30d16bb394d1c58f4c97 | Update.zip / Updatef.zip | Remote access module |
| File | 237ba698d7dc8936c43e0e78e7644002375e51e8baf9b3a7d4e18683f871ee31 | nig20084.zip | Surveillance module |
| File | be0329d0795dd62ae587faf97e704bb36413e5c98ddd8fe575f5077db3c84e5f | getthem20084.zip | Stealer module |
| File | 04d2828155ed2a276cfd3c97d4f966d328391dd818e04e773212cd601e49fa74 | nig20083.zip | Older stealer module |
| File | 56f05c4fb1c25c04e0dde60e2e5e41ac164a6dc53688d0f9eb52a55f82106389 | getthem20083.zip | Older stealer module |
| File | 0ea99fbbe29af6f797e3866ed5f822c7a5d3e9cdb990a8c382a715069f156499 | SysMon.py | Remote access module |
| File | 8fb7aaf2b9270b8b75f6844aaefd5242b4f926fb89cba10fff3d9b908a769788 | basrq.py | Surveillance module |
| File | 5410c2f239c3649928383c4478dea182f90b21f5b258081fec07e9d297ae4b1c | got.py | Stealer module |
| Domain | choclatey[.]org | — | Fake Chocolatey domain |
| Domain | massgravel[.]net | — | Fake MAS domain |
| Domain | workerstats[.]net | — | C2 domain |
| Domain | pymons[.]is | — | C2 domain |
| Domain | datamons[.]org | — | Initially standby C2; later active |
| Domain | niceer[.]net | — | Standby C2 |
| Domain | supertrap[.]net | — | Standby C2 |
| IP address | 82[.]153[.]135[.]80 | — | Payload host |
| IP address | 186[.]2[.]175[.]183 | — | C2 IP address |
| IP address | 186[.]2[.]163[.]185 | — | C2 IP address |
| IP address | 190[.]115[.]31[.]69 | — | C2 IP address |
| IP address | 209[.]99[.]186[.]187 | — | Payload host |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Join 16,000+ SOC teams using ANY.RUN to streamline threat investigations and reduce manual effort. Explore for your team