Data Privacy
,
Data Security
,
Fraud Management & Cybercrime
Study Warns of Rising Attacks, Care Disruptions, Added Costs and New AI Risks
The frequency of cyberattacks on healthcare organizations, the disruption of those incidents on patient care, workflow and hospital operations – and their associated financial costs – are climbing, according to new research.
See Also: When Ransomware Targets Your Last Line of Defense
A survey of 705 IT and IT security practitioners at U.S. healthcare institutions conducted in May 2026 found that nearly all organizations had experienced at least one cyberattack within the last year, according to the new report by the research firm Ponemon Institute and security vendor Proofpoint released on Tuesday.
Operational disruption expenses related to the attacks now account for the single-largest cost of a cyberattack, averaging $1.39 million, the research found. That’s up from $1.2 million in 2025, which includes expenses stemming from system unavailability.
“When critical systems go down, the consequences extend well beyond financial losses to delayed procedures, longer hospital stays and interruptions in essential patient services,” said Susan Biddle, director of healthcare solutions at Proofpoint.
We’re seeing more attacks, higher costs and greater disruption to patient care,” she told ISMG.
In fact, 97% of survey respondents said their organizations experienced at least one cyberattack in the past 12 months, of which 74% reported disruption to patient care as a result. The average number of attacks organizations reported also rose – to 51, from 43 in 2025.
The average cost of the most expensive cyberattack also rose nearly 8% to $4.2 million, up from $3.9 million in 2025.
“What concerns me most is that cyberattacks are increasingly becoming healthcare operational crises, not just IT incidents,” Biddle said.
But when it comes to the costs associated with the attacks, fewer healthcare organizations are paying extortion demands even as ransomware continues to disrupt patient care. “It’s a reminder that avoiding a ransom payment doesn’t necessarily mean avoiding the consequences of an attack,” she said.
“Ultimately, the findings point to a broader shift in how we think about healthcare cybersecurity. Success can’t be measured only by the attacks stopped or data protected. It also has to be measured by whether clinicians can continue doing their jobs and patients can continue receiving care.”
At the same time, healthcare providers are embracing AI faster than they can secure and govern it, she said. The survey found that 45% of organizations have embedded AI in cybersecurity – or in both cybersecurity and patient care – while another 30% plan to adopt it.
Sixty percent of the respondents admitted their organizations lacked controls governing sensitive data used in AI systems, with only 42% saying they use security measures designed for AI.
Those Ponemon Institute/Proofpoint findings appear to sync with other recent findings by other researchers. For instance, recent research by privacy and security consulting firm Clearwater found similar gaps between AI adoption in healthcare and the lack of governance (see: Healthcare AI Governance Has Visibility Problem).
AI technologies hold enormous promise for improving care and efficiency, but many organizations still lack the visibility and governance needed to manage the risks, Biddle said. “That gap is particularly concerning in an industry where sensitive data and operational continuity are so closely tied to patient outcomes.”
The AI-specific risk of greatest concern according to nearly 40% of the survey respondents was supply chain risk from AI vendors. That was followed by other AI risk concerns, including data leakage via prompts; AI-generated phishing and social engineering scams; inadequate privacy protections; and non-compliant tool usage.
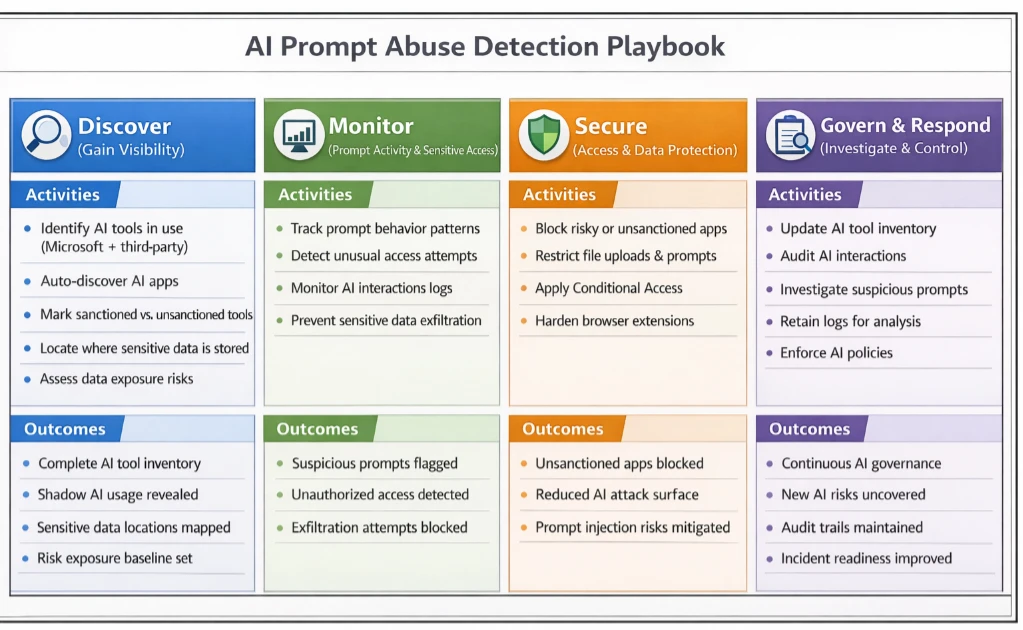
“Healthcare organizations don’t necessarily need to slow AI adoption, but security needs to evolve alongside it rather than follow it,” Biddle told ISMG. That starts with understanding where AI is being used, what sensitive information it can access and what actions AI agents are permitted to take.
“Our research found that 60% of organizations lack controls governing sensitive data used in AI systems. That’s a gap healthcare leaders need to prioritize as AI becomes more embedded in clinical and operational workflows.”
But healthcare organizations can’t neglect human risks that have long made the sector vulnerable, from phishing and compromised accounts to employee mistakes and data loss, she said. “As people and AI agents increasingly work alongside one another, the priority should be protecting those interactions while ensuring critical healthcare services remain available.”
Resiliency in the face of disruptive healthcare cyberattacks was also top of mind of many experts who spoke at the ISMG HealthSec cybersecurity summit in New York City last week.
“Moving from cyber defense to cyber resilience is important for anybody in any sector, but I would argue that it’s even more important for the healthcare sector,” said Guru Gurushankar, senior vice president and general manager of healthcare and life sciences at security firm Color Tokens.
“In healthcare, I cannot turn away patients during the downtime. I cannot turn away ambulances. I cannot reschedule elective surgeries and even emergent surgeries,” he said. Cyber resilience plays a critical role in delivering uninterrupted clinical care, he said. That requires certain key technical controls.
“Microsegmentation has to be core essential because that is the proactive way in which you prevent a simple breach incident from becoming a large-scale catastrophic incident,” he said.
Proofpoint’s Biddle said she expects the line between cybersecurity and healthcare resilience to become increasingly blurred.
“As clinical applications move to the cloud and AI becomes more embedded in everyday workflows, healthcare organizations will face growing pressure to secure not just their systems and data, but the processes that keep patient care moving,” she said.
The question will increasingly shift from whether an organization can prevent every attack to how effectively it can maintain and restore critical services when something goes wrong, she added.
“AI will add another dimension to that challenge. As agents take on more responsibility, healthcare organizations will need to move beyond governing who can access sensitive information to understanding what AI systems can do with it,” she said.
AI governance, data protection and third-party risk will ultimately become much more central to healthcare cybersecurity strategies moving forward, she predicted.