
How They Got Hacked Episode Fifty Six 56

Source link
Related Articles
All Mix →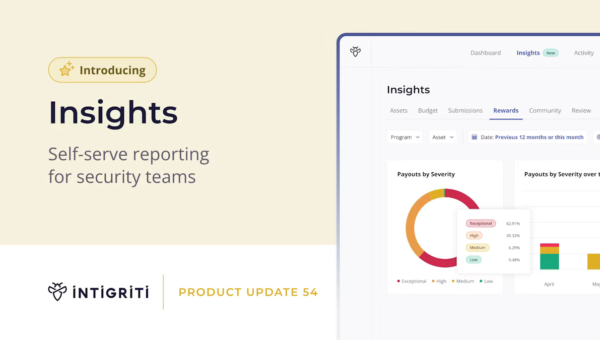
Insights self-serve reporting for security teams
Table of Contents 1) Prove ROI and control spend 2) Demonstrate security performance and risk trends 3) Improve operational efficiency for review and remediation 4)…
Guide to Responsible Disclosure and Bug Bounty
Table of Contents What does Responsible Disclosure mean? What is the difference between Responsible Disclosure and Bug Bounty? How do you set up an Responsible…

3 Bug Bounty Lessons From Retail & eCommerce Customers
Table of Contents 1. Diverse Skillsets and Creativity 2. Actionable Insights 3. Scale How do security vulnerabilities uniquely impact the retail and eCommerce space, and…
A complete guide to exploiting advanced CSRF vulnerabilities
Table of Contents Browser security measures When is it vulnerable to CSRF? 2) Content-Type based CSRF Cross-site request forgery—or for short CSRF—vulnerabilities are one of…
Security myths and misconceptions – Writing down passwords is bad
This is the first of a series of short posts to debunk security myths and misconceptions. In today’s blog i’m going to explain why writing…
More AI and Hacking Content · Joseph Thacker
Table of Contents Written Content Video Content Features If you read my posts on here, you enjoy the same things I do. So, I wanted…