
How They Got Hacked Episode Fifty Three 53

Source link
Related Articles
All Mix →
Lessons Learned from Over a Decade of On-Call
Table of Contents The What, When, Who, and Why Over-alerting Is Detrimental in More Ways Than One Importance of Looking Back All of Us Are…
My Gaming Idea | Daniel Miessler
Table of Contents Isn’t Everyone Doing That Already? More On The Model FPS Casual Why I’m not pursuing it Conclusion [ July 27, 2006 ]…
Addressing API Security with NIST SP 800-228 — API Security
Table of Contents The Context: APIs, Automation, and Attack Velocity What NIST SP 800-228 Brings to the Table API Specification and Inventory Management Schema Validation…
Happiness: Creation vs. Collection | Daniel Miessler
I have an observation that I’ve been mulling for the last few days: unhealthy people collect things. Healthy people create things. Naturally, statements like these…
Axel Springer National Media & Tech launches a public bug bounty program on Intigriti
Axel Springer has long been a pioneer in the digital publishing industry, with a vast portfolio of brands, such as Stepstone, Aviv, Idealo, BILD, Politico…
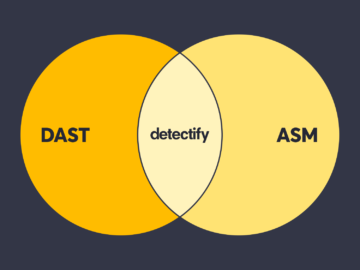
How we use DAST methodology in EASM
Table of Contents Differences between manual and automated security testing The history of DAST tools Surface Monitoring + Application Scanning = Best-in-class AST solution Surface…