OpenAI released a technical breakdown of the historic incident and plans changes to prevent such an occurrence from happening again.
OpenAI released a technical breakdown of the historic incident and plans changes to prevent such an occurrence from happening again.
Hackers could subvert frontier models with attacks that their developers overlook, Cisco said. Source link
Listen to the article 4 min This audio is auto-generated. Please let us know if you have feedback. Dive Brief: The vulnerability of the “connective…
Listen to the article 3 min This audio is auto-generated. Please let us know if you have feedback. The Trump administration’s campaign to purge the…
Threat actors are targeting a critical and high severity vulnerability in Roundcube Webmail, which is widely used in government and higher education, according to security…
The code injection flaw is similar to a prior vulnerability that was immediately flagged in January. Source link
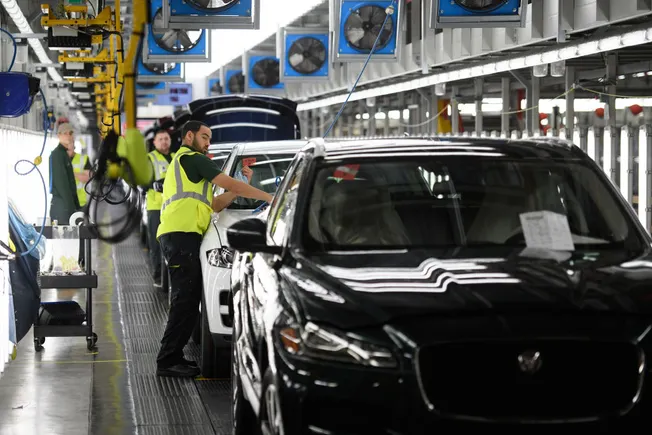
Jaguar Land Rover said Tuesday that it will extend a production pause until Sept. 24, as it continues investigating a recent cyberattack on its networks.…