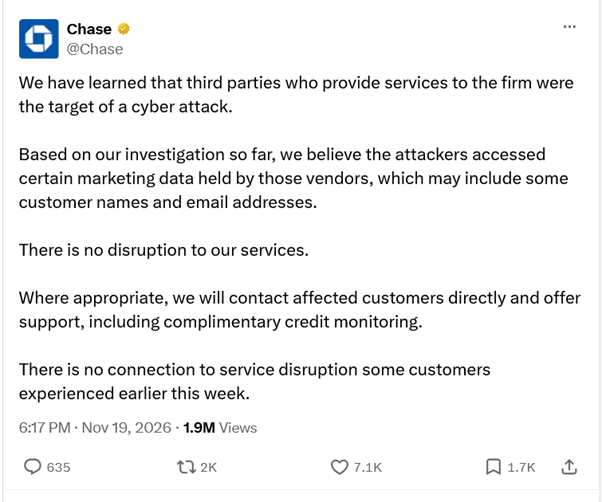
JPMorgan Chase, Visa and Mastercard acknowledged cyber incidents involving third-party service providers on Thursday, November 19, after the extortion group n0n posted files it claimed contained records linked to the three companies.
JPMorgan said it believes attackers accessed marketing data held by its vendors, which may include customer names and email addresses. Mastercard confirmed that a provider incident exposed email addresses belonging to a small subset of cardholders enrolled in a benefits program. It said the incident did not affect its payment network or card use.
Visa told Reuters that it linked the claims to an incident involving a service provider in the Asia-Pacific region. Visa said its own systems and payment data were unaffected. It did not confirm that customer records were exposed.
What the files contained
Reuters reported that n0n posted claims and files relating to Visa and Mastercard on November 16. Hackread.com reviewed the files posted by the group and counted 16,541 unique email addresses in the material attributed to JPMorgan Chase, 7,815 in the files attributed to Visa and 3,210 in those attributed to Mastercard. These figures count distinct email addresses within each dataset. They do not establish how many customers were affected.
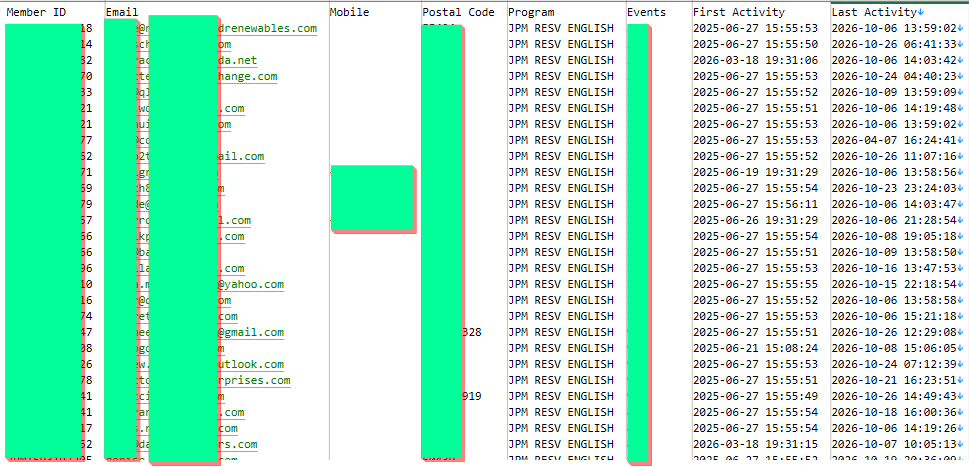
Hackread.com’s review also found entries for Hong Kong, Taiwan, South Korea, Japan, the Philippines, Singapore, Malaysia, Australia and Macau in the files attributed to Visa. The files attributed to Mastercard included marketing records for markets in North America, the Middle East and Africa.
None of the three companies named the providers involved, and it remains unclear whether the incidents involved a common vendor. Mastercard said it had contained the exposure and was working with the provider to assist affected cardholders. JPMorgan said it would contact affected customers where appropriate and offer free credit monitoring.
The n0n group has been active since September 2026. The Wall Street Journal, citing cybersecurity firm Recorded Future, reported that the group steals corporate data for extortion and recruits other hackers to gain access to company networks.
Chase says its banking outage was unrelated
JPMorgan said the vendor incident was unrelated to the November 16 Chase outage, which it attributed to a software bug affecting its internal hardware systems.
Email addresses, phone numbers and details about a customer’s relationship with a bank or card provider can make fake fraud alerts or benefits messages more convincing. If a message asks you to verify your account or claim a benefit, open your bank’s app directly or call the number on the back of your card. A message that mentions a program you actually use can still be a scam.