A Python-based information stealer that targets data from 17 Chromium-based browsers, alongside Firefox, to harvest saved credentials, payment-card details, browsing history and active session cookies.
The malware is delivered through a builder framework that enables operators to generate customized Windows payloads and configure their own data-exfiltration webhook.
The archive included a “TokenGrabber Builder” folder containing a Python builder and an embedded stealer payload.
The structure points to a malware-as-a-service (MaaS) model, allowing multiple affiliates or low-skilled operators to build and deploy individualized samples.
The builder can compile the embedded Python payload into Windows executables using Nuitka or PyInstaller, or save it as a raw Python script.
Nuitka is especially notable because it converts Python code into native binaries, reducing the presence of recoverable Python bytecode and complicating analysis with common Python decompilers.
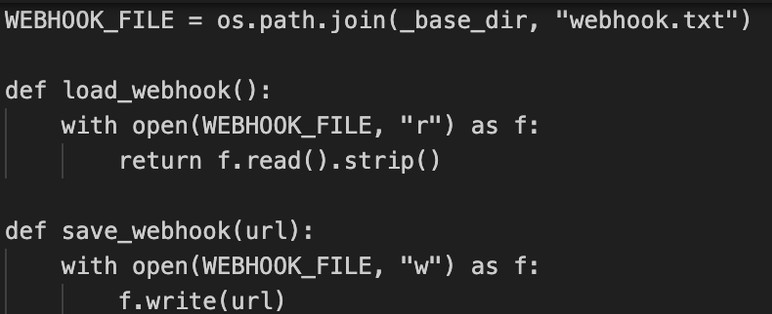
Before compilation, the operator supplies a Discord or Telegram webhook address. The builder XOR-encrypts the address with key 0x5A, Base64-encodes it and injects it into the payload.
This approach prevents the webhook from appearing in plaintext and causes separately built samples to carry different encoded configuration values and potentially distinct hashes, weakening simple indicator-based clustering.
The builder also automatically installs dependencies when needed and searches for locally installed Python interpreters through environment paths, common installation directories and Windows Registry locations.
Unexpected pip.exe execution from non-development applications could therefore provide defenders with an early behavioral detection signal.
K7 Labs identified the Python campaign, after examining a suspicious RAR archive, “my new program called 2.rar,” which contained a nested archive named TokenGrabberBuilder.zip.
Python Infostealer Campaign
The embedded stealer checks known browser-profile paths in %LOCALAPPDATA% and %APPDATA% to target 17 Chromium-based browsers.
It collects credentials from Login Data, history from History, payment-card records from Web Data, and session material from Cookies or Network/Cookies.
To access Chromium-protected data, the malware retrieves the browser’s encrypted master key from the Local State file and attempts to decrypt it using Windows DPAPI.
It copies locked SQLite databases to a temporary location before reading them, then decrypts newer Chrome-format entries protected with AES-256-GCM or falls back to older DPAPI-based methods.
Firefox is also in scope. The stealer searches Firefox profile directories for places.sqlite and cookies.sqlite, enabling collection of browsing history and session cookies.
Session theft is particularly damaging because a valid cookie can let an attacker hijack an authenticated web session without knowing the victim’s password.
Beyond browser data, the malware enumerates saved Wi-Fi profiles through netsh wlan show profiles and attempts to extract cleartext Wi-Fi keys.
It scans Discord LevelDB storage for tokens, validates potential tokens against Discord’s API, and seeks .ROBLOSECURITY cookies that could expose Roblox accounts.
The malware establishes persistence through two methods: a Registry Run key at HKCUSoftwareMicrosoftWindowsCurrentVersionRun, using the misleading value name WindowsUpdate, and an ONLOGON scheduled task.
It further attempts to evade analysis by checking for attached debuggers, virtual-machine processes, low-capacity disks and sandbox time limits.
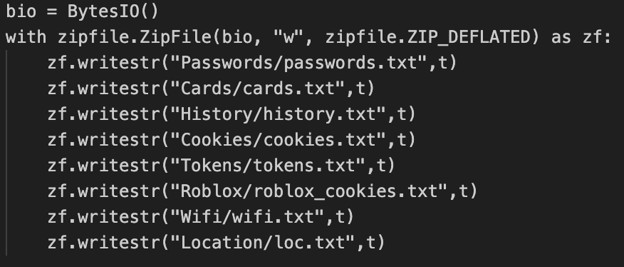
Collected information, including public IP address, location details, username and computer name, is assembled in memory as StolenData_.
The archive is then transmitted via HTTP POST to the attacker-controlled webhook, limiting artifacts that might otherwise be visible through disk-based monitoring.
Organizations should prioritize behavior-based detection rather than relying only on static file signatures.
Useful hunting signals include suspicious child execution of pip.exe, browser database access by untrusted processes, netsh commands requesting Wi-Fi profiles, creation of Run-key persistence or login-triggered scheduled tasks, and outbound POST requests to unfamiliar webhook infrastructure.
The campaign also underscores the risk posed by archive-delivered malware.
Users should avoid executing files extracted from unsolicited or unverified archives, while defenders should enforce multifactor authentication, monitor anomalous session activity and rapidly revoke browser sessions or reset credentials following a suspected compromise.
Indicators of Compromise
| Hash | Detection Name |
| 610f0c65a3f8e88559f89ed90ea9ee5c | Password-Stealer ( 006dba241 ) |
| 429ed63ab3fbda8d22d0ac750ecfe8cc | Password-Stealer ( 006dba241 ) |
| 9ffe0e45c7a3f20e4481206c1c3b0854 | Trojan ( 006e632e1 ) |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Cut every SOC alert investigation by 21 min. Power your SOC with instant IOC context for immediate response: Integrate TI Lookup in your SOC