A newly identified information-stealing campaign, tracked as Rapuncel, is exploiting a Microsoft-attested kernel driver to terminate up to 145 antivirus (AV) and endpoint detection and response (EDR) processes. This allows attackers to steal browser credentials, cryptocurrency wallet data, chat tokens, and Windows credentials.
Researchers from the LastPass Threat Intelligence, Mitigation, and Escalation team, in collaboration with Delphos Labs, uncovered this operation while investigating a fraudulent GitHub organization impersonating LastPass Authenticator.
The campaign used SEO-optimized GitHub repositories and GitHub Pages sites to redirect victims through a multi-stage delivery chain before delivering malware-laden ZIP archives.
New Rapuncel Infostealer
The operation impersonated at least 40 companies, utilizing a reusable malware-as-a-service distribution kit hosted in part on GitHub infrastructure. Victims searching for software downloads could encounter convincing fake repositories that included stolen branding, product descriptions, and download buttons.
In the LastPass-themed lure, a “GET – LASTPASS AUTHENTICATOR” button redirected users to a GitHub Pages portal that displayed counterfeit trust indicators, such as “VirusTotal Approved” and “Secure Archive” badges.
Hidden GitHub Pages redirects and a Cloudflare-fronted traffic management domain then directed victims to attacker-controlled payload servers.
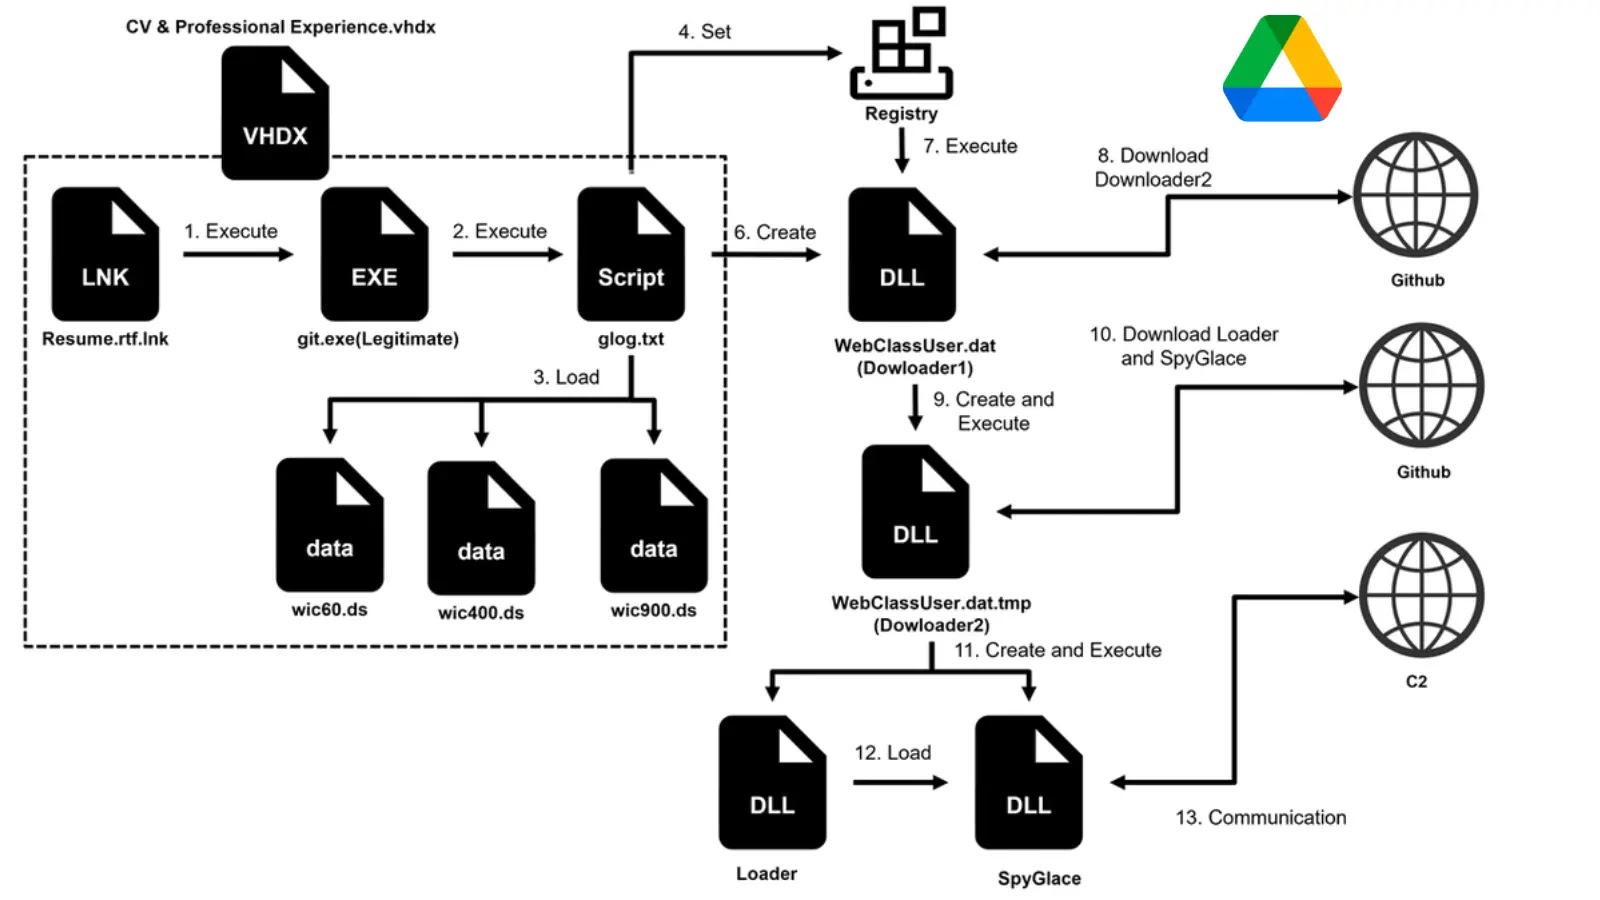
The download archives were unusually large, ranging from 127 MB to 148 MB in the cases observed, as they included junk DLL files designed to exceed automated sandbox and scanning size limits. Inside the archives was a fake installer based on Microsoft’s legitimate vsdbg.exe debugging utility, renamed to appear harmless.
When executed, the renamed binary side-loads a malicious vsdbg.dll file. The loader attempts multiple privilege escalation methods and ultimately seeks SYSTEM-level execution before deploying the Alinubx.sys kernel driver.
The driver is dropped as nvfsflt64.sys and registered under the service name NvFsFilter, masquerading as an NVIDIA File System Filter Driver. It exposes an IOCTL interface through \.Alinubx and accepts process IDs from the loader.
The driver then opens targeted processes with kernel-mode access and terminates them using ZwTerminateProcess. This technique bypasses normal user-mode access checks and can defeat Protected Process Light protections utilized by security products. Researchers found that the loader contains 145 hardcoded AV and EDR process names.
Alinubx.sys is signed through the Microsoft Windows Hardware Compatibility Publisher chain, with a signing timestamp dating back to March 2023. Although it can disable security software, the driver was not listed on Microsoft’s vulnerable-driver blocklist at the time of analysis.
The driver appears to be a renamed version of CcProtect.sys, which is associated with the CnCrypt/CcProtect product line from Henan Dafeng Software.
Its known ability to terminate processes has been publicly documented, but changing the driver’s filename and identity seems to have helped operators evade signature-based detection.
Once endpoint protections are disabled, Rapuncel can steal data from over 25 browsers, more than 30 cryptocurrency wallets, Discord, Steam, Telegram, and Windows Credential Manager.
It also searches for files containing terms such as “password,” “seed,” “wallet,” and “recovery,” captures screenshots, and exfiltrates the collected data to 2.26.126[.]50.
Defenders should block the identified driver hash, search for the NvFsFilter service and nvfsflt64.sys, restrict the installation of unsigned or unapproved drivers, and monitor for suspicious DLL side-loading involving vsdbg.exe.
Organizations should also inform users that GitHub is not an official download channel for LastPass Authenticator or many other commonly impersonated products.
Cut every SOC alert investigation by 21 min. Power your SOC with instant IOC context for immediate response: Integrate TI Lookup in your SOC