AvisLoader, a newly observed Windows malware loader designed to maintain operator access even when conventional command-and-control infrastructure is disrupted.
Instead of relying on a fixed domain, IP address, or centralized server, the malware uses the encrypted Tox peer-to-peer messaging network to receive commands and deliver follow-on payloads.
The discovery highlights a growing challenge for defenders: takedowns that block or seize malicious domains may have limited effect when malware operators can retain the same peer identity and migrate their controller to new infrastructure.
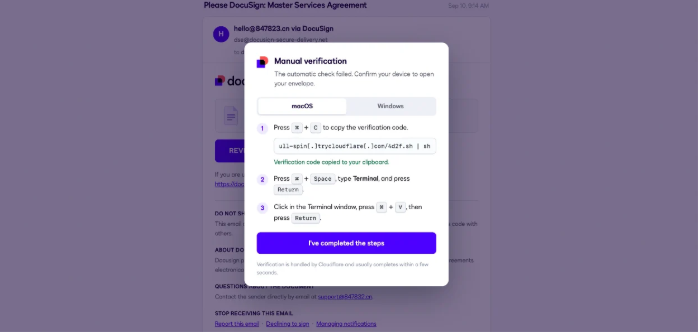
The infection chain begins with a fake document-signing request styled as a DocuSign page.
Rather than downloading a document, the page prompts the target to copy and execute an attacker-supplied command.
This is a hallmark of ClickFix activity: social engineering that turns the victim into the execution mechanism.
The copied command retrieves and runs code through a Cloudflare Quick Tunnel address hosted under trycloudflare.com.
While Cloudflare services are legitimate, their use in this campaign helps obscure the payload-delivery infrastructure and shifts execution outside the browser’s conventional download flow.
The exposed lure contained a macOS-oriented command, but researchers recovered a 64-bit Windows loader and did not identify a matching macOS payload.
The 3.4 MB AvisLoader executable statically links c-toxcore, the reference implementation of the Tox protocol.
It also retains a developer build path C:UsersdevDesktopc-toxcore providing a direct indicator of its underlying communications framework.
Unlike centralized C2 operations, where responders can block a domain or neutralize a server, Tox allows the malware to communicate as a peer in an encrypted P2P network.
A cybercrime-forum advertisement reportedly claims operators can move the controller simply by transferring its Tox save file, allowing infected systems to follow the same identity without a new domain.
That architecture does not make AvisLoader invisible. Its peer connections, correlated with suspicious host activity, remain a viable detection point.
However, it raises the operational cost of infrastructure disruption and reduces the value of domain-only blocking.
Varonis Threat Labs recently discovered AvisLoader, was found on an exposed staging server together with a ClickFix lure, supporting utilities, and an operator-facing command center.
P2P Command Network
AvisLoader appears built for persistence, privilege escalation, and concealment. Researchers found code targeting desktop and taskbar-pinned shortcuts, along with backup-related strings and a VBScript launcher named VLCAssistant.
Victims are presented with a bogus “Manual verification” dialog claiming that Cloudflare is handling the verification process.
This suggests shortcut hijacking: malware can execute when a user opens a modified shortcut, then launch the intended application to minimize suspicion.
A helper executable, auto.exe, references method 41 from UACME, a public UAC-bypass project.
Its strings reference the ICMLuaUtil interface and a COM-elevation technique, although the recovered artifact alone does not prove that privilege escalation succeeds on a given Windows build.
Another component, hmn_hook.dll, hooks NtQuerySystemInformation and can filter a chosen process name from returned process listings.
Such functionality could conceal a process from software relying on that API, though Varonis did not establish that the DLL was injected into Task Manager or used to hide AvisLoader specifically.
The recovered AvisLoader Command Center provides operators with a dashboard for managing endpoints, staging files, and assigning tasks.
Its client table records hostnames, location, CPU and GPU details, antivirus products, administrator status, and public keys metadata consistent with Tox’s peer-identity model.
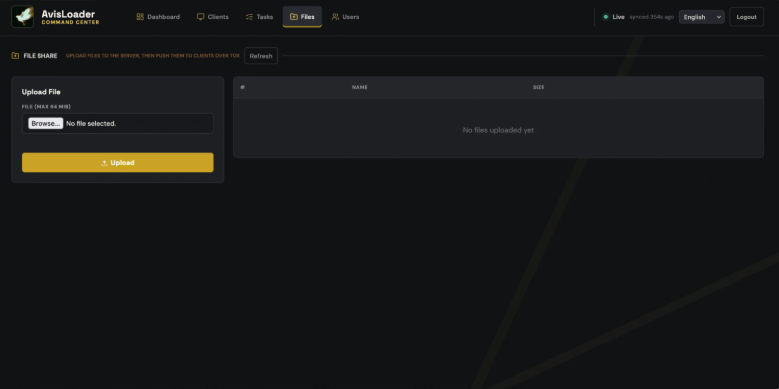
Operators can queue shell commands for systems matching hardware, geography, or privilege criteria, including tasks that execute when a matching endpoint next comes online.
The panel also supports transferring additional payloads to compromised devices over Tox, turning AvisLoader into a flexible initial-access and post-compromise delivery framework.
Security teams should investigate document-verification pages that instruct users to paste commands into Windows Run, Command Prompt, PowerShell, or Terminal.
Monitoring should focus on suspicious command-shell activity following browser sessions, unexpected remote-code retrieval, modified desktop or taskbar shortcuts, .backup artifacts, and references to VLCAssistant, auto.exe, or hmn_hook.dll.
Defenders should also examine anomalous Tox or peer-to-peer traffic from endpoints that show suspicious script execution or shortcut changes.
As ClickFix campaigns increasingly bypass exploit-based defenses through user-assisted execution, behavioral telemetry and user awareness become as important as traditional malware blocking.
IOCs
| Filename | SHA-256 | Role |
| 78324.exe | 35dd164a7f5d8b42b9870c7009f7425b1c8cb771280c9e6c525e09f3dd13c2cc | AvisLoader Windows client |
| auto.exe | f0a6870cb774a55775eda15fd39e8a17eb3169d5b9365186dae8edff07ff3975 | Bundled elevation-bypass helper |
| hmn_hook.dll | cd1e835f52e5f55279dcdf3857e11bc9298ea6caa88eb214ea2d40ff5d38b5f5 | Bundled process-hiding library |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Cut every SOC alert investigation by 21 min. Power your SOC with instant IOC context for immediate response: Integrate TI Lookup in your SOC