North Korea-linked threat actor Konni has launched a targeted cyberespionage operation against Ukraine-focused entities using malicious Windows shortcut files disguised as PDF documents.
The campaign, tracked by SOCRadar Threat Research Unit as Operation Conflict Compass, deploys a modular PowerShell malware family dubbed VelvetCake to collect intelligence on the Russia-Ukraine war.
The activity appears designed to provide the Democratic People’s Republic of Korea (DPRK) with insight into the conflict’s likely trajectory, including diplomatic developments, operational risks, and the medium-term outlook of Russia’s invasion.
The initial-access chain likely begins with spear-phishing emails that deliver ZIP archives containing LNK shortcut files masquerading as legitimate PDF documents.
The social-engineering themes are deliberately tailored to audiences following Ukraine-related policy, humanitarian, and geopolitical issues.
Observed decoys reference Russia-Ukraine peace-negotiation frameworks, a Ukrainian social researcher’s résumé, and global food-price disruption linked to the Strait of Hormuz crisis and Russian grain exports.
These lures indicate likely targeting of diplomatic missions, foreign-policy think tanks, NGOs, defense researchers, and other organizations able to provide insight into the war’s political and strategic direction.
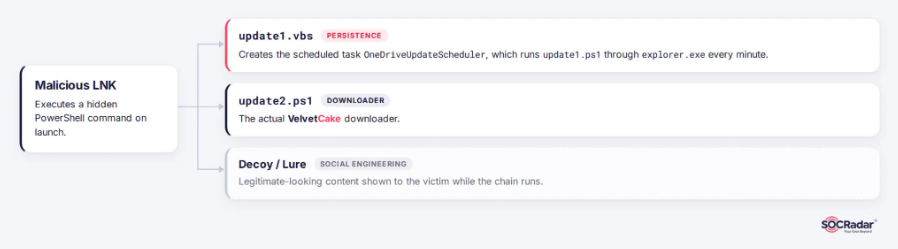
When a victim opens the shortcut, it launches a PowerShell command that retrieves two payloads from an attacker-controlled GitHub repository and stores them in the user’s AppData directory.
One file is a VBScript persistence component, while the other is the VelvetCake PowerShell downloader.
The use of GitHub gives the campaign a familiar and often trusted delivery channel while allowing operators to update staging content rapidly.
The VBScript establishes persistence by creating a scheduled task named OneDriveUpdateScheduler.
The task invokes explorer.exe to execute the PowerShell component every minute, disguising malicious execution as a benign Microsoft OneDrive-related update process.
VelvetCake differs from a traditional feature-rich backdoor because it contains little fixed functionality on the compromised endpoint.
SOCRadar Researchers assess the campaign, as linked to Konni with moderate confidence, citing its targeting patterns, infrastructure choices, execution tradecraft, code characteristics, and operator activity aligned with Korea/Japan Standard Time.
VelvetCake PowerShell Malware
Instead, it acts as a lightweight task runner that retrieves PowerShell modules from its command-and-control infrastructure, runs them, returns collected data, removes local artifacts, and exits.
The scheduled task repeatedly launches the downloader, giving operators a near-real-time mechanism to issue new tasks without redeploying the primary payload.
Researchers observed VelvetCake connecting to a remote server over raw TCP on port 12345.
The malware requests available task files, downloads configuration files and PowerShell scripts, executes the scripts, monitors for newly generated output, uploads the results, and deletes temporary artifacts.
The malware uses a hard-coded plaintext password, MySecurePass123, and a custom upload framing value of 0x12345678, indicators that may assist defenders with threat hunting.
A recovered second-stage script performed broad host reconnaissance, including antivirus discovery through the rootSecurityCenter2 WMI namespace, collection of system and network information, active-process enumeration, drive mapping, and harvesting of recently accessed files.
It also captured screenshots of the victim’s virtual display and staged text and PNG output in the temporary directory before exfiltrating it through HTTP POST requests.
The actors also used trojanized Zoom installers containing legitimate Zoom installation files alongside the same VBScript and PowerShell payloads.
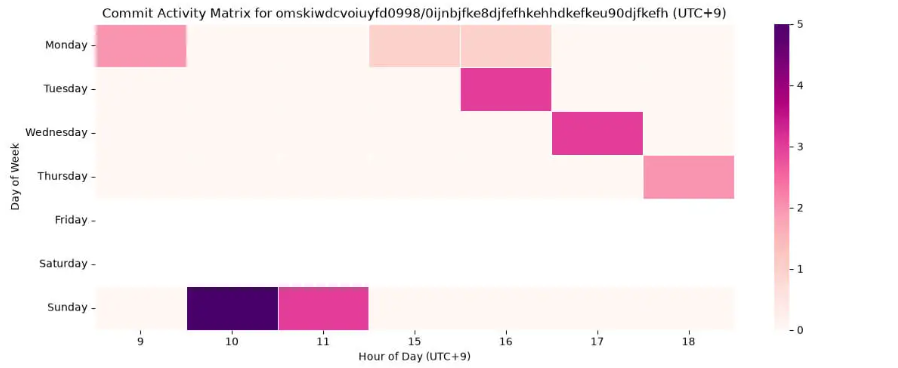
An analysis of commit timestamps from the operator’s GitHub staging repository reveals that most commits were pushed with a +0900 time zone offset (Korea/Japan Standard Time).
In another variant, PowerShell used Net.WebClient.DownloadString with Invoke-Expression to execute malicious content directly in memory, reducing on-disk artifacts and complicating conventional file-based detection.
Konni, also tracked as TA406 and Opal Sleet, is a DPRK-nexus espionage group associated with the wider Kimsuky umbrella.
It has a history of targeting foreign-policy, defense, diplomatic, and government-linked organizations through highly tailored phishing operations, malicious shortcut files, scheduled-task persistence, and custom PowerShell loaders.
Operation Conflict Compass reinforces a broader operational pattern: DPRK operators are combining geopolitical intelligence requirements with low-cost, adaptable malware delivery.
For defenders, high-priority detection opportunities include ZIP-contained LNK files, scheduled tasks impersonating OneDrive updates, unexpected PowerShell activity initiated through explorer.exe.
GitHub raw-content downloads, and outbound connections associated with the campaign’s TCP and web-based C2 infrastructure.
IOCs
| Indicator | Description | |
|---|---|---|
| URL | hxxps[://]github[.]com/omskiwdcvoiuyfd0998/ | Threat Actor’s GitHub Account |
| URL | hxxps[://]github[.]com/omskiwdcvoiuyfd0998/media | Threat Actor’s GitHub Repo of Peace Lure |
| URL | hxxps[://]github[.]com/omskiwdcvoiuyfd0998/medianews | Threat Actor’s GitHub Repo of Sociologist CV Lure |
| URL | hxxps[://]github[.]com/omskiwdcvoiuyfd0998/zoominstaller | Threat Actor’s GitHub Repo of VelvetCake Malicious Zoom Installer |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Cut every SOC alert investigation by 21 min. Power your SOC with instant IOC context for immediate response: Integrate TI Lookup in your SOC