Healthcare regs should include continuous AI monitoring
The National Commission into the Regulation of AI in Healthcare has published a report covering a set of recommendations for artificial intelligence (AI-)enabled healthcare. The…
The National Commission into the Regulation of AI in Healthcare has published a report covering a set of recommendations for artificial intelligence (AI-)enabled healthcare. The…
Key points A critical vulnerability tracked as CVE-2026-75650, rated 10.0 on the CVSS scale, allows unauthenticated remote code execution on Adobe Commerce and Magento Open…
Adversaries, both criminal and state-sponsored, are increasingly using AI to automate and scale their attacks, according to Google’s Threat Intelligence Group (GTIG). What started as…
Chaotic Eclipse Released ShieldCrash, A PoC For Microsoft Defender Zero-Day Pierluigi Paganini September 09, 2026 The researcher Chaotic Eclipse released ShieldCrash, a PoC exploit for a Microsoft…
The document also focuses on helping victims, reflecting the bureau’s attempt to encourage more companies to share information with it. Source link
Proofpoint researchers have spotted at least four state-aligned threat groups chain a trio of zero-day vulnerabilities to conduct espionage on various targets of interest to…
The Trump administration sanctioned Chinese-language marketplace Xinbi Guarantee on Wednesday, along with two affiliated organisations, as part of a wider crackdown on transnational cybercrime. The…
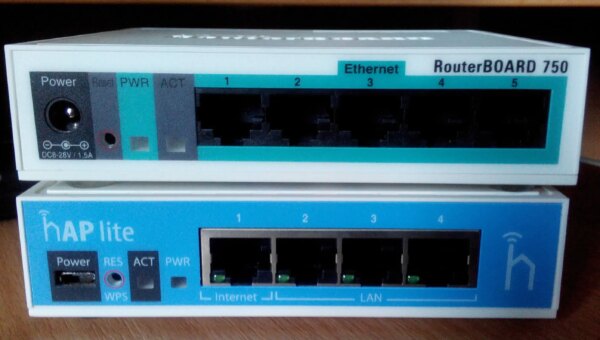
MikroTik released patches in RouterOS 7.25 beta 3, 7.24.2, 7.23.4, and 6.49.21 and advises against enabling the SSH service on the internet interface. Despite this…
A nearly identical exploit kit that targets critical vulnerabilities in both Chromium-based browsers and older versions of Windows is being actively used by at least…
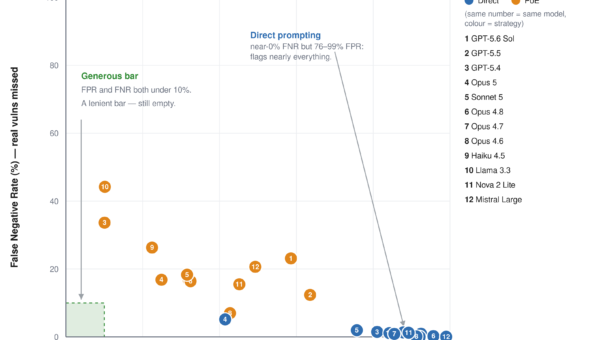
Security teams are starting to actively use AI for security work, including vulnerability triage, penetration testing, threat modeling, incident response, and code review. The promise…
Cisco Talos is actively tracking the exploitation of two vulnerabilities in Cisco’s Secure Firewall Management Center (FMC) Software. First, CVE-2026-20079 is an authentication bypass vulnerability…
Open-source registries for AI agents are only effective when they include a rigorous, transparent security review process for community submissions. That’s why for its new…