Elastic’s 2022 Global Threat Report: A roadmap for navigating today’s growing threatscape
Staying up-to-date on the current state of security and understanding the implications of today’s growing threat landscape is critical to my role as CISO at…
Staying up-to-date on the current state of security and understanding the implications of today’s growing threat landscape is critical to my role as CISO at…
A phishing-as-a-service framework called BigBear 2.0 has been used to bypass multi-factor authentication at 258 organizations and steal more than 5,000 Microsoft 365 credentials. Researchers…
A stealthy Linux rootkit is giving attackers a new way to keep control of compromised F5 BIG-IP Access Policy Manager servers. Instead of leaving an…
ConnectWise has announced a security issue affecting file transfer functionality in ScreenConnect Remote Access Support and Access sessions. This issue affects both cloud-hosted and on-premises…
N-able released an emergency hotfix for CVE-2026-86218, a remote code execution (RCE) flaw affecting N-central, its remote monitoring and management (RMM) solution popular with managed…
This week on the Lock and Code podcast… Crooks are taking a holiday. They’re counting on you to fund it. For decades, cybercriminals have stolen…
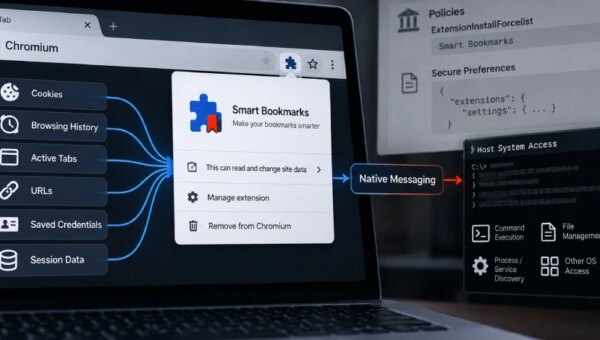
Cybersecurity researchers have disclosed details of a complex Chromium-based post-exploitation toolkit called PEEP that masquerades as a bookmarks extension for the web browser. “Requiring prior…
Earlier this year, the UK Government launched its Cyber Resilience Pledge initiative, aimed at encouraging more companies to invest in cyber security. This initiative aims…
Some of the world’s leading democracies are pushing governments and companies to start preparing for post-quantum cryptography before quantum computers become powerful enough to break…
NSW Police are set to receive an extra $15 million to spend on technology to access “encrypted devices and digital platforms”, for the purpose of…
North Korea-aligned threat actors have been using a new Linux toolkit in attacks targeting automotive and media organizations in South Korea, Rapid7 reports. Designed for…
StyleSmuggler: The Magento Zero-Day Behind New Store Attacks Pierluigi Paganini September 07, 2026 StyleSmuggler Magento zero-day is under active attack, letting unauthenticated attackers execute code…