KB5060533 update triggers boot errors on Surface Hub v1 devices
Microsoft is investigating a known issue that triggers Secure Boot errors and prevents Surface Hub v1 devices from starting up. These boot problems only impact…
Microsoft is investigating a known issue that triggers Secure Boot errors and prevents Surface Hub v1 devices from starting up. These boot problems only impact…
Despite sustained international pressure, sanctions, and public exposures over the past two years, the sophisticated Predator mobile spyware has demonstrated remarkable resilience, continuing to evolve…
The National Institute of Standards and Technology (NIST) has released groundbreaking guidance to help organizations implement Zero Trust Architectures (ZTAs) using commercially available technologies. Implementing…
The Black Hat USA 2025 two-day main conference on Aug. 6 and 7 will feature more than 100 selected Briefings. Some of the catchy Briefings are: No Hoodies…
Microsoft is investigating an ongoing incident that is causing users to experience errors with some Microsoft 365 authentication features. As the company revealed earlier today in…
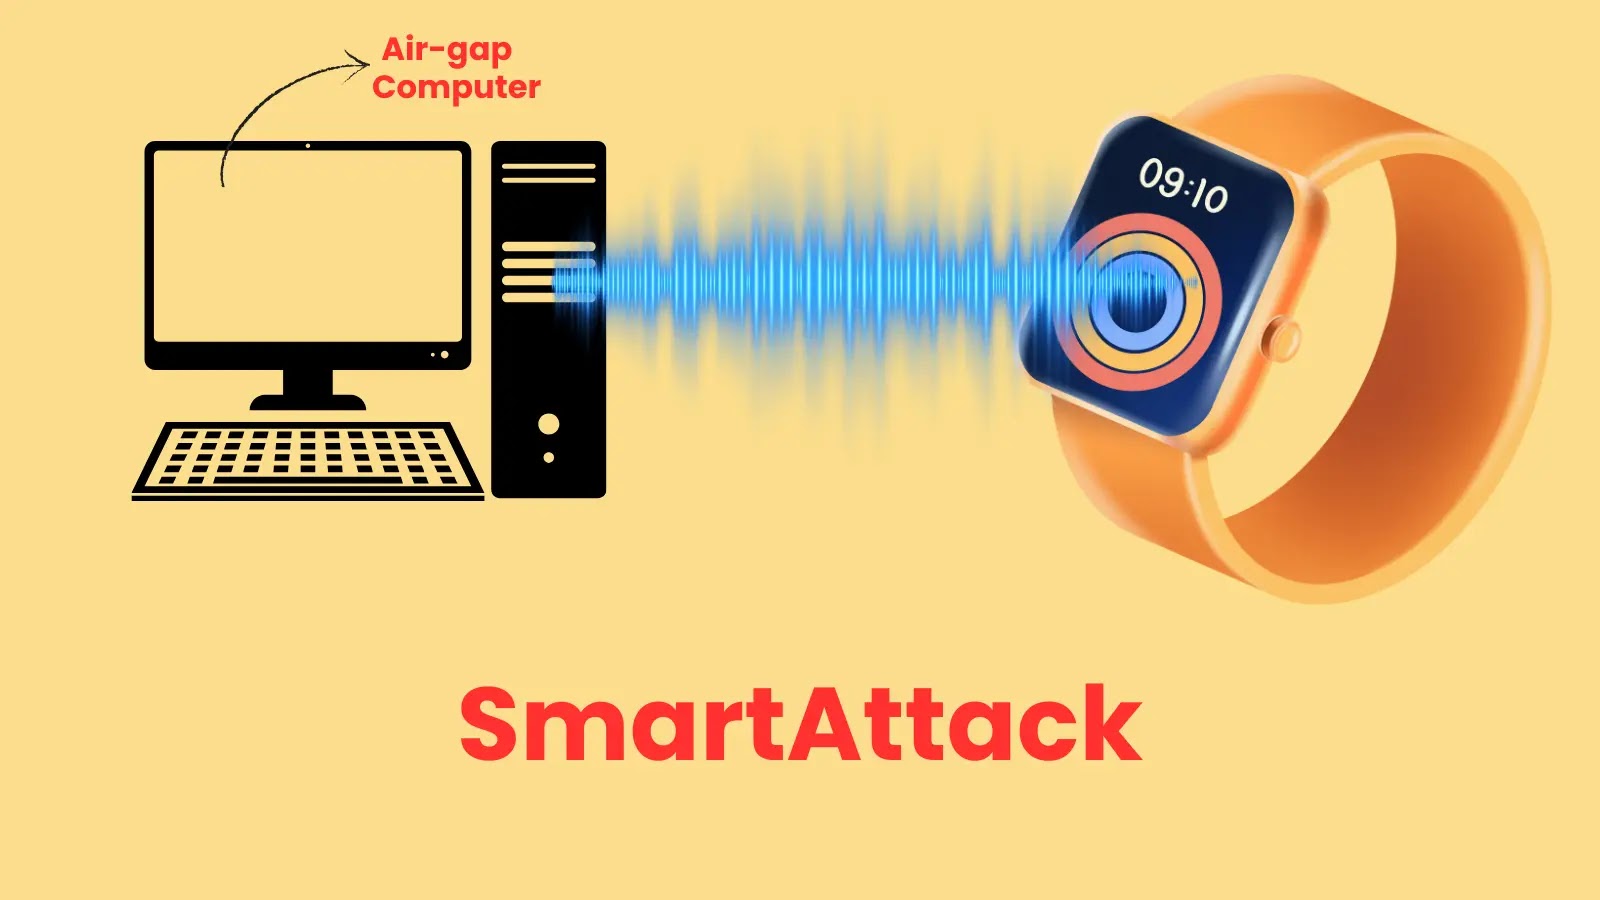
A sophisticated new attack method called “SmartAttack” that can breach supposedly secure air-gapped computer systems using smartwatches as covert data receivers. The groundbreaking research demonstrates…
A critical vulnerability (CVE-2025-6031) has been identified in Amazon Cloud Cam devices, which reached end-of-life (EOL) status in December 2022. The flaw allows attackers to…
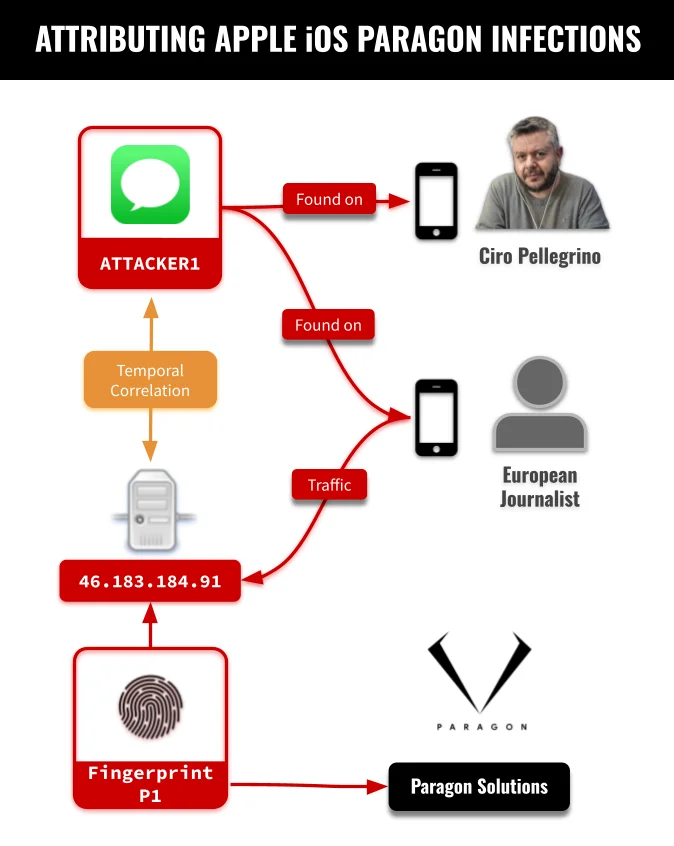
A zero-click attack leveraging a freshly disclosed Messages vulnerability (CVE-2025-43200) has infected the iPhones of two European journalists with Paragon’s Graphite mercenary spyware, Citizen Lab…
Introduction: Security at a Tipping Point Security Operations Centers (SOCs) were built for a different era, one defined by perimeter-based thinking, known threats, and manageable…
Victoria’s Secret has restored all critical systems impacted by a May 24 security incident that forced it to shut down corporate systems and the e-commerce…
Cybersecurity researchers have identified a sophisticated new phishing campaign that exploits GitHub’s OAuth2 device authorization flow to compromise developer accounts and steal authentication tokens. This…
A newly disclosed spoofing vulnerability (CVE-2025-26685) in Microsoft Defender for Identity (MDI) enables unauthenticated attackers to capture Net-NTLM hashes of critical Directory Service Accounts (DSAs),…