APTs Exploiting WinRAR 0day Flaw Despite Patch Availability
According to Google’s Threat Analysis Group (TAG), the group exploiting the vulnerability comprises Sandworm, Fancy Bear, and APT40, all associated with the Russian government and…
According to Google’s Threat Analysis Group (TAG), the group exploiting the vulnerability comprises Sandworm, Fancy Bear, and APT40, all associated with the Russian government and…
France-headquartered energy giant EDF has been singled out by the UK’s Office for Nuclear Regulation (ONR) and placed under significantly enhanced regulatory attention for cyber…
Three days after Cisco disclosed details of a dangerous zero-day in its IOS XE software, known compromises appear to be rising at a rapid rate,…
A British startup called Harmonic Security has attracted $7 million in seed-stage investment to build technology to help secure generative AI deployments in the enterprise.…
In the double extortion strategy, cybercriminals first exfiltrate sensitive data from the victim’s servers and then encrypt the data, making it inaccessible. They then demand…
Operational resilience is the discipline that is taking organisations beyond an internally-focused business continuity or information technology disaster recovery (ITDR) programme to look at the…
I hope you’ve been doing well! 🤖 AI Meetups Erry’ Day Living in the Bay Area, there appears to be an ever-increasing number of AI-related…
Thousands of information technology workers contracting with U.S. companies have for years secretly sent millions of dollars of their wages to North Korea for use…
The Ragnar Locker ransomware operation’s Tor negotiation and data leak sites were seized Thursday morning as part of an international law enforcement operation. BleepingComputer has…
Recently, researchers have found an increasing number of malware samples that employ code from non-executable files (such as .txt, .log, etc.), a strategy created particularly…
A threat actor allegedly published 4.1 million genetic data profiles stolen from the DNA testing company 23andMe in dark web forums. The British Royal Family,…
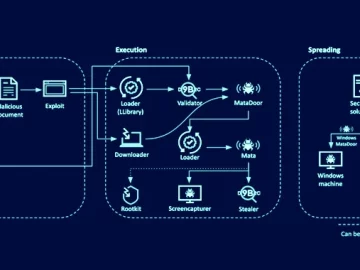
An updated version of a sophisticated backdoor framework called MATA has been used in attacks aimed at over a dozen Eastern European companies in the…