FBI confirms Barracuda patch is not effective for exploited ESG appliances
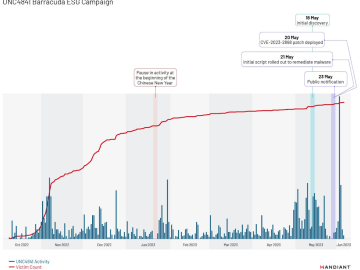
The FBI repeats the warning by Barracuda that all ESG appliances should immediately be replaced because the patch was ineffective. In an FBI Flash about a…
The FBI repeats the warning by Barracuda that all ESG appliances should immediately be replaced because the patch was ineffective. In an FBI Flash about a…
Modern attackers use a variety of tools and techniques to overcome defences to steal data, execute ransomware attacks and cause damage and disruption to their…
There is now a warning for Microsoft Edge about information technology safety. You’ll discover information on this page about which products are vulnerable, which vulnerabilities…
Google made its artificial intelligence-powered tools available to enterprise customers at a monthly price of US$30 ($46.30) per user, as the Alphabet-owned firm looks to…
US authorities said an international law enforcement operation had taken down the notorious “Qakbot” malware platform used extensively by cybercriminals in a variety of financial…
Image: Midjourney A new version of the DreamBus botnet malware exploits a critical-severity remote code execution vulnerability in RocketMQ servers to infect devices. The exploited…
Westpac has built and embedded a data management operating system called DM-OS throughout its groupwide operations. DM-OS was initially created to meet an enforceable undertaking…
UNC4841 threat actors hacked US government email servers exploiting Barracuda ESG flaw Pierluigi Paganini August 29, 2023 China-linked threat actors breached government organizations worldwide with…
The FBI announced today the disruption of the Qakbot botnet in an international law enforcement operation that not only seized infrastructure but also uninstalled the…
Law enforcement authorities on Tuesday announced the cross-border dismantling of the notorious Qakbot cybercrime operation that hit more than 700,000 computers globally with ransomware and…
The U.S. government today announced a coordinated crackdown against QakBot, a complex malware family used by multiple cybercrime groups to lay the groundwork for ransomware…
KEY FINDINGS Microsoft has identified a Chinese government-backed APT group called Flax Typhoon. The group has been targeting Taiwanese organizations since mid-2021. Flax Typhoon does…