The time to implement an internal AI usage policy is now
The use of artificial intelligence (AI) in organisations is increasingly widespread, thanks to its ability to increase efficiency, reduce the time that needs to be…
The use of artificial intelligence (AI) in organisations is increasingly widespread, thanks to its ability to increase efficiency, reduce the time that needs to be…
The LockBit ransomware group claims to have hacked Taiwan Semiconductor Manufacturing Company (TSMC), but the chip giant says only one of its suppliers was breached.…
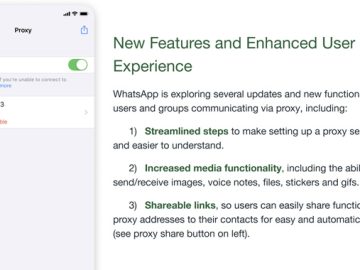
Jun 30, 2023Ravie LakshmananPrivacy / Tech Meta’s WhatsApp has rolled out updates to its proxy feature, allowing more flexibility in the kind of content that…
The internationally operating dating and friendship website, OkCupid was claimed to be attacked by the cybercriminal group, Türk Hack Team. Cybersecurity researchers tweeted about the…
Internet privacy company Proton this week announced the global launch of its open source password manager, Proton Pass. The password manager is now available as…
Cloud service providers fundamentally changed the way we do business in 2023. Office 365 is one of the most popular cloud-based services catering to online…
The United States Department of Commerce (DOC) has allegedly become the target of a cyber attack. Falcon Feed, a threat intelligence service, took to Twitter…
The top 25 most dangerous software weaknesses impacting software for the previous two calendar years have been published by MITRE as part of the 2023…
A ransomware attack on University of Manchester (UoM) has led to the data breach of over a million patients related to NHS and the data…
In the digital age, where connectivity and data exchange play a crucial role, cybersecurity has become a paramount concern. The advent of 5G technology brings…
Jun 30, 2023Ravie LakshmananVulnerability / Software Security MITRE has released its annual list of the Top 25 “most dangerous software weaknesses” for the year 2023.…
North Korea-linked cyberespionage group Andariel used a previously undocumented malware called EarlyRat. Kaspersky researchers reported that the North Korea-linked APT group Andariel used a previously undocumented malware dubbed EarlyRat in attacks exploiting…