Polymarket users who had the site open during a short window on October 29 watched their positions get sold and their funds leave their wallets without doing anything themselves. The Polymarket hack did not start inside Polymarket.
It came through a small piece of code from an outside company that loaded on every visit to polymarket.com. The cryptocurrency-based prediction market now says it is returning $3.9 million to affected traders.
How the Polymarket Hack Worked
In a post-mortem published on October 31, Polymarket said a third-party vendor whose performance-monitoring script ran on polymarket.com had been compromised. The attacker swapped the vendor’s legitimate code for a compromised script built specifically to target Polymarket users.
The attacker did not need anyone’s password. For users who had the site open at the time, the malicious script used their active session to sell positions and move funds out of their wallets. Anyone logged in and browsing during that window was exposed. The vendor has publicly confirmed the compromise.
Polymarket’s status page first reported “unauthorized activity affecting user wallets” on October 29 and marked the incident as resolved later that day.
Who Was the Vendor Behind the Polymarket Hack?
Performance-monitoring company DebugBear released its own update on the incident. It said its initial findings point to its domain registrar as the point of entry.
“Our DNS records were compromised through our domain registrar,” the company said on X. “We are currently unable to receive emails sent to our domain. Based on our initial investigation this attack targeted the website of a specific customer.”
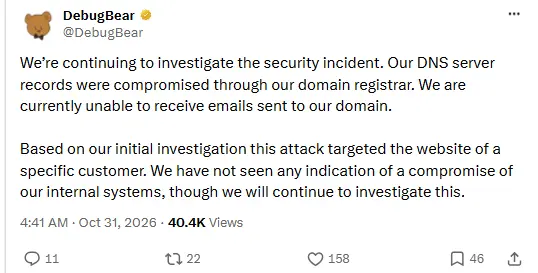
DebugBear added that it has “not seen any indication of a compromise of our internal systems,” though it is continuing to investigate.
This is the part of the story that should worry other website operators. According to the statements from both companies, the attacker appears to have gone after a vendor’s domain setup rather than Polymarket’s own systems, and used that position to put malicious code in front of Polymarket’s users. DebugBear’s own internal systems, by its account, show no sign of being breached.
How Polymarket Responded
Polymarket listed the steps it took once the attack was identified:
- Removed the vendor’s compromised script and cleared every cache.
- Paused trading and its relayer to stop further drains, then reopened once the site was clean.
- Reset all active login sessions.
- Began redeploying third-party scripts with added integrity controls and continuous monitoring, including a stronger content security policy, explicit version pinning and sandboxing.
- Referred the case to law enforcement while running its own investigation into the threat actor.
The trading pause stopped the bleeding, but it created a second set of losses for traders who were not directly hit by the script.
Where the Polymarket Hack Refunds Stand
Polymarket is returning $3.9 million in total. Of that, $2.7 million covers the initial losses from the attack, and $1.2 million covers losses tied to the hours-long shutdown.
As of its post-mortem, the company said 95% of affected wallets had been refunded in full, through a mix of reimbursements for drained wallets and goodwill payments.
The refunds cover more than drained wallets. Polymarket said it also made goodwill payments in two cases:
- Positions taken during the attack. If the script moved or force-sold a user’s positions, Polymarket will pay what they were worth when they were taken, including any slippage from the sale.
- Losses during the trading pause. If a user held a position when trading paused and it lost value because the market ended during the pause, or the user sold right after trading reopened, Polymarket covered the difference from its value at the pause.
Users do not need to file claims or tickets. Polymarket said it identified eligible wallets using on-chain and trading data. Anyone who thinks their amount is wrong, or believes they should have received a payment, can submit a form for the company to recheck.
What Remains Unanswered
Some questions are still open. Neither company has named the threat actor. DebugBear has said the attack targeted a single customer, but its investigation is ongoing, and it still cannot receive email sent to its domain. Polymarket has also not said exactly how many wallets were affected, only that 95% have been made whole.
The incident shows how much trust a website places in every outside script it loads. Polymarket’s own systems were not the entry point, yet its users still lost money, and it took a trading halt, a session reset and a removal of the vendor’s code to stop it.