Reportedly, the ShinyHunters extortion group breached the leak site of one of its competitors, the Clop ransomware gang.
ShinyHunters is a financially motivated cybercrime and extortion group active since 2019. It is known for stealing large volumes of data and pressuring victims to pay, rather than necessarily deploying ransomware. One recent high-profile organization targeted by the group was Instructure, the maker of Canvas LMS. ShinyHunters claimed it stole 3.65 TB of data belonging to about 9,000 academic institutions.
Clop, also written Cl0p, is a ransomware and data-extortion operation associated with large-scale exploitation of vulnerabilities in enterprise software and file-transfer platforms. In its recent campaign targeting PTC Windchill systems, it named more than 40 alleged victims, including Shell, Philips, Fiserv, Zebra Technologies, Ingersoll Rand, and Toast.
At the time of writing, the Clop dark web leak site looks like this:
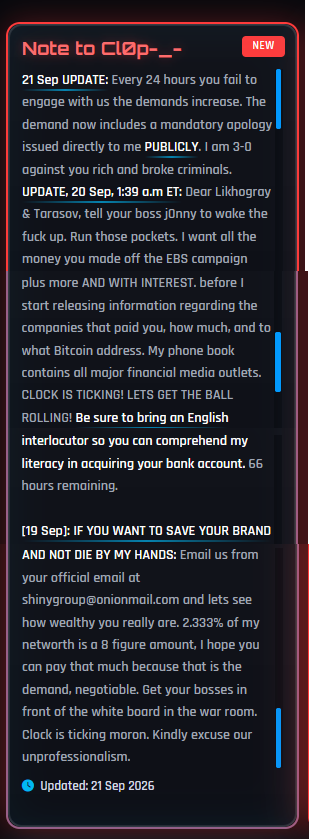
The rest of that page looks much the same as the ShinyHunters leak site, which includes this “Note to Cl0p”:
“Note to Cl0p_-
21 Sep UPDATE: Every 24 hours you fail to engage with us the demands increase. The demand now includes a mandatory apology issued directly to me PUBLICLY. I am 3-0 against you rich and broke criminals.
UPDATE, 20 Sep, 1:39 a.m ET: Dear Likhogray & Tarasov, tell your boss j0nny to wake the fuck up. Run those pockets. I want all the money you made off the EBS campaign plus more AND WITH INTEREST, before I start releasing information regarding the companies that paid you, how much, and to what Bitcoin address. My phone book contains all major financial media outlets. CLOCK IS TICKING! LETS GET THE BALL ROLLING! Be sure to bring an English interlocutor so you can comprehend my literacy in acquiring your bank account. 66 hours remaining.[19 Sep]: IF YOU WANT TO SAVE YOUR BRAND AND NOT DIE BY MY HANDS: Email us from your official email at shinygroup@onionmail.com and lets see how wealthy you really are. 2.333% of my networth is a 8 figure amount, I hope you can pay that much because that is the demand, negotiable. Get your bosses in front of the white board in the war room. Clock is ticking moron. Kindly excuse our unprofessionalism.
Updated: 21 Sep 2026”
BleepingComputer reports that the attack began Friday night when ShinyHunters exploited what it claims is an unauthenticated file-upload vulnerability in Grav CMS to upload a small text file to Clop’s site. Several hours later, ShinyHunters told BleepingComputer that it had “completely defaced” the site.
The group claimed it could continue controlling the address:
“We have their onion keys. So, if they kick us out it wouldn’t matter at all because we control the private keys to host the same exact onion URL.”
You might expect groups that make their money by exploiting unpatched vulnerabilities to be more vigilant about their own systems, but it looks as though they sometimes let their guard down.
According to ShinyHunters, this gang war began after ShinyHunters disrupted a Clop data-theft campaign. A Clop representative then allegedly threatened to identify ShinyHunters members and made violent threats against them.
ShinyHunters explained:
“During the Oracle EBS campaign they ran and stole from me last year, someone from cl0p personally messaged me and said, and I quote (translated from Russian): I have more money than you and all of your people combined, I’ll kill you soon.”
The good news is that while they are after each other, they probably have less time to attack legitimate businesses. I’m grabbing a bag of popcorn and watching this one unfold. We’ll keep you posted.
From reporting threats to removing them.
Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.