Sweet Security has announced the release of Virtual Patching, a new capability that protects running cloud and AI applications from specific vulnerabilities the moment they are identified. Security teams can enforce protection in one click while engineering develops, tests, and deploys a permanent fix.
Vulnerability remediation can take days or weeks as engineering teams develop fixes, test changes, obtain approvals, and deploy updated applications. During that window, the running application remains exposed. AI is making attacks faster and cheaper, increasing pressure on defenders whose response still depends on manual investigation, cross-team handoffs, and release schedules. A vulnerable workload left unprotected is not a theoretical risk. It is a target.
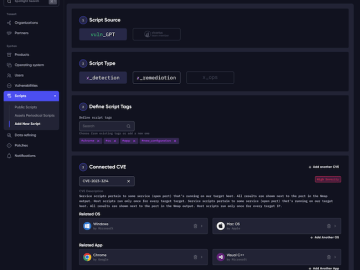
Sweet’s new Virtual Patching closes that window. From Sweet’s Vulnerabilities Catalog, a security team can identify a vulnerability, select Enforce protection, and deploy a policy to every node running that workload. The sensor applies it to the running application, blocking requests that attempt to exploit it while leaving normal traffic unaffected. Protection follows the workload as it scales and restarts. When a permanent fix is deployed, removing protection is equally simple.
“AI is accelerating vulnerability discovery and exploitation to the point where exploits are emerging days before patches are available; faster patching alone isn’t enough. Sweet’s Virtual Patching provides a critical layer of protection against known and unknown exploits, helping teams apply protection immediately while giving them the time they need to remediate vulnerabilities at their source,” said James Berthoty, CEO, Latio Tech.
“When a team knows an application can be exploited, waiting is not an option,” said Dror Kashti, CEO of Sweet Security. “Sweet’s new Virtual Patching gives security teams the ability to protect production immediately while engineering finishes the permanent fix. That changes the economics of cloud security by reducing the time and effort between identifying a risk and doing something about it.”
Virtual Patching works alongside Sweet Attack, Sweet’s autonomous AI red-team agent, which continuously validates exploitable attack paths using unmatched runtime context. When Sweet Attack identifies a vulnerability, it suggests a virtual patching policy the security team can enforce immediately. The result is a complete loop: Sweet Attack finds the exploit, the policy closes it, and the sensor enforces it at runtime.