
The Hacker’s Guide to Sneaking in Through the Back Door: A Second Order IDOR Adventure

Source link
Related Articles
All Mix →
Wallarm at OWASP Global AppSec DC 2023
Table of Contents Why OWASP 2023 Global AppSec Event? Meet Wallarm at the Event Why Choose Wallarm for API Security? Not Going to OWASP AppSec…
Concepts
This is one of my most ambitious projects, as it aims to capture everything I learn through reading, film, education, life experience, contemplation, etc. into…
Shopify Shares How Hackers Help to Secure $40B+ in Transactions
When Andrew Dunbar started at Shopify in 2012, he was the only security team member. Now, in his role as Director of Risk & Compliance,…

Jedox’s Journey with HackerOne: A Q&A with CTO, Vladislav Maličević
Vladislav Maličević is the Chief Technology Officer at Jedox, a leading global provider of cloud-based enterprise performance management solutions for Financial Planning and Analysis. Jedox…

New security test: CVE-2019-11043 PHP-FPM & NGINX RCE
Table of Contents What is Nginx/PHP-FPM RCE? Impact Details Remediation tl;dr – CVE-2019-11043 PHP-FPM & NGINX RCE was publicly disclosed and a Proof-of-Concept exploit code…
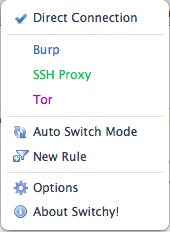
Three Proxy Options Every Security Pro Should Consider Using
Working in the information security field it’s frequently handy to be able to browse the web in different configurations. Sometimes you want to be able…